Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
UK NCSC Calls for Immediate Citrix NetScaler Vulnerability Patching

UK NCSC Calls for Immediate Citrix NetScaler Vulnerability Patching

Posted on September 28, 2026 By CWS

The UK National Cyber Security Centre (NCSC) has issued a critical advisory urging organizations to urgently address several vulnerabilities impacting Citrix NetScaler ADC and Gateway appliances. The call to action follows the discovery of two critical zero-day vulnerabilities, designated CVE-2026-88771 and CVE-2026-88772, which are actively being exploited by attackers.

Understanding the Citrix NetScaler Vulnerabilities

According to Citrix’s CTX697096 bulletin, the two most severe vulnerabilities possess a CVSS 4.0 score of 9.5. The first, CVE-2026-88771, is an improper input-validation flaw that allows remote attackers to execute arbitrary commands without authentication. This vulnerability exists across all vulnerable configurations of NetScaler, including those with default settings.

The second flaw, CVE-2026-88772, involves a memory overflow issue that can lead to either remote code execution or denial of service when DTLS is enabled, a feature that is typically active in VPN virtual servers by default.

Additional Security Weaknesses and Mitigations

The security update also addresses six further vulnerabilities that span various features of the affected systems. These include CVE-2026-88773, which allows HTTP request smuggling, and CVE-2026-88774 that can bypass certain policy controls. Memory-overflow vulnerabilities like CVE-2026-88775, CVE-2026-88776, and CVE-2026-88777 impact different server configurations, while CVE-2026-88778 poses risks with TCP sequence number prediction.

Organizations are advised to upgrade Citrix-managed cloud services and adaptive authentication systems, as well as to implement specific TCP configuration changes to address these vulnerabilities thoroughly.

Recommended Actions for Organizations

The NCSC emphasizes the need for organizations to consult Citrix’s detailed advisory and blog post to better understand the risks and necessary actions. Affected systems should be isolated if possible, and defenses should include blocking access via firewalls and restricting network connections to trusted IP addresses.

To ensure systems are not compromised, defenders are encouraged to preserve logs for forensic analysis, apply the latest patches, and verify all network nodes before restoring full service. It’s crucial for UK entities to report any confirmed breaches through the government’s cyber-incident reporting service.

Ensuring Long-term Security

Given the strategic position of NetScaler appliances in network architecture, successful exploitation could enable attackers to steal credentials and move laterally within networks. Therefore, post-patch monitoring, continuous threat intelligence updates, and regular security audits are essential.

Security teams should employ tools like File Integrity Monitoring to detect unauthorized changes and ensure logs are sent to an external SIEM for comprehensive analysis. In addition, specific vulnerabilities like CVE-2026-88778 require separate TCP configuration changes beyond just applying software updates.

Finally, Citrix users are advised to remain vigilant and proactive, continually monitoring for new threats and ensuring that all updates are applied across high-availability setups.
Cyber Security News Tags:Citrix, CVE, cyber security, cyber threats, NCSC, NetScaler, network security, patch management, remote code execution, Vulnerabilities

Post navigation

Previous Post: 2026 CISO Forum Virtual Summit Seeks Presentation Proposals
Next Post: Cross-Platform File Notification Attack Exposes User Activity

Related Posts

Threat Actors Using Fake Notepad++ and 7-zip Websites to Deploy Remote Monitoring Tools Threat Actors Using Fake Notepad++ and 7-zip Websites to Deploy Remote Monitoring Tools Cyber Security News
New PamStealer Malware Targets Mac Passwords New PamStealer Malware Targets Mac Passwords Cyber Security News
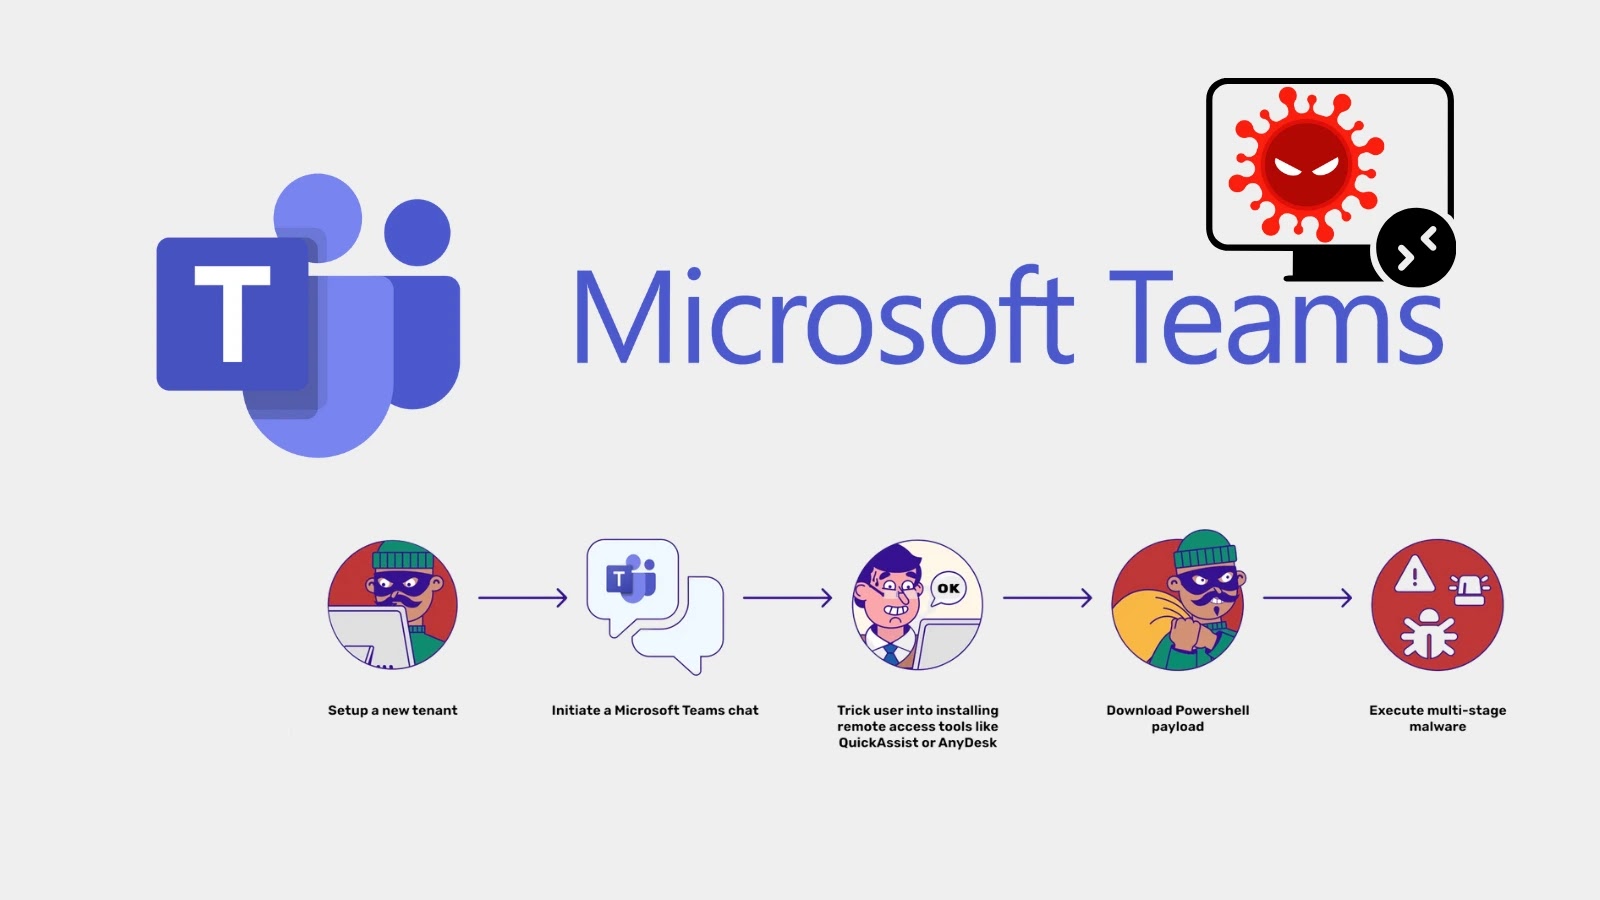
Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Cyber Security News
WhatsApp Usage May Require Active SIM Under New Rules WhatsApp Usage May Require Active SIM Under New Rules Cyber Security News
Tailscale SSH Vulnerabilities Risk Server Compromise Tailscale SSH Vulnerabilities Risk Server Compromise Cyber Security News
OnePlus Vulnerabilities Allow Root Access via OxygenOS OnePlus Vulnerabilities Allow Root Access via OxygenOS Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Lenovo Highlights Critical Server Security Vulnerability
  • Critical PTC Software Vulnerability Allows Remote Code Execution
  • Russian Hacker Linked to Qilin Ransomware Operations
  • Inside the Google Session Phishing Campaign via Calendar Invites
  • AWS Resolves MCP Gateway Vulnerability Exposing Cloud Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Lenovo Highlights Critical Server Security Vulnerability
  • Critical PTC Software Vulnerability Allows Remote Code Execution
  • Russian Hacker Linked to Qilin Ransomware Operations
  • Inside the Google Session Phishing Campaign via Calendar Invites
  • AWS Resolves MCP Gateway Vulnerability Exposing Cloud Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark