
Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Cross-Platform File Notification Attack Exposes User Activity

Cross-Platform File Notification Attack Exposes User Activity

Posted on September 28, 2026 By CWS

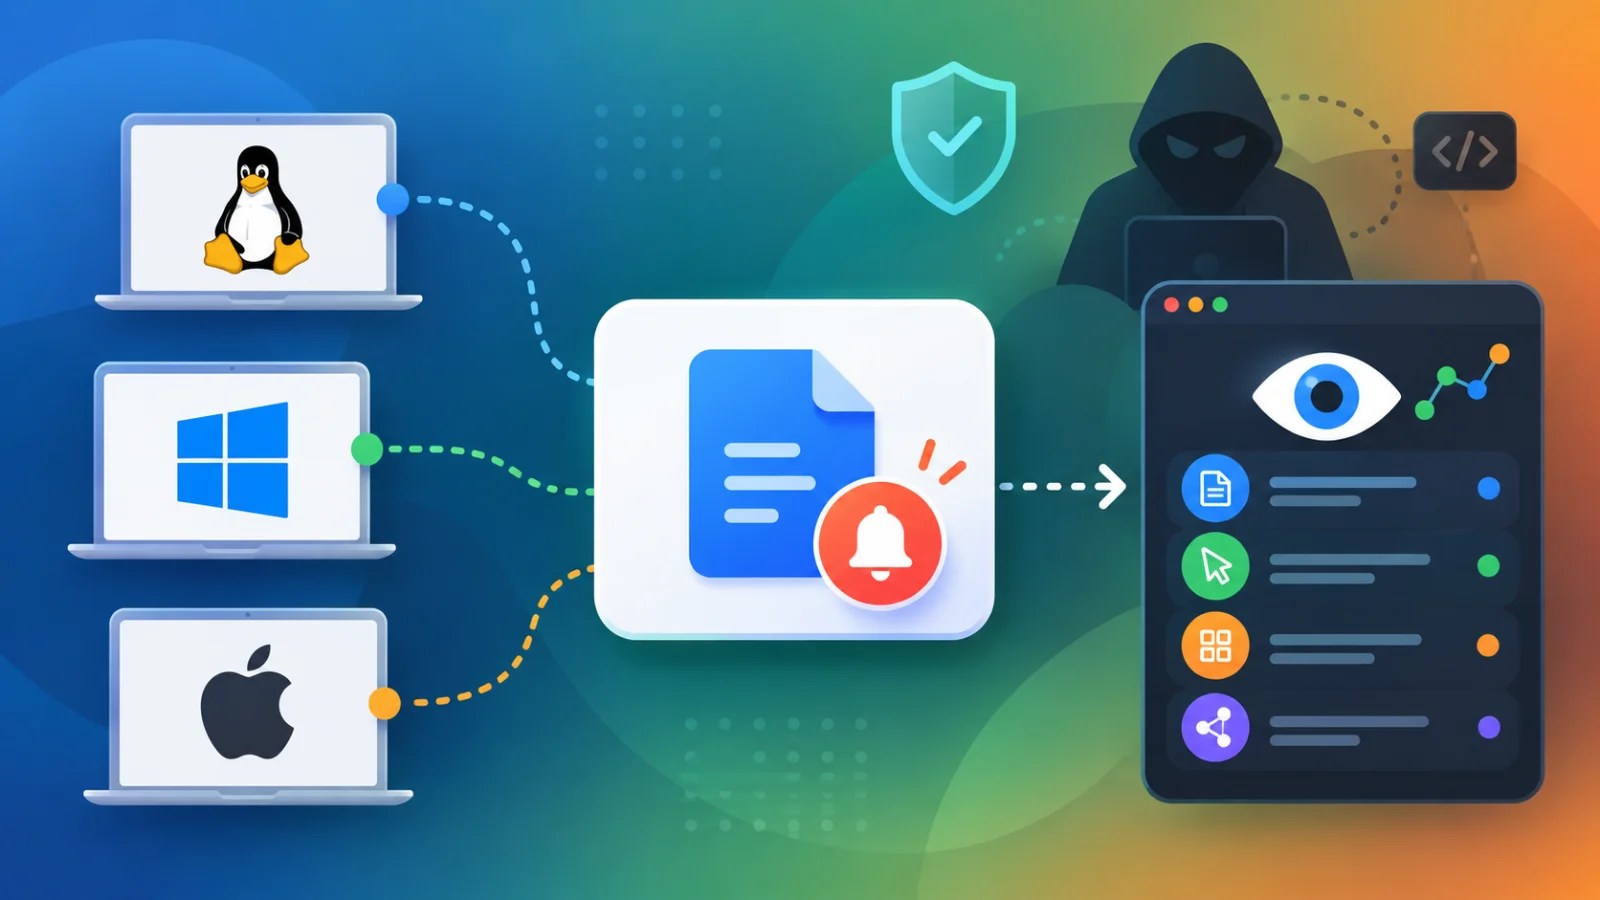
A novel side-channel attack capable of tracking user activities across Linux, Windows, and macOS has been uncovered, leveraging file-notification services such as inotify, ReadDirectoryChangesW, and FSEvents. This technique uses these services, which traditionally alert applications to file changes, as monitoring tools without the need for elevated privileges.

Research Origins and Methodology

This discovery stems from a study conducted by researchers at Graz University of Technology, titled “File Notification Attacks: Templating and Exploiting Side-Channel Leakage from the File-Notification Systems on Linux, Windows, and macOS.” The researchers developed a templating process to record filesystem events linked with various user actions.

These templates can discern a wide range of activities, including terminal commands, input from keyboard and mouse, website visits, web-server activity, and more. The attack does not exploit memory corruption but instead observes the timing and paths of legitimate operating-system notifications.

Implications for Different Operating Systems

On Linux, the attack exploits inotify’s ability to report file-access events, enabling the detection of keystroke timing with high accuracy. It can also efficiently monitor SSH pseudo-terminal activity. On Windows, the attack allows an unprivileged user to access file paths within another user’s profile, revealing visited domains through browser storage paths.

MacOS, while slightly more resilient due to its restrictions on monitoring private directories, still exposes application launches and network activity. The average latency on macOS is slower compared to the other systems, yet remains effective for behavioral analysis.

Security Implications and Recommendations

The attack represents a significant threat in terms of post-compromise surveillance, allowing malware to infer user behaviors without direct file access. Although researchers disclosed these findings to major operating system vendors in October 2025, responses have varied. Linux has implemented partial mitigations, whereas Microsoft regards the behavior as intended.

The study suggests that filenames, access timing, and notification metadata should be considered sensitive. Enhanced permission checks, sandboxing applications, and updating operating systems are recommended to mitigate exposure. The potential for false interpretations exists when different activities create similar filesystem patterns.

In conclusion, while the attack does not allow remote compromise, it underscores the need for improved security in file-notification systems to protect user privacy and system integrity.
Cyber Security News Tags:Cybersecurity, file notification, Linux, macOS, Privacy, security research, side-channel attack, system monitoring, tech news, user activity, Windows

Post navigation

Previous Post: UK NCSC Calls for Immediate Citrix NetScaler Vulnerability Patching

Related Posts

Apache Log4j Vulnerability Allow Attackers to Intercept Sensitive Log Data Apache Log4j Vulnerability Allow Attackers to Intercept Sensitive Log Data Cyber Security News
Qilin Ransomware Leveraging Mspaint and Notepad to Find Files with Sensitive Information Qilin Ransomware Leveraging Mspaint and Notepad to Find Files with Sensitive Information Cyber Security News
Turla’s Advanced Espionage Operations in Ukraine Uncovered Turla’s Advanced Espionage Operations in Ukraine Uncovered Cyber Security News
OpenAI Astra AI Uncovers Zero-Day Security Threats OpenAI Astra AI Uncovers Zero-Day Security Threats Cyber Security News
Microsoft’s Record M Bug Bounty Payout Microsoft’s Record $20M Bug Bounty Payout Cyber Security News
Ubiquiti UniFi Flaws Risk Total System Compromise Ubiquiti UniFi Flaws Risk Total System Compromise Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Cross-Platform File Notification Attack Exposes User Activity
  • UK NCSC Calls for Immediate Citrix NetScaler Vulnerability Patching
  • 2026 CISO Forum Virtual Summit Seeks Presentation Proposals
  • Bitget Security Breach Results in $387 Million Loss
  • Nvidia Launches AI Safety Platform with Hardware Watchdog

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Cross-Platform File Notification Attack Exposes User Activity
  • UK NCSC Calls for Immediate Citrix NetScaler Vulnerability Patching
  • 2026 CISO Forum Virtual Summit Seeks Presentation Proposals
  • Bitget Security Breach Results in $387 Million Loss
  • Nvidia Launches AI Safety Platform with Hardware Watchdog

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark