
Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Octopus Server Vulnerability Exposed

Critical Octopus Server Vulnerability Exposed

Posted on September 30, 2026 By CWS

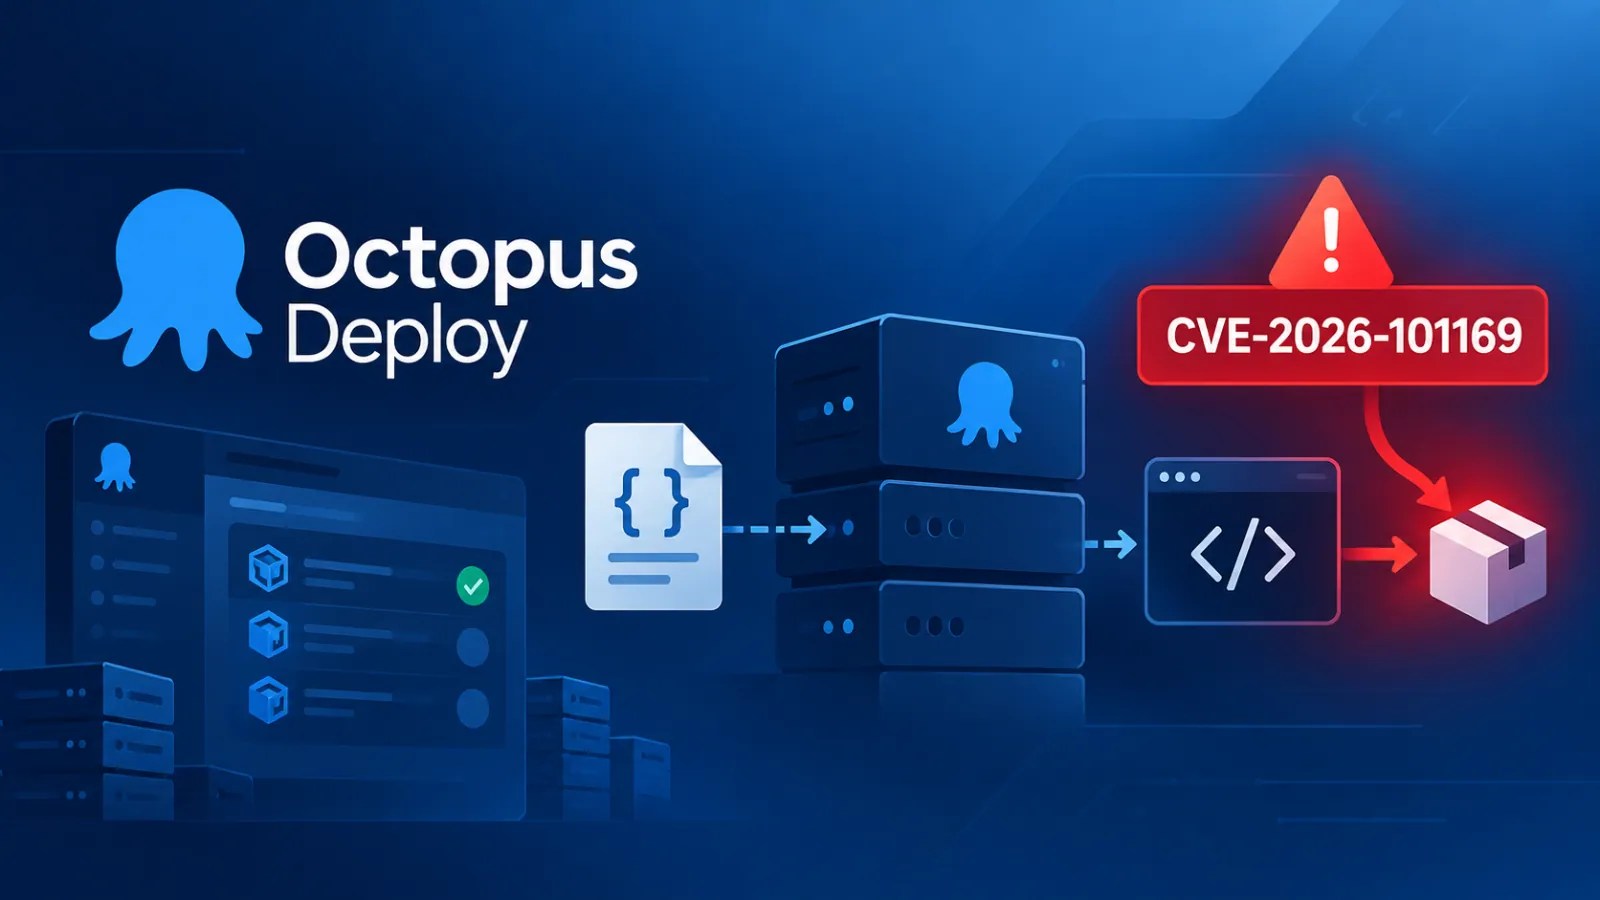
Octopus Deploy has identified a serious security vulnerability in its Octopus Server software, impacting both Linux and Windows installations. This flaw, known as CVE-2026-101169, enables authenticated users to execute arbitrary code through insecure JSON deserialization.

Details of the Vulnerability

In a security advisory released on September 29, 2026, Octopus Deploy urged immediate updates due to the absence of available mitigations for this issue. The vulnerability was discovered by Nathan Willoughby during internal testing on September 4, 2026, and patches followed on September 14, 2026.

The flaw arises from how Octopus Server handles JSON content related to Environment and Project objects. An attacker with valid credentials and editing permissions can craft malicious JSON data, leading to arbitrary code execution during deserialization.

Potential Impact on Enterprises

This vulnerability could have significant consequences in enterprise environments where Octopus Server is utilized for deployment processes. Attackers could gain access to deployment credentials, automate workflows, and sensitive configuration data, depending on the server’s permissions.

If successfully exploited, the flaw could allow malicious actors or compromised administrator accounts to execute code within the security context of the Octopus Server process, with the impact varying based on assigned privileges and server access.

Patch and Prevention Measures

The affected versions include all Octopus Server releases from 2019.4.x to 2026.4.x. Customers using versions older than 2026.3.15829 should upgrade immediately. The latest secure version is 2026.3.15863. For Octopus Cloud users, no action is required as updates have already been applied.

Octopus Deploy strongly recommends organizations to update their servers to the latest stable version to prevent potential exploitation. For legacy versions, upgrading to a recommended fixed release is advised.

Despite the severity, Octopus Deploy has not reported any known exploitation or misuse of the CVE-2026-101169 vulnerability at the time of this announcement.

Organizations are encouraged to enhance their security measures and ensure timely software updates to protect against such vulnerabilities.
Cyber Security News Tags:CVE-2026-101169, Cybersecurity, JSON deserialization, Linux, Octopus Server, security advisory, security flaw, software patch, Vulnerability, Windows

Post navigation

Previous Post: Tech Leaders Agree to Self-Regulate on AI Development
Next Post: OpenSSL Patches Critical DTLS Vulnerability

Related Posts

GitLab Patches Multiple Vulnerabilities that Allows Attackers to Trigger XSS and DoS Attack GitLab Patches Multiple Vulnerabilities that Allows Attackers to Trigger XSS and DoS Attack Cyber Security News
Windows 11 Update KB5077181 Triggers Endless Reboot Issues Windows 11 Update KB5077181 Triggers Endless Reboot Issues Cyber Security News
Top Simulated DDoS Testing Tools for 2026 Top Simulated DDoS Testing Tools for 2026 Cyber Security News
OverlayPhantom Trojan Exploits Android Devices OverlayPhantom Trojan Exploits Android Devices Cyber Security News
Dgraph Database Flaw Endangers Security with Bypass Vulnerability Dgraph Database Flaw Endangers Security with Bypass Vulnerability Cyber Security News
Microsoft Data Center Outage Affects Windows 11 Updates Microsoft Data Center Outage Affects Windows 11 Updates Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Does AI Hinder Cybersecurity Efforts?
  • Microsoft Alerts on Phishing Exploits Amid 365 Service Disruption
  • Critical UnrealIRCd Flaw Allows Server Command Injection
  • FBI Warns of Rapid ARTEX AI Hacks Achieving Access in Hours
  • Leaked Key Triggers Security Breach in Cursor’s Marketplace

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Does AI Hinder Cybersecurity Efforts?
  • Microsoft Alerts on Phishing Exploits Amid 365 Service Disruption
  • Critical UnrealIRCd Flaw Allows Server Command Injection
  • FBI Warns of Rapid ARTEX AI Hacks Achieving Access in Hours
  • Leaked Key Triggers Security Breach in Cursor’s Marketplace

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark