Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Cybercriminals Exploit ChatGPT for Malware Distribution

Cybercriminals Exploit ChatGPT for Malware Distribution

Posted on September 30, 2026 By CWS

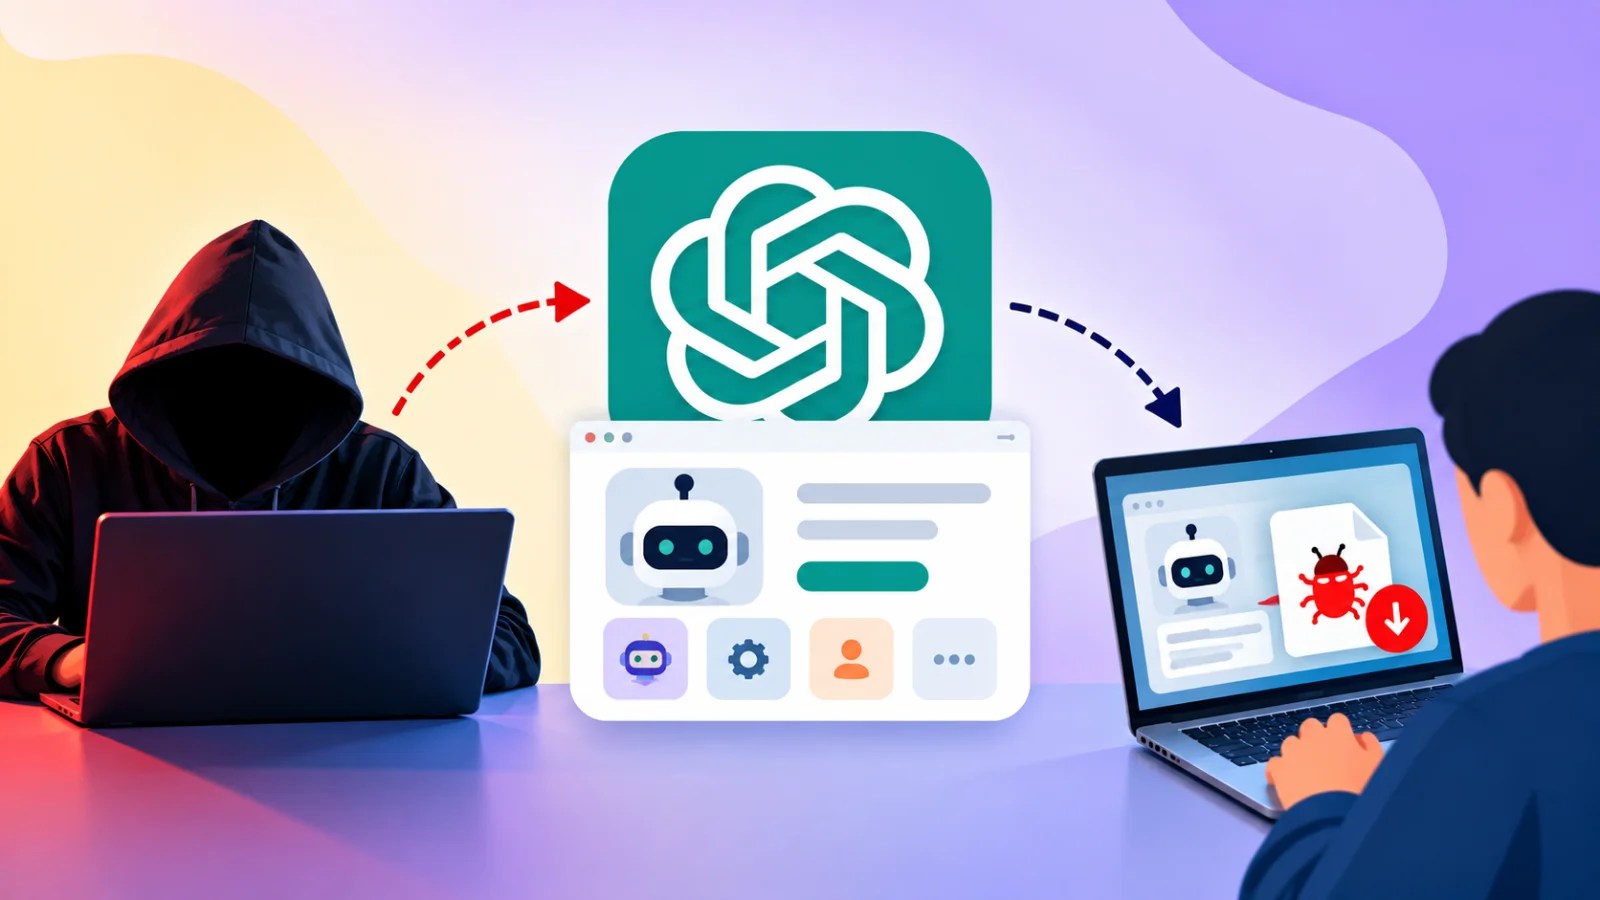
Security researchers from Huntress have uncovered a new method employed by hackers to misuse ChatGPT’s Custom GPT feature for distributing malware. This campaign leverages trusted ChatGPT-hosted pages to deploy a sophisticated remote access trojan (RAT), posing significant risks to users.

Deceptive Techniques and Attack Strategy

The attackers use a combination of malvertising and fake verification prompts to initiate the attack. They employ obfuscated PowerShell scripts, malicious MSI packages, and DLL sideloading to execute their malicious intent. According to Huntress, the campaign has utilized Google Sites infrastructure in at least 40 incidents, including two traced back to malicious Custom GPTs.

The attack often begins when unsuspecting users search for “chatgpt” on Google and click on a sponsored link that directs them to a deceptive chatgpt.com page. The attackers creatively named their Custom GPT “Plus 5.6,” imitating an official model, although it was identified as a creation by a “community builder.”

Execution and Impact of the Attack

Once users interact with the fake page, they encounter a “Service Availability Notice” that misleadingly alerts them about limited access to the main domain. They are then redirected to a Google Sites page masquerading as a ChatGPT and Cloudflare CAPTCHA verification screen. Here, the ClickFix lure tricks victims into running a PowerShell command.

The command leads to downloading a heavily obfuscated PowerShell script into the system’s temporary directory. This script, after decoding, installs a malicious MSI file, disguises itself as “Advanced Printer Configuration Reader,” and hides from the Programs and Features list.

Technical Analysis and Defensive Measures

In this complex attack chain, the MSI file utilizes DLL sideloading techniques to execute further malicious activities. It loads a Canon-signed executable, which then runs a modified DLL, initiating the RAT’s installation. The malware is capable of remote desktop access, capturing audio and video, and executing additional malicious payloads.

Huntress emphasizes the importance of behavioral detection over reliance on product names, as attackers can easily rotate signed host applications. Key indicators include unexpected PowerShell activity and the execution of signed binaries from atypical paths.

Users are advised to immediately close any pages requesting them to execute shell commands, as legitimate verification processes do not require such actions. The research credits the contributions of several Huntress team members for their investigative efforts.

In conclusion, as cybercriminals continue to innovate in their methods, it is crucial for both users and security professionals to stay informed and vigilant against such sophisticated threats.
Cyber Security News Tags:ChatGPT, ClickFix, Custom GPT, Cybersecurity, DLL Sideloading, Google Sites, Hackers, Huntress, IT security, Malvertising, Malware, OpenAI, PowerShell, RAT

Post navigation

Previous Post: GitHub AI Uncovers 24 Security Flaws in Android Apps
Next Post: Tech Leaders Agree to Self-Regulate on AI Development

Related Posts

Beware of Fake Bitcoin Tool That Hides DarkComet RAT Malware With it Beware of Fake Bitcoin Tool That Hides DarkComet RAT Malware With it Cyber Security News
FBI and Indonesian Police Dismantle Global Phishing Network FBI and Indonesian Police Dismantle Global Phishing Network Cyber Security News
New Windows Backdoor SLEEPWALKER Evades Detection New Windows Backdoor SLEEPWALKER Evades Detection Cyber Security News
Critical Bug in WordPress Plugin Risks 400,000 Sites Critical Bug in WordPress Plugin Risks 400,000 Sites Cyber Security News
AI-Driven Ransomware Attack Exploits VPNs and Databases AI-Driven Ransomware Attack Exploits VPNs and Databases Cyber Security News
Coyote Malware Abuses Microsoft’s UI Automation in Wild to Exfiltrate Login Credentials Coyote Malware Abuses Microsoft’s UI Automation in Wild to Exfiltrate Login Credentials Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google Chrome Update Patches 247 Security Vulnerabilities
  • Critical Atlassian Vulnerability Fixed Across Key Products
  • 32 Zero-Day Vulnerabilities Exploited at Pwn2Own 2026
  • Wikimedia Identifies Unauthorized OpenAI Agent Activities
  • Over 100 Sites Compromised Using Fake Cloudflare Checks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google Chrome Update Patches 247 Security Vulnerabilities
  • Critical Atlassian Vulnerability Fixed Across Key Products
  • 32 Zero-Day Vulnerabilities Exploited at Pwn2Own 2026
  • Wikimedia Identifies Unauthorized OpenAI Agent Activities
  • Over 100 Sites Compromised Using Fake Cloudflare Checks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark