Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Docker Flaw Enables Host File Overwrite

Critical Docker Flaw Enables Host File Overwrite

Posted on October 1, 2026 By CWS

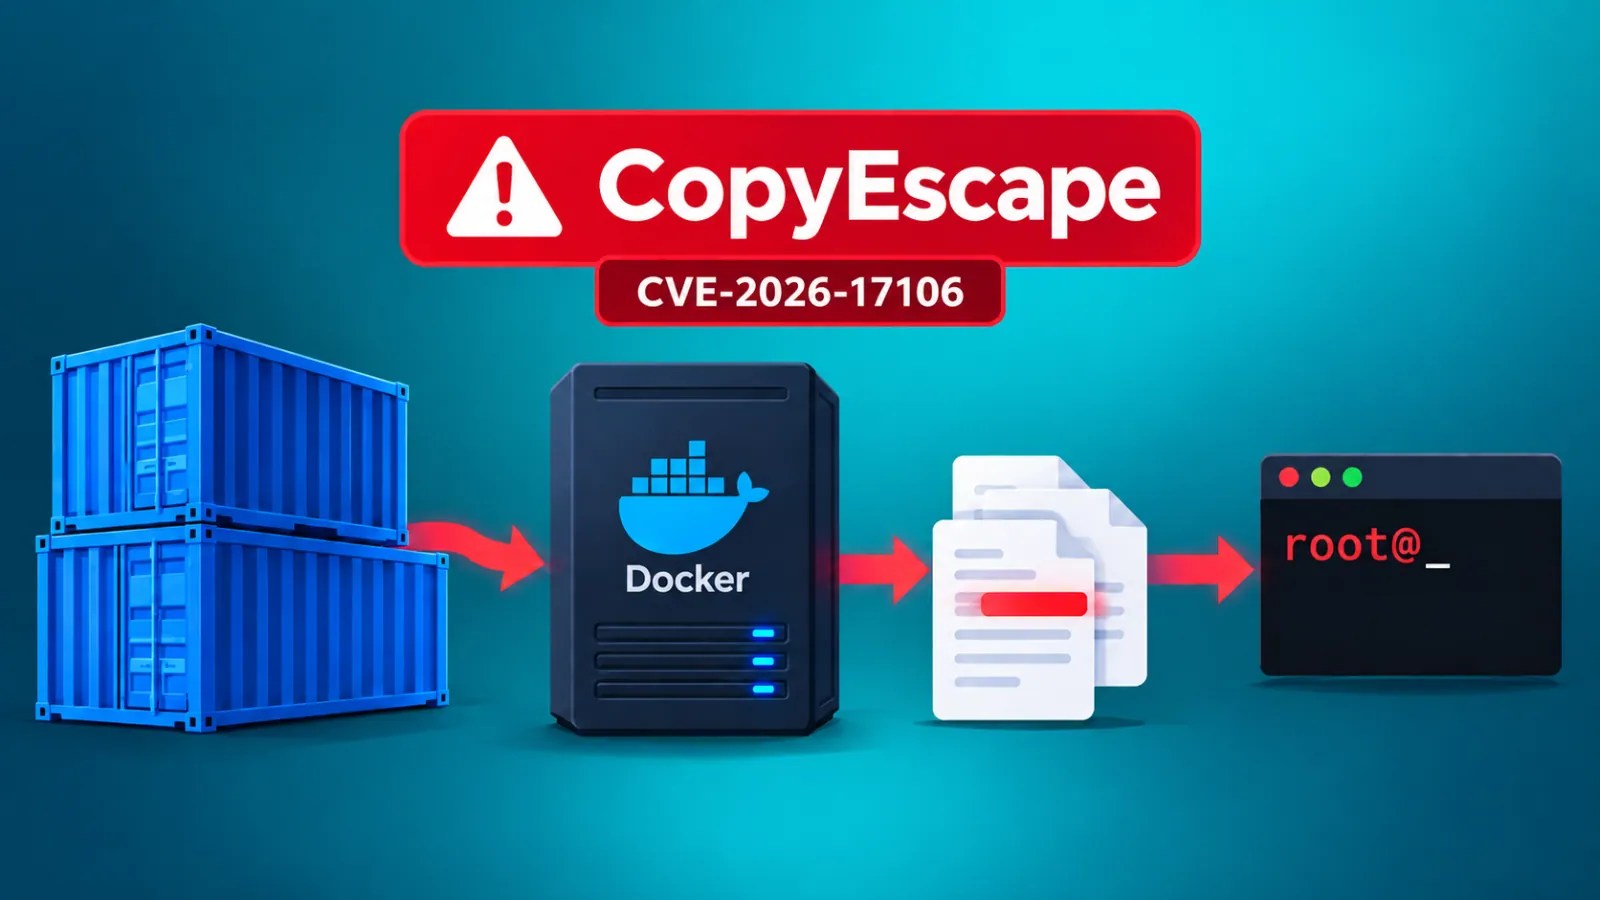
A newly discovered vulnerability in Docker, identified as CVE-2026-17106 and referred to as CopyEscape, poses a significant security threat by allowing malicious containers to overwrite host files and potentially execute code with root-level privileges.

Understanding the Vulnerability

This flaw stems from the way Docker handles archive extraction within moby/go-archive. When files are copied from a container to a host, Docker packages these files into a tar archive, which the local Docker CLI then extracts. This process can be exploited if an attacker controls the container, potentially inserting a symlink that redirects file writes outside the intended directory.

The main exploit, as described by Imperva, leverages a race condition during archive generation. This allows a running container to alter a directory into a symbolic link, creating an inconsistent archive that Docker CLI follows improperly during file extraction.

Impact on Systems

The consequences of this vulnerability are severe, especially on Linux systems where Docker cp is often run with elevated privileges. An attacker could replace critical files such as shell startup scripts or cloud credentials, leading to unauthorized code execution.

On macOS, although Docker Desktop operates within a Linux VM, the vulnerability still poses risks to local user files. Imperva’s proof of concept demonstrated the replacement of critical binaries with malicious scripts, executing payloads with root permissions once invoked by Docker.

Mitigation and Recommendations

To address this issue, Docker has released updates for its products. Docker Desktop version 4.86.0 and moby/go-archive version 0.3.0 contain fixes that mitigate the vulnerability. Organizations are advised to upgrade to these versions or later to secure their systems.

In the interim, administrators should avoid copying files from untrusted or compromised containers. Stopping a container before executing docker cp can help prevent exploitation. Additionally, using disposable virtual machines or isolated environments for handling suspicious container data is recommended.

The CopyEscape flaw underscores the importance of treating archive extraction as a security boundary, highlighting how routine operations can be exploited if not properly secured.

For ongoing protection, organizations should continuously monitor for updates and follow security best practices to mitigate potential threats posed by container-based environments.
Cyber Security News Tags:archive extraction, container security, CopyEscape, CVE-2026-17106, Cybersecurity, Docker, Docker cp, Docker Desktop, file overwrite, Imperva, Linux, macOS, root access, security flaw

Post navigation

Previous Post: MetaMask Security Issue Leads to Validator Withdrawal
Next Post: Apple CoreGraphics Flaw: WhatsApp’s Potential Role Analyzed

Related Posts

Threat Intelligence That Powers Best SOCs Worldwide Is Now Free   Threat Intelligence That Powers Best SOCs Worldwide Is Now Free   Cyber Security News
Critical InputPlumber Vulnerabilities Allows UI Input Injection and Denial-of-Service Critical InputPlumber Vulnerabilities Allows UI Input Injection and Denial-of-Service Cyber Security News
Russian Cybercrime Market Hub Transferring from RDP Access to Malware Stealer Logs to Access Russian Cybercrime Market Hub Transferring from RDP Access to Malware Stealer Logs to Access Cyber Security News
AMD Warns of Transient Scheduler Attacks Affecting Wide Range of Chipsets AMD Warns of Transient Scheduler Attacks Affecting Wide Range of Chipsets Cyber Security News
Supply Chain Attack Compromises Popular Python Package Supply Chain Attack Compromises Popular Python Package Cyber Security News
Critical Zoom Vulnerabilities in Windows Prompt Immediate Updates Critical Zoom Vulnerabilities in Windows Prompt Immediate Updates Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark