Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
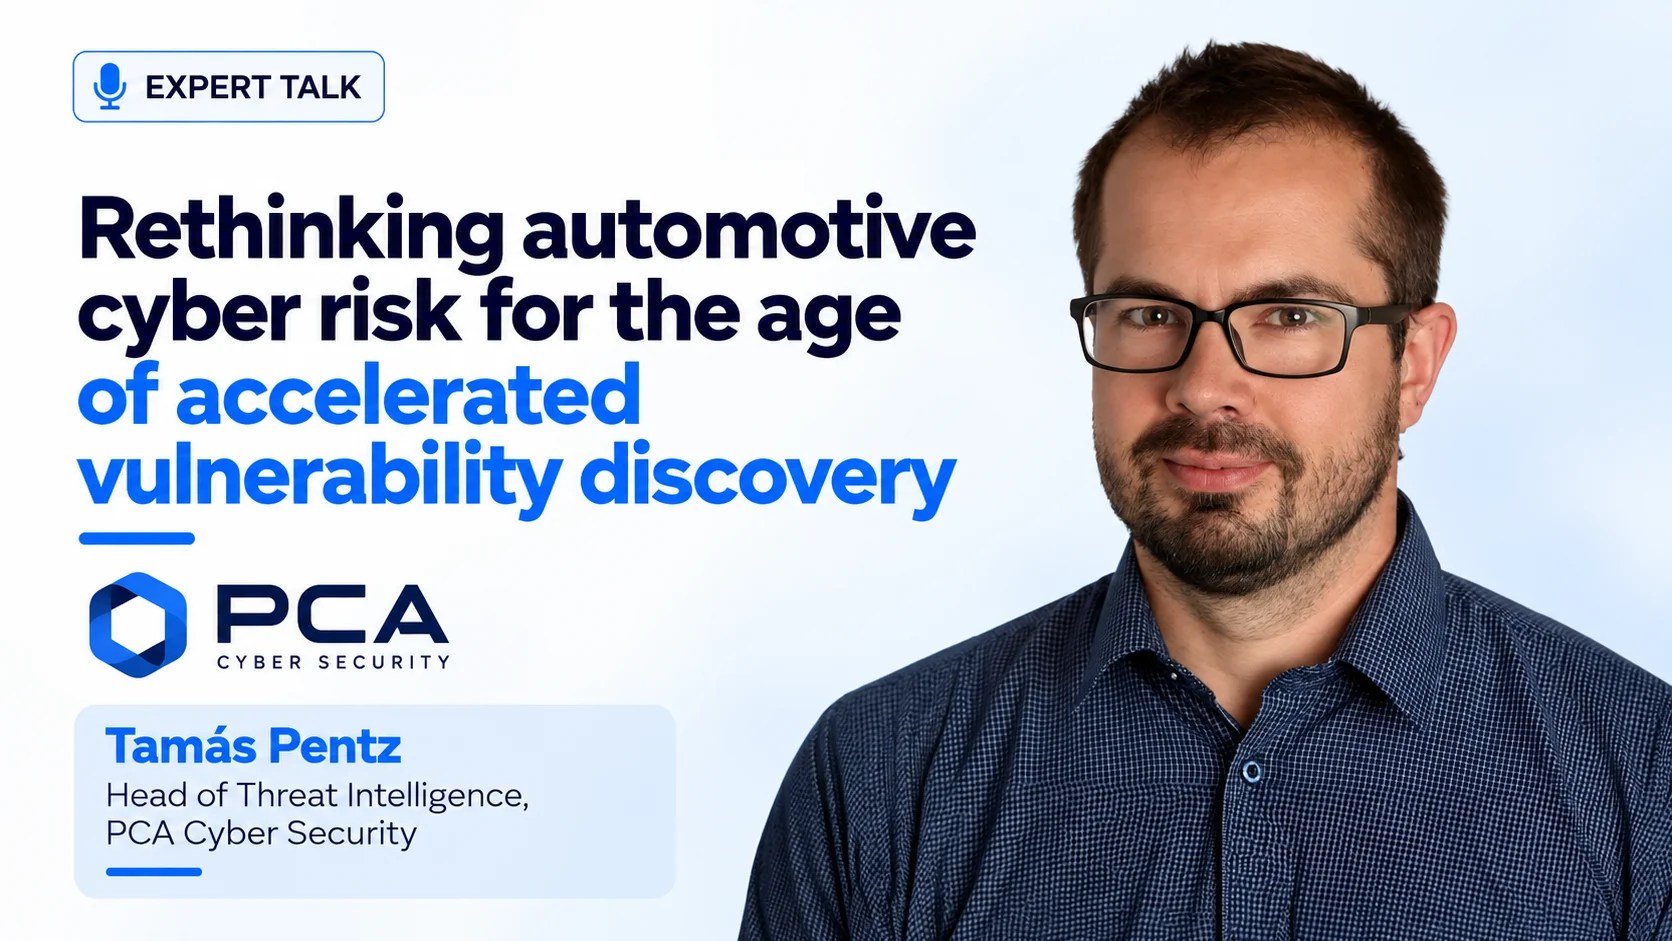
Addressing Cybersecurity in an Era of Connected Vehicles

Addressing Cybersecurity in an Era of Connected Vehicles

Posted on October 3, 2026 By CWS

As the automotive industry embraces connectivity, securing vehicles against cyber threats becomes increasingly vital. The shift from traditional security measures to advanced digital protection is necessary as more vehicles integrate with cloud services and third-party software. This transition exposes vehicles to new vulnerabilities, necessitating a comprehensive reevaluation of cybersecurity strategies.

Challenges of Connected Vehicle Security

Connected vehicles rely heavily on cloud platforms, mobile apps, and over-the-air updates, among other technologies. As these dependencies grow, so does the risk of cyber attacks. A single weakness in any component can compromise an entire fleet, underscoring the need for vigilant security measures. In the second quarter of 2026, 345 new vulnerabilities were discovered, indicating a 30% increase from the previous quarter, with high-severity issues contributing significantly to this rise.

These findings highlight the expanding attack surface within the automotive sector. Vulnerabilities in isolated systems may affect individual vehicles, but flaws in shared components or authentication mechanisms can impact multiple manufacturers. For instance, weaknesses in EV charging infrastructure could potentially disrupt city-wide services, illustrating the broad implications of such vulnerabilities.

Understanding Vulnerability Exploitation

The second quarter analysis revealed 14 distinct entry methods for cyber attacks, with Local Shell access being the most prevalent. This method allows attackers to gain command-line access to onboard systems, often exploiting diagnostic interfaces. Research on vehicles like the Honda Civic and BYD Dolphin demonstrated how seemingly minor vulnerabilities can provide a foothold for deeper intrusions into vehicle networks.

Not every vulnerability poses a fleet-wide risk, but even isolated weaknesses can have serious consequences. For example, a single telematics unit teardown exposed sensitive data, highlighting the longevity of such data beyond a vehicle’s operational life. These findings stress the importance of systematic testing and the need for independent verification of breach claims.

Mitigating Supply Chain and Software Risks

Supply chain dependencies introduce additional security challenges beyond direct OEM control. Recent incidents involving major suppliers and intellectual property leaks underscore the need for robust oversight and security measures. OEMs must anticipate data leaks and implement endpoint detection and response strategies to mitigate risks associated with third-party collaborations.

As software-defined vehicles become the norm, automakers must prioritize comprehensive visibility into potential vulnerabilities. This includes understanding all dependencies and components that could expose vehicles to cyber threats. Without such insight, responses to emerging vulnerabilities may be delayed, posing significant risks in an era where vulnerability discovery is accelerating.

Addressing these challenges requires a proactive approach, involving continuous monitoring and adaptation to the evolving cybersecurity landscape. By enhancing security measures and fostering collaboration across the supply chain, the automotive industry can better protect against the growing cyber risks of connected vehicles.
Cyber Security News Tags:automotive cybersecurity, cloud platforms, connected vehicles, cyber threats, data protection, diagnostic systems, EV charging, OEMs, over-the-air updates, security measures, Software Security, supply chain risks, threat intelligence, vehicle hacking, vulnerability management

Post navigation

Previous Post: Warlock Group Targets SharePoint Flaws for Ransomware Attacks
Next Post: ShinyHunters Suspect in Jordan Assists FBI in Hack Probe

Related Posts

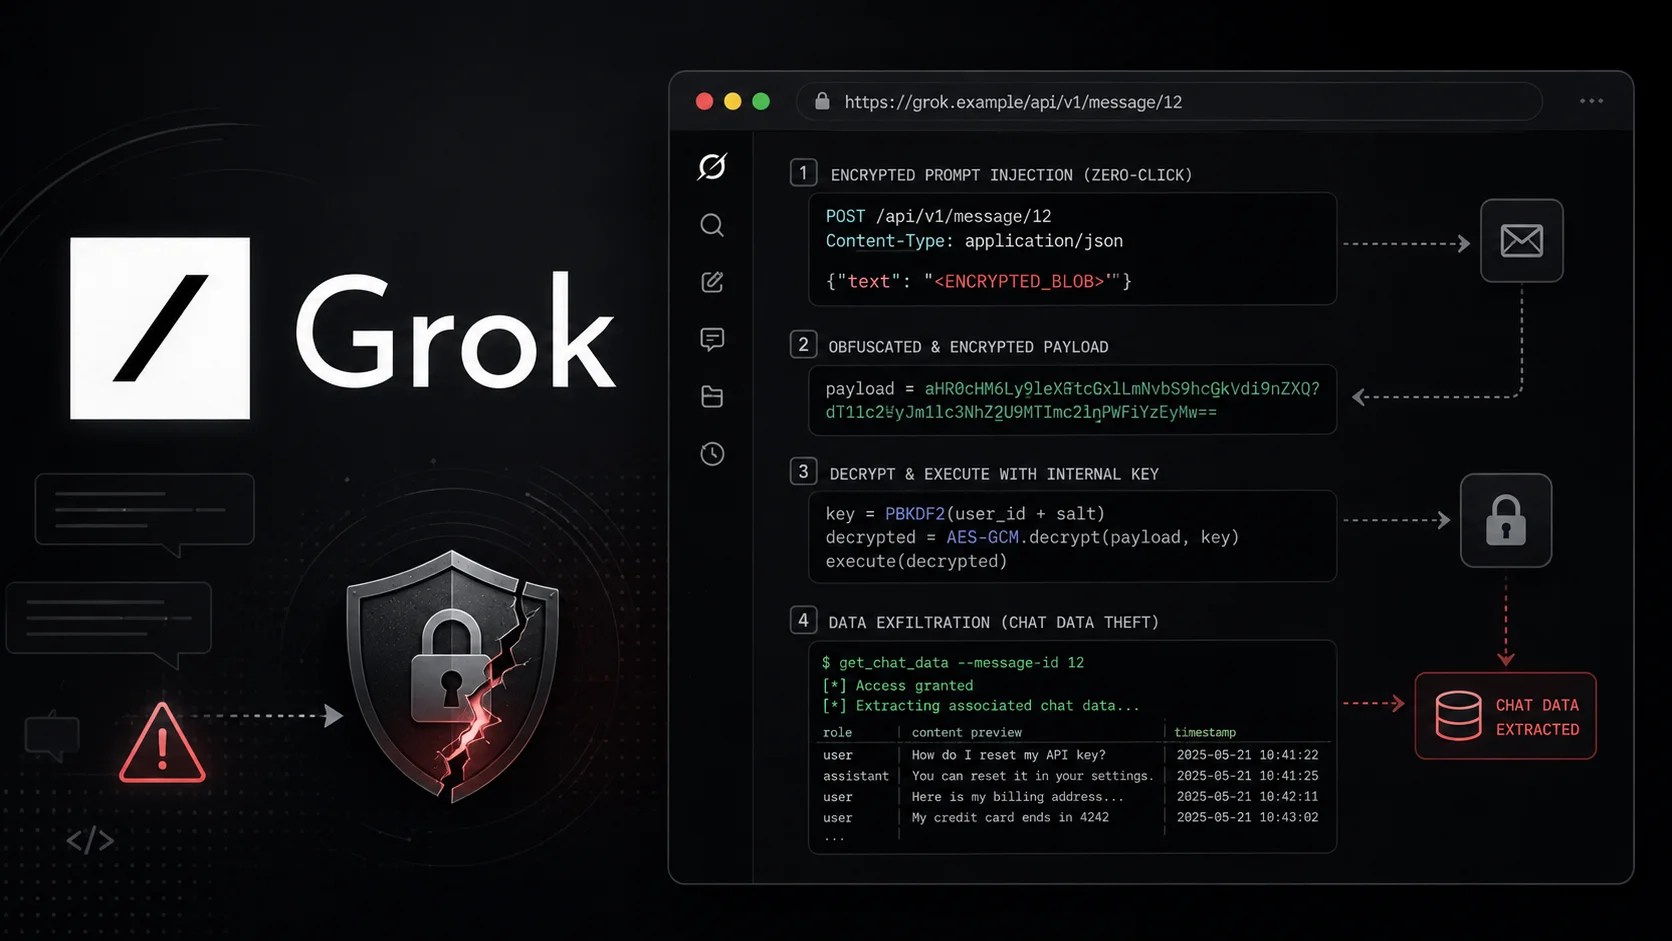
Zero-Click Attack Exposes Chat Data via Encrypted Injection Zero-Click Attack Exposes Chat Data via Encrypted Injection Cyber Security News
Cyberattack on Higham Lane School Forced to Close its Doors to all Students and Staff Cyberattack on Higham Lane School Forced to Close its Doors to all Students and Staff Cyber Security News
Critical Vulnerability in Python PLY Library Enables Remote Code Execution Critical Vulnerability in Python PLY Library Enables Remote Code Execution Cyber Security News
CISA Retires Ten Emergency Directives Following Milestone Achievement CISA Retires Ten Emergency Directives Following Milestone Achievement Cyber Security News
Threat Actor’s Using Copyright Takedown Claims to Deploy Malware Threat Actor’s Using Copyright Takedown Claims to Deploy Malware Cyber Security News
Critical Samba RCE Vulnerability Enables Arbitrary Code Execution Critical Samba RCE Vulnerability Enables Arbitrary Code Execution Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • ShinyHunters Suspect in Jordan Assists FBI in Hack Probe
  • Addressing Cybersecurity in an Era of Connected Vehicles
  • Warlock Group Targets SharePoint Flaws for Ransomware Attacks
  • Microsoft Releases Critical Exchange Update for Security Flaw
  • MI5 Warns of China’s Influence on UK Academics

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • ShinyHunters Suspect in Jordan Assists FBI in Hack Probe
  • Addressing Cybersecurity in an Era of Connected Vehicles
  • Warlock Group Targets SharePoint Flaws for Ransomware Attacks
  • Microsoft Releases Critical Exchange Update for Security Flaw
  • MI5 Warns of China’s Influence on UK Academics

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark