Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher K

Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Posted on October 4, 2026 By CWS

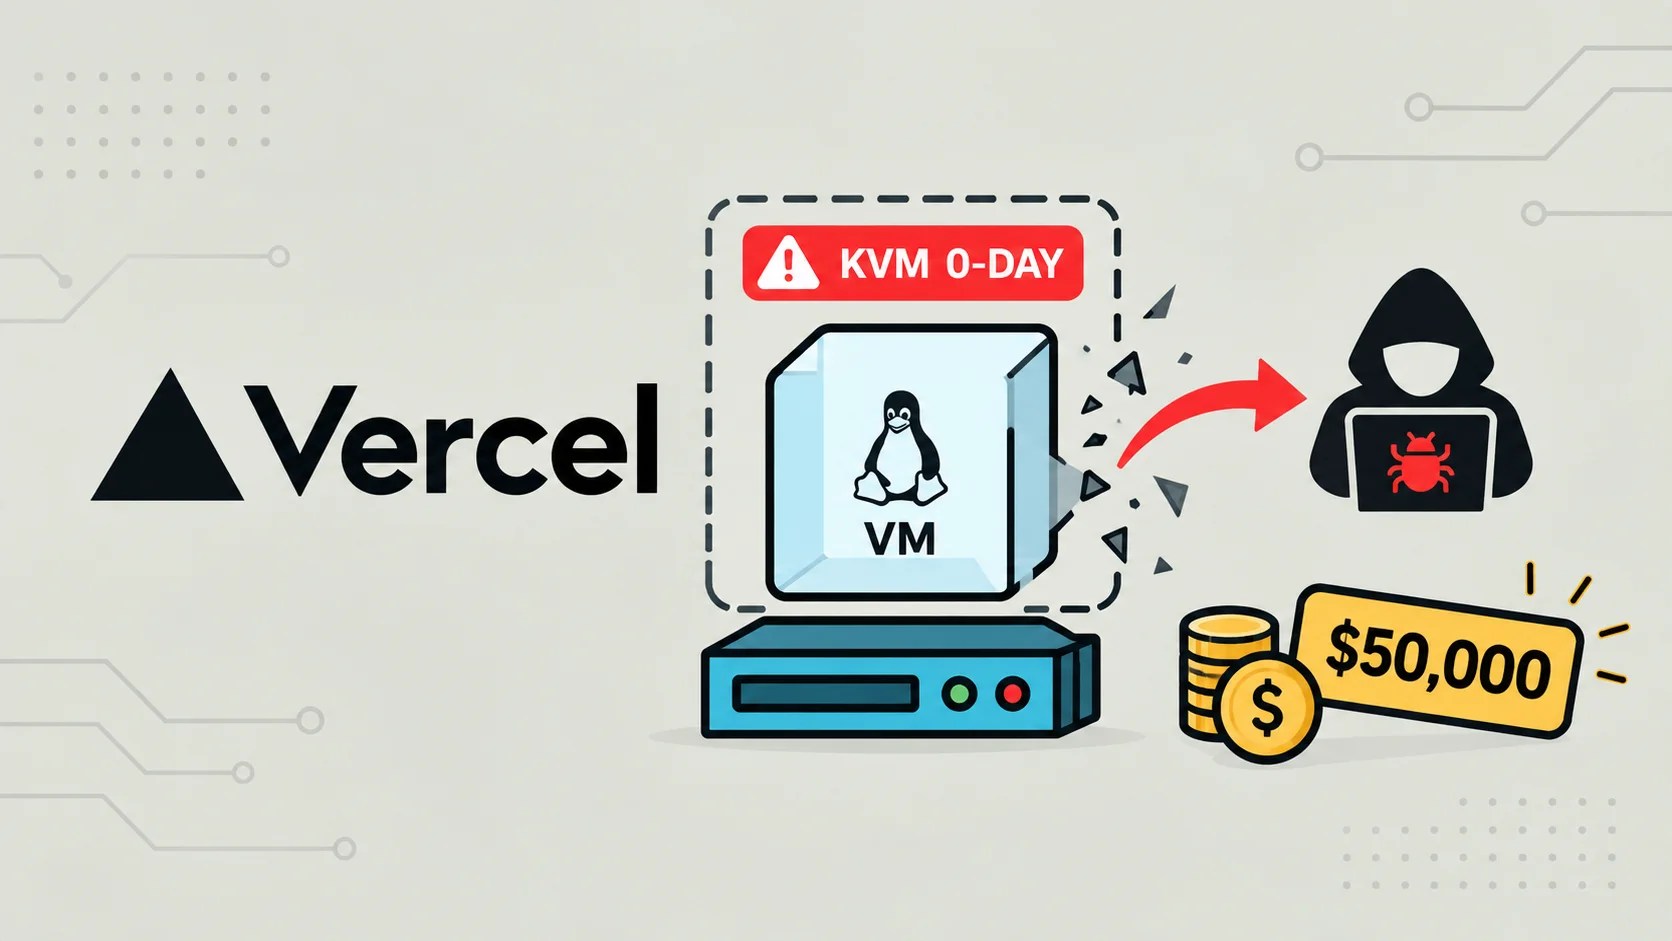
Vercel has confirmed a critical vulnerability in the KVM hypervisor, reported by security researcher Paulos Yibelo. This zero-day flaw allows potential code execution from a guest virtual machine, granting root access on the host system.

Significant Discovery Through Bug Bounty Program

The vulnerability was uncovered through Vercel’s Sandbox bug bounty initiative, highlighting security concerns in isolating untrusted workloads and AI-driven processes. Yibelo shared his findings on October 3, 2026, characterizing the issue as a complete virtual machine escape involving standard hypervisors.

Vercel’s CEO, Guillermo Rauch, confirmed the existence of a KVM zero-day without detailing the specific exploit mechanisms or affected software versions. A comprehensive technical report is anticipated to follow these announcements.

Rewarding Critical Vulnerability Reports

In recognition of the discovery, Vercel awarded Yibelo $50,000, the maximum payout for a single report in their program. This reward underscores the severity of vulnerabilities that could potentially expose or alter another customer’s data.

While the award signifies the critical nature of the flaw, there is no indication that customer data was compromised. The information released does not provide evidence of real-world exploitation or data theft.

Understanding the Implications for KVM

The KVM, or Kernel-based Virtual Machine, is a key component of Linux virtualization. It is crucial for maintaining separation between guest virtual machines and their hosts. A breach in this separation grants an attacker considerable control over the host system.

Vercel’s infrastructure employs Firecracker microVMs on Amazon’s EC2 hosts, with each sandbox isolated within these microVMs. The security breach described by Yibelo involves crossing from a container to the host system, a significant security boundary violation.

No Common Vulnerabilities and Exposures (CVE) identifier, affected software versions, or mitigation strategies have been disclosed yet. Until Vercel publishes a detailed technical analysis, operators should seek guidance from Vercel and relevant Linux providers.

Looking Ahead

The forthcoming technical write-up is expected to shed light on the root cause and offer guidance on protecting systems. The cybersecurity community is urged to await these details to gauge the vulnerability’s impact and necessary countermeasures.

For now, the confirmed vulnerability and potential host-root access remain primary concerns, with a focus on understanding and mitigating the risk rather than assuming widespread exploitation.
Cyber Security News Tags:AI agents, bug bounty, Cybersecurity, EC2, Firecracker, Hypervisor, KVM, Linux, microVM, root access, Sandbox, Vercel, virtual machine, Vulnerability, zero-day

Post navigation

Previous Post: ShinyHunters Suspect in Jordan Assists FBI in Hack Probe
Next Post: Key Arrest in ShinyHunters Case Aids FBI Investigation

Related Posts

GitHub AI Uncovers 24 Security Flaws in Android Apps GitHub AI Uncovers 24 Security Flaws in Android Apps Cyber Security News
ShinyHunters Claims Data Theft from 200+ Companies via Salesforce Gainsight Breach ShinyHunters Claims Data Theft from 200+ Companies via Salesforce Gainsight Breach Cyber Security News
New EDR-Redir Tool Breaks EDR Exploiting Bind Filter and Cloud Filter Driver New EDR-Redir Tool Breaks EDR Exploiting Bind Filter and Cloud Filter Driver Cyber Security News
Key Challenges Facing US SOCs: Solutions to Improve Efficiency Key Challenges Facing US SOCs: Solutions to Improve Efficiency Cyber Security News
HR Giant Workday Discloses Data Breach After Hackers Compromise Third-Party CRM HR Giant Workday Discloses Data Breach After Hackers Compromise Third-Party CRM Cyber Security News
NVIDIA VApp for Windows Vulnerability Let Attackers Execute Malicious Code NVIDIA VApp for Windows Vulnerability Let Attackers Execute Malicious Code Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Armornet Launches AI Security for Software Supply Chains
  • Critical NGINX HTTP/2 Vulnerability Allows Remote Code Execution
  • SpyCloud Predicts 2027 Cyber Threats: AI and Trusted Access Risks
  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Armornet Launches AI Security for Software Supply Chains
  • Critical NGINX HTTP/2 Vulnerability Allows Remote Code Execution
  • SpyCloud Predicts 2027 Cyber Threats: AI and Trusted Access Risks
  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark