Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Cisco Nexus Vulnerabilities Expose Networks to Critical Threats

Cisco Nexus Vulnerabilities Expose Networks to Critical Threats

Posted on October 8, 2026 By CWS

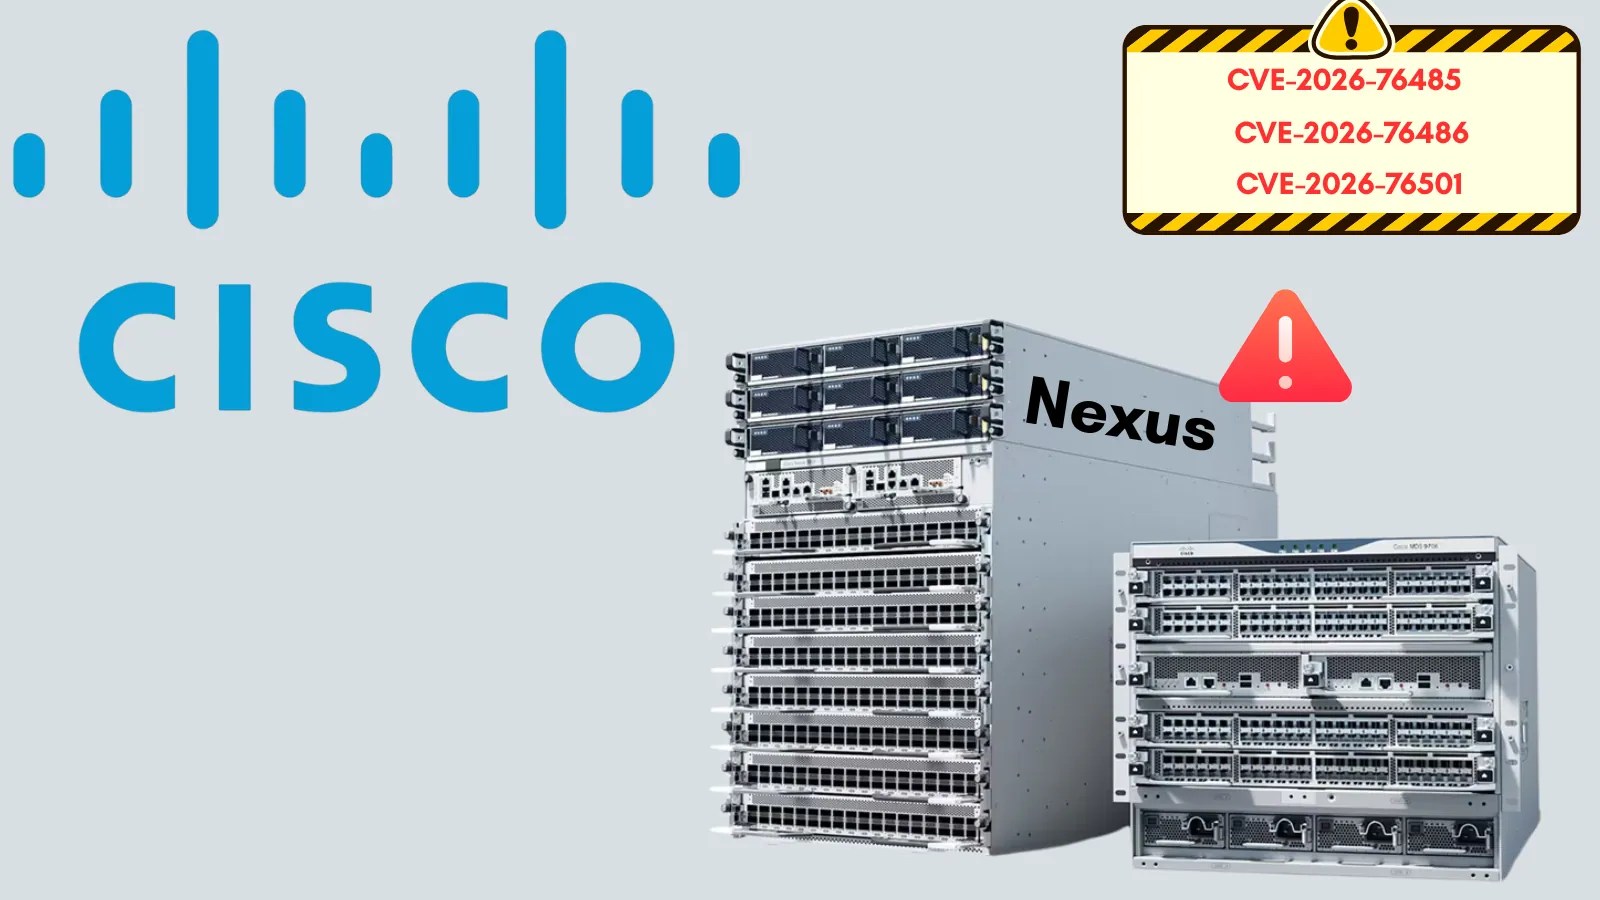
Cisco has issued important security updates addressing three severe vulnerabilities in its Nexus 3000 and 9000 Series switches. These flaws, if exploited, could allow unauthorized remote code execution with root-level access, posing a significant threat to network security.

Understanding the Vulnerabilities

The identified vulnerabilities reside in the Next Generation Operation, Administration, and Maintenance (NGOAM) feature of the Cisco NX-OS Software. Exploitation of these vulnerabilities may not only lead to unauthorized code execution but could also result in process crashes, switch reloads, and disruption of network services.

According to Cisco’s security advisory, released on October 7, 2026, the vulnerabilities are cataloged as CVE-2026-76485, CVE-2026-76486, and CVE-2026-76501, each carrying a critical CVSS base score of 9.8. The vulnerabilities were discovered during internal testing, with no known public exploitation at the time of disclosure.

Technical Details and Impact

The vulnerabilities arise from inadequate validation of incoming IP traffic when NGOAM is active. Crafted packets sent to an affected switch’s IP interface could exploit these flaws, allowing attackers to execute code with root privileges. This critical access level could give complete control over the operating system and possibly lead to denial-of-service attacks.

NGOAM is designed to assist with network troubleshooting, including VXLAN functions for loop detection and SRv6 functions for connectivity checks. However, the vulnerabilities’ impact varies, necessitating administrators to evaluate specific software versions and configurations.

Mitigation and Recommendations

Cisco’s advisory covers Nexus 3000 and 9000 Series switches operating in standalone NX-OS mode. Notably, CVE-2026-76485 requires only NGOAM to be enabled. In contrast, CVE-2026-76486 and CVE-2026-76501 also involve SRv6 and specific Network Virtualization Overlay configurations.

Administrators can verify NGOAM status with commands like show feature | include ngoam. Although no direct workarounds exist, disabling NGOAM through no feature ngoam can mitigate risks, as recommended by Cisco. Additionally, Cisco offers Live Protect shields as temporary protection measures, pending software patch updates.

Organizations are advised to use the Cisco Software Checker for identifying fixed software versions. Furthermore, a separate root-code-execution flaw, CVE-2026-20212, previously reported, highlights the necessity for ongoing vigilance and timely software updates.

Conclusion and Future Outlook

The disclosed vulnerabilities in Cisco Nexus switches underscore the importance of proactive network security management. By swiftly applying the recommended patches and configurations, organizations can safeguard against potential exploitation. As cybersecurity threats evolve, maintaining up-to-date systems remains critical in protecting network integrity.
Cyber Security News Tags:Cisco, CVSS score, Cybersecurity, network security, Nexus switches, NGOAM, remote code execution, security update, tech news, Vulnerabilities

Post navigation

Previous Post: TP-Link Faces Legal Actions Over Security Concerns
Next Post: Wazza Phishkit Poses Threat to Key Sectors Globally

Related Posts

How to Detect and Mitigate Insider Threats in Your Organization How to Detect and Mitigate Insider Threats in Your Organization Cyber Security News
Rundll32 and WebDAV: New ClickFix Variant Evades Detection Rundll32 and WebDAV: New ClickFix Variant Evades Detection Cyber Security News
APT28 Exploits MSHTML Zero-Day Vulnerability Before Patch APT28 Exploits MSHTML Zero-Day Vulnerability Before Patch Cyber Security News
Microsoft Warns of Remote Desktop Issues After Security Update Microsoft Warns of Remote Desktop Issues After Security Update Cyber Security News
Exploiting Unicode Flaws in macOS Security Tools Exploiting Unicode Flaws in macOS Security Tools Cyber Security News
Critical PowerSYSTEM Center Flaws Pose Security Risks Critical PowerSYSTEM Center Flaws Pose Security Risks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Newly Patched Ghostscript Flaw Highlights Security Risks
  • AI Hosting Firms Face Breaches: OpenRouter Drops Providers
  • OpenRouter Investigates AI Chat Privacy Breach
  • Microsoft Entra Connect Health Flaw Exposes Sensitive Data
  • Critical Ghostscript Flaw Threatens Servers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Newly Patched Ghostscript Flaw Highlights Security Risks
  • AI Hosting Firms Face Breaches: OpenRouter Drops Providers
  • OpenRouter Investigates AI Chat Privacy Breach
  • Microsoft Entra Connect Health Flaw Exposes Sensitive Data
  • Critical Ghostscript Flaw Threatens Servers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark