Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Break Into Google Pixel 10 at Pwn2Own Contest

Hackers Break Into Google Pixel 10 at Pwn2Own Contest

Posted on October 9, 2026 By CWS

At the recent Pwn2Own competition held in Cork, Ireland, three research teams successfully infiltrated fully patched Google Pixel 10 devices. The event, which took place on October 8, 2026, showcases hacking skills and awards researchers for their ability to identify vulnerabilities. Ikotas Labs stood out by winning the top prize of $300,000 and was named the overall winner of the contest.

Details of the Exploits

The Zero Day Initiative (ZDI), affiliated with Trend Micro, manages the Pwn2Own event. On October 9, they released the results, but specific details about the exploit mechanisms remain undisclosed. Notably, one of the winning exploits by the teams involved a previously known vulnerability, a situation referred to as a ‘collision’ by ZDI.

The rules of the contest stipulate that exploits should be based on bugs unknown to the vendor or the organizer. However, entries involving known bugs, albeit at a reduced prize, are still permissible. Participants demonstrated their skills by exploiting Pixel 10 devices through various remote methods, such as web content via the default browser or through wireless technologies including NFC, Wi-Fi, Bluetooth, or baseband.

Prize Distribution and Exploit Strategies

Xint, comprising Tim Becker and Yves Bieri, were the first to achieve a successful hack, earning $150,000 and 15 points. Their approach included a bug collision. Ikotas Labs followed, securing the full $300,000 and 30 points despite their entry being labeled a collision, with no further explanation provided.

The third team, consisting of Dimitrios Valsamaras, Ken Gannon, and Tenia Valsamara, utilized a combination of a collision and a zero-day vulnerability, earning them $112,500 and 22.5 points. Combined, these exploits awarded the participants a total of $562,500.

Future Implications and Vendor Response

The winning teams are required to hand over their exploit details to ZDI, who then communicates this information to the affected vendors. According to Trend Micro’s guidelines, vendors have a 90-day window to address these vulnerabilities before ZDI makes the technical details public.

Google’s security bulletin for October was released just days before the contest and did not mention these specific exploits. There is currently no guidance for Pixel users regarding these vulnerabilities. Other devices, such as Samsung’s Galaxy S26 and various smart home devices, were also targets at the event, with several successful hacks reported.

Overall, Pwn2Own 2026 awarded over $1.2 million, surpassing the previous year’s total. The event highlights the ongoing need for robust cybersecurity measures and the value of identifying vulnerabilities in modern technology.

The Hacker News Tags:Cybersecurity, Google Pixel 10, hacking contest, Ikotas Labs, mobile security, Pwn2Own, remote exploit, Trend Micro, Vulnerability, Zero Day Initiative

Post navigation

Previous Post: Critical Flaw in React Server Components Puts Next.js Servers at Risk
Next Post: AhsayCBS Flaws Actively Exploited, Urgent Action Needed

Related Posts

AI User Accounts Targeted by Infostealer Logs AI User Accounts Targeted by Infostealer Logs The Hacker News
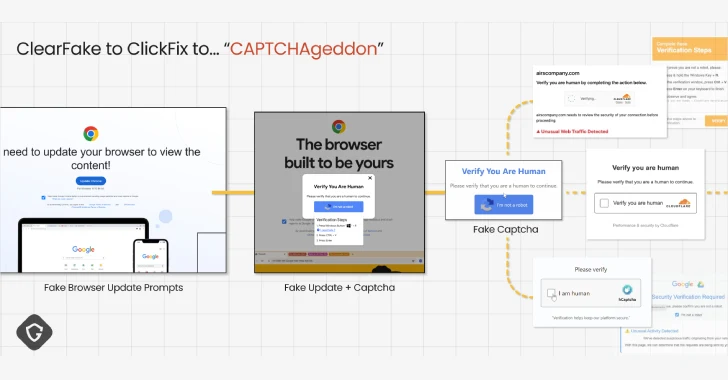
ClickFix Malware Campaign Exploits CAPTCHAs to Spread Cross-Platform Infections ClickFix Malware Campaign Exploits CAPTCHAs to Spread Cross-Platform Infections The Hacker News
Daxin Malware Reappears in Taiwan with New Stupig Backdoor Daxin Malware Reappears in Taiwan with New Stupig Backdoor The Hacker News
Google Ordered to Pay 4M for Misusing Android Users’ Cellular Data Without Permission Google Ordered to Pay $314M for Misusing Android Users’ Cellular Data Without Permission The Hacker News
NANOREMOTE Malware Uses Google Drive API for Hidden Control on Windows Systems NANOREMOTE Malware Uses Google Drive API for Hidden Control on Windows Systems The Hacker News
Open VSX Supply Chain Attack Used Compromised Dev Account to Spread GlassWorm Open VSX Supply Chain Attack Used Compromised Dev Account to Spread GlassWorm The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • New Exploit in Telegram Desktop Allows Account Takeover
  • AI Involvement in South Korean Bank Hacks Raises Concerns
  • AI Ambitions Clash with Outdated Security Measures
  • MATCHBOIL Deploys Backdoor via Hidden Servers
  • AhsayCBS Flaws Actively Exploited, Urgent Action Needed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • New Exploit in Telegram Desktop Allows Account Takeover
  • AI Involvement in South Korean Bank Hacks Raises Concerns
  • AI Ambitions Clash with Outdated Security Measures
  • MATCHBOIL Deploys Backdoor via Hidden Servers
  • AhsayCBS Flaws Actively Exploited, Urgent Action Needed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark