MATCHBOIL, a sophisticated malware downloader developed in C#, has been linked to the UAC-0099 group. It utilizes command-and-control (C2) servers obscured by Cloudflare services to introduce backdoor payloads into targeted systems. This evolution reflects a shift from a simple downloader to a more complex tool designed to evade detection through frequent server communications and advanced obfuscation techniques.
Targeted Attacks in Ukraine
Victims of MATCHBOIL have predominantly been identified within Ukraine, affecting sectors such as transportation, manufacturing, and energy. ESET documented these intrusions from July 2025 to June 2026. The research indicates a persistent threat across various industries, although the complete extent of the campaign remains undetermined. A detailed analysis by WeLiveSecurity, published on October 8, outlines the malware’s progression from April 2024 through April 2026.
MATCHBOIL was first publicly noted by CERT-UA in August 2025, but evidence suggests its development may have started earlier. ESET’s investigation aligns UAC-0099’s motives with Russian interests, albeit with medium confidence.
Phishing and Execution Tactics
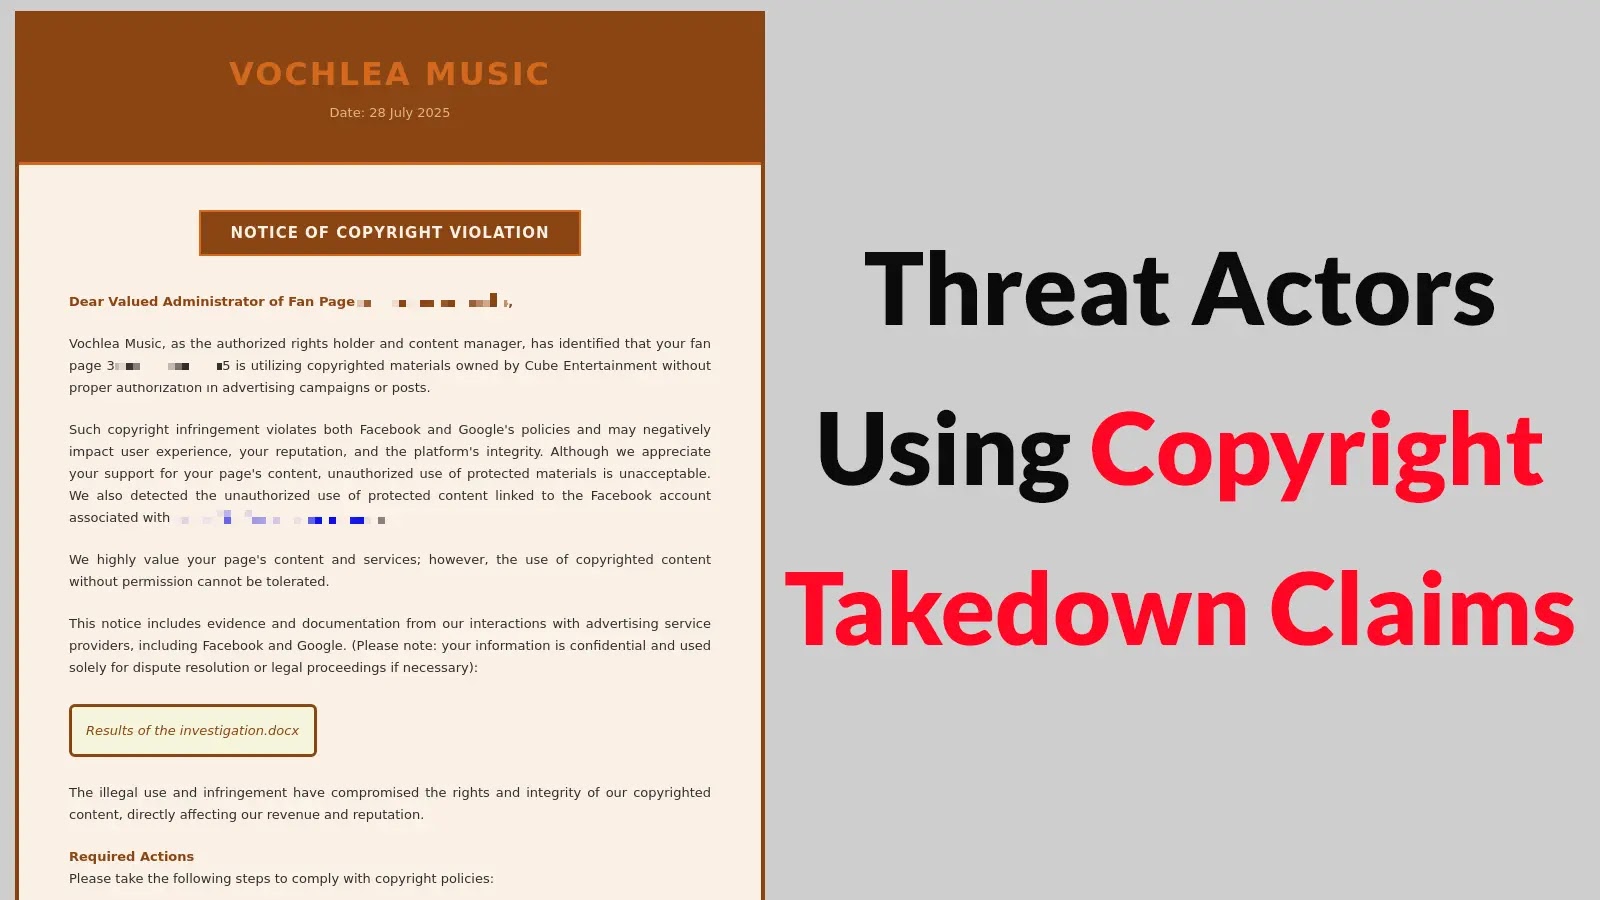
The infection process begins with targeted phishing emails containing links to a downloadable archive with a VBScript file. Users must manually execute this script, which then downloads and initiates MATCHBOIL. This method traces back to older techniques involving deceptive court notices, providing a historical context for UAC-0099’s document-based strategies.
Upon execution, MATCHBOIL checks for its existence to avoid redundant installations. It collects comprehensive system details including hardware identifiers and network information, aiding in unique victim identification during server interactions.
Concealment and Evasion Strategies
UAC-0099 employs virtual private servers and Cloudflare to conceal C2 server locations. ESET discovered the use of unique Let’s Encrypt certificates across domains, paralleling techniques seen in other cyber operations like MuddyWater. This concealment complicates detection by security practitioners.
Recent updates to MATCHBOIL have replaced simpler encryption with Eziriz .NET Reactor and introduced checks for analysis tools and system uptime. These improvements help avoid detection in research environments. Furthermore, the malware now initiates C2 communication every two minutes, allowing for continuous updates and retries in case of failures.
In April 2026, a variant labeled MATCHBOIL.V2 emerged, operating as a DLL via a custom loader. This version uses more inconspicuous file and task names to blend in with legitimate software, complicating its identification.
For security teams, it is crucial to focus on behavioral indicators such as unexpected VBScript activity and unusual HTTPS traffic from unfamiliar C# applications. These patterns, combined with known file paths and network indicators, provide a stronger investigative foundation than generic traffic analysis.