Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
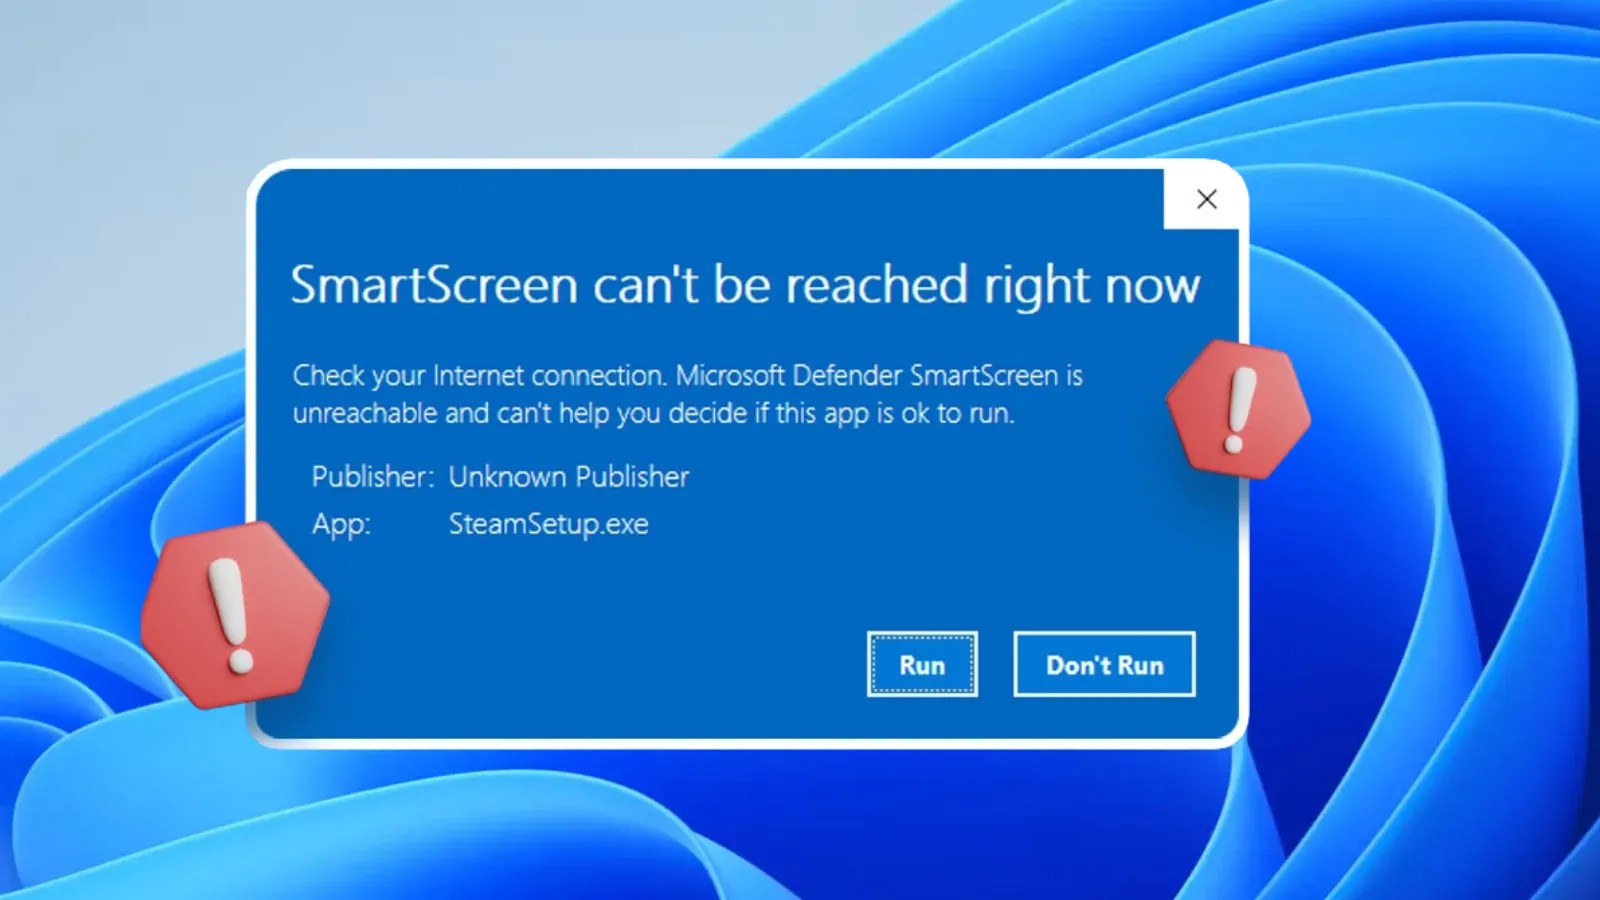
Critical Windows SmartScreen Vulnerability Patched by Microsoft

Critical Windows SmartScreen Vulnerability Patched by Microsoft

Posted on October 14, 2026 By CWS

Microsoft has recently addressed a significant security vulnerability in Windows SmartScreen, which could allow attackers with local access to escalate their privileges. Known as CVE-2026-85851, this flaw was made public on October 13, 2026, and is rated with a CVSS score of 7.8, reflecting its significance. The flaw impacts various versions of Windows 11 and Windows Server 2025, marking it as an important issue requiring immediate attention.

Understanding the Vulnerability

The identified flaw stems from a use-after-free memory error, categorized under CWE-416. This occurs when software attempts to use memory that has already been freed, potentially allowing malicious actors to exploit this by using the memory incorrectly. This can result in memory corruption, system crashes, or other severe security issues. The vulnerability allows an attacker to elevate their privileges from a low to a medium integrity level, although it does not directly grant admin or SYSTEM level access.

Exploitation of this flaw requires the attacker to already have low-level privileges on the compromised device. However, exploiting this vulnerability does not require any user interaction, making it a significant risk for systems where attackers have gained initial access.

Security Impact and Mitigation Efforts

The impact of this vulnerability is categorized as local privilege escalation. According to Microsoft’s CVSS vector, the attack complexity is low, and the required privileges are minimal, with no user interaction needed. Therefore, it is crucial for organizations to patch their systems promptly to mitigate potential risks associated with this flaw.

Researcher yhw is credited with discovering this vulnerability. While the flaw was not publicly disclosed or exploited at the time of the advisory, the potential for exploitation underlines the importance of updating affected systems without delay. Previous SmartScreen weaknesses involved different attack vectors, such as bypassing security warnings, which differ from this newly identified privilege escalation issue.

Additional Vulnerabilities and Patching Recommendations

Alongside CVE-2026-85851, Microsoft disclosed another SmartScreen vulnerability, CVE-2026-83504, related to information disclosure through a time-of-check-to-time-of-use race condition. This flaw has a CVSS score of 4.7 and requires overcoming a complex race condition, underscoring the need for precise timing in exploitation.

Microsoft has released updates for various affected systems, including Windows 11 versions 23H2, 24H2, 25H2, 26H1, 26H2, and Windows Server 2025. Administrators should ensure that each device is matched to its specific release and architecture and verify the installation of updates against Microsoft’s records. The update packages include KB5126653, KB5127648, KB5127646, and KB5126646, tailored for each corresponding version and architecture.

To safeguard against emerging threats, organizations should update their defenses promptly and consider integrating threat intelligence feeds to stay informed about potential vulnerabilities and exploits.
Cyber Security News Tags:CVE-2026-85851, CWE-416, Cybersecurity, local access, Microsoft, Patch, privilege escalation, Security, SmartScreen, Vulnerability, Windows

Post navigation

Previous Post: US Cracks Down on North Korean IT Worker Fraud Schemes
Next Post: CISA Urges Fast Update of Ivanti Connect Secure Amid Exploits

Related Posts

New Critical n8n Vulnerability Allow Attackers to Execute Arbitrary Commands New Critical n8n Vulnerability Allow Attackers to Execute Arbitrary Commands Cyber Security News
Hackers Using New ClickFix Technique To Exploits Human Error Via Fake Prompts Hackers Using New ClickFix Technique To Exploits Human Error Via Fake Prompts Cyber Security News
The Most Active RAT Uses New Stagers and Loaders to Bypass Defenses The Most Active RAT Uses New Stagers and Loaders to Bypass Defenses Cyber Security News
WhatsApp, Chrome 0-Day, AI Ransomware, and Cyber Attacks WhatsApp, Chrome 0-Day, AI Ransomware, and Cyber Attacks Cyber Security News
CISA Warns of WHILL Model C2 Wheelchairs Vulnerability Let Attackers Take Control of Product CISA Warns of WHILL Model C2 Wheelchairs Vulnerability Let Attackers Take Control of Product Cyber Security News
UNC6692 Exploits Microsoft Teams for SNOW Malware Attack UNC6692 Exploits Microsoft Teams for SNOW Malware Attack Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Curl 8.23.0 Fixes 24 Vulnerabilities Impacting Billions
  • Join the Zero Trust Strategies Virtual Summit Today
  • AI Discovers Critical OTP Bypass in Major Insurer’s Site
  • Tech Giants Unite to Tackle West African Scam Networks
  • AI Mastery of OT Systems Raises Security Concerns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Curl 8.23.0 Fixes 24 Vulnerabilities Impacting Billions
  • Join the Zero Trust Strategies Virtual Summit Today
  • AI Discovers Critical OTP Bypass in Major Insurer’s Site
  • Tech Giants Unite to Tackle West African Scam Networks
  • AI Mastery of OT Systems Raises Security Concerns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark