Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
New Windows 11 Flaw Lets Attackers Bypass Lock Screen

New Windows 11 Flaw Lets Attackers Bypass Lock Screen

Posted on November 20, 2026 By CWS

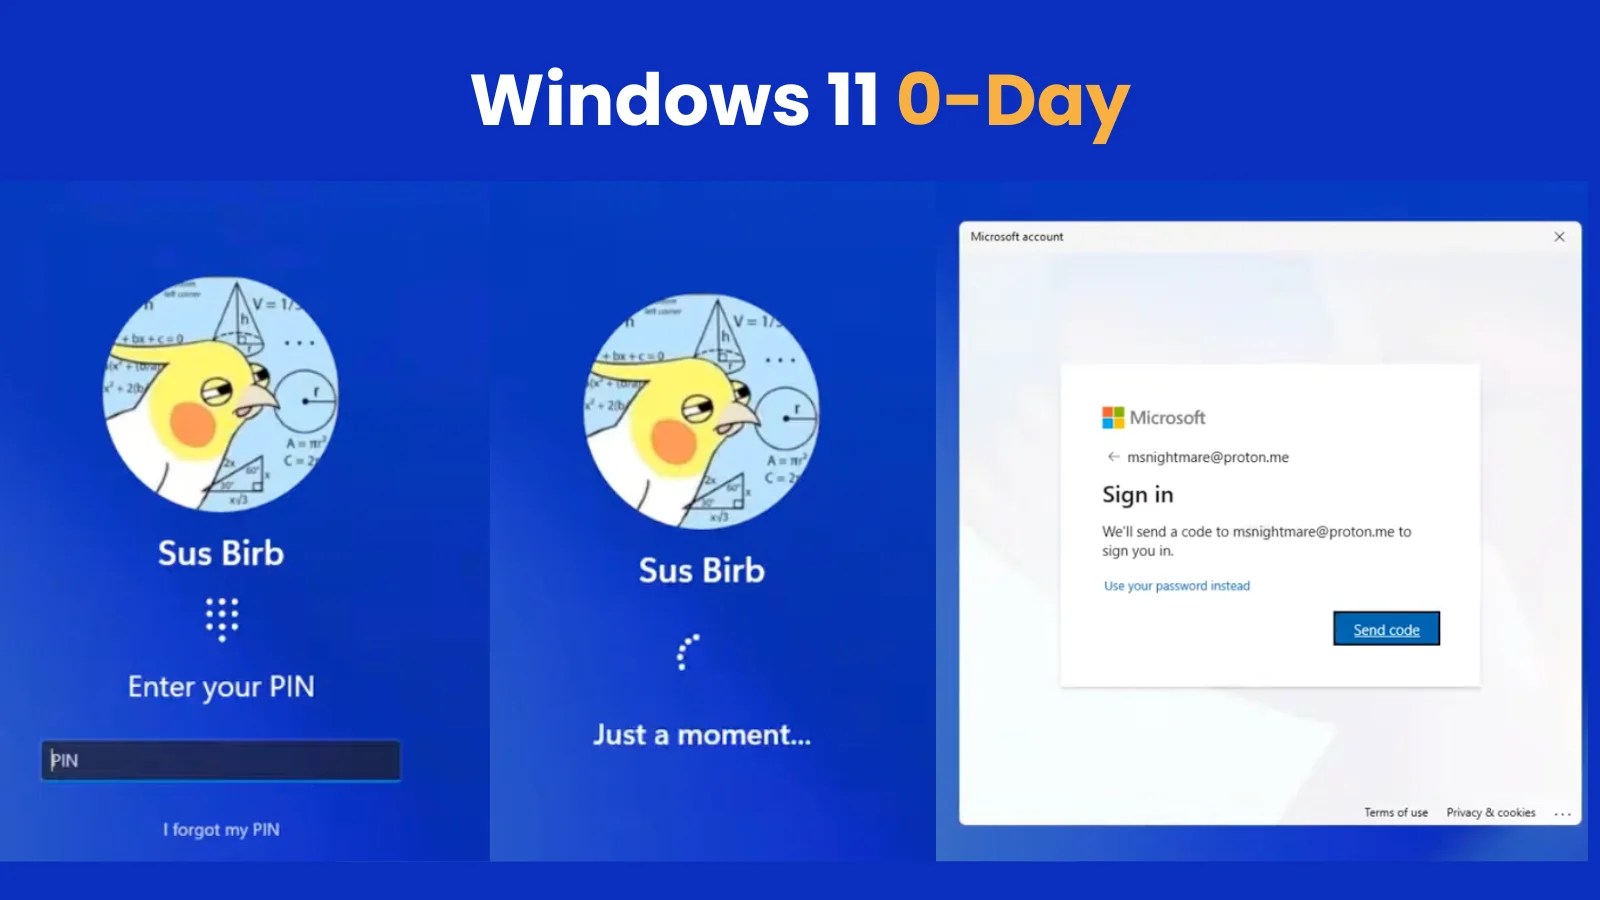
A critical vulnerability in Windows 11, known as FastUnlock, has been uncovered, allowing individuals with physical access to bypass the lock screen and execute code without logging in. This flaw impacts the Narrator feature, a built-in screen reader, posing a risk to systems even when BitLocker encryption is active.

Understanding the FastUnlock Vulnerability

FastUnlock, discovered by a researcher using the alias Nightmare Eclipse, was tested on Windows 11 version 26H2 with security updates as recent as November 2026. The researcher highlighted that the flaw could be exploited in about five minutes under specific conditions, although this was not an average time across various Windows devices.

The vulnerability necessitates physical access to the device and at least one online Microsoft account. It manipulates the account recovery screen, allowing Narrator to interact with unauthorized interfaces. The issue arises not from the availability of a screen reader at the lock screen but from its ability to access controls beyond it.

Implications for System Security

The security community has previously dealt with similar issues, such as CVE-2026-97015 and CVE-2026-119832, which were addressed in previous updates. However, the FastUnlock flaw remains unresolved as of November 20, with no official Microsoft advisory or fix released.

Tests conducted by ThreatLocker revealed that FastUnlock allows code execution under the WsiAccount, a non-administrative account used at the lock screen. This does not permit full control over the device or access to all files, highlighting the vulnerability’s limitations.

Protective Measures and Future Outlook

BitLocker provides protection while data is at rest, but once the system is active, access is governed by lock screen and account permissions. FastUnlock targets this active state, differing from previous vulnerabilities like YellowKey, which attacked BitLocker before Windows fully loaded.

Microsoft advises pairing devices with a trusted platform module (TPM) and a startup PIN for enhanced security against physical access. This does not mitigate the Narrator flaw but helps protect devices that are shut down or hibernated. For portable devices, ensuring they are shut down or properly hibernated is recommended, as sleep mode does not require a startup PIN.

While no attacks using FastUnlock have been publicly reported, organizations should remain vigilant and restrict physical access to vulnerable devices. Security teams should stay updated on potential advisories from Microsoft concerning this issue.

Cyber Security News Tags:0-day vulnerability, BitLocker, Cybersecurity, FastUnlock, lock screen, Microsoft, Narrator, physical access, security flaw, Windows 11

Post navigation

Previous Post: 8.8 Million NGINX Services at Risk from NGINX2Root Flaws
Next Post: New Windows Vulnerability Allows Limited Program Access

Related Posts

China-Linked Silver Dragon Uses Google Drive in Cyberattacks China-Linked Silver Dragon Uses Google Drive in Cyberattacks Cyber Security News
How SOCs Detect More Threats without Alert Overload How SOCs Detect More Threats without Alert Overload Cyber Security News
Beware of Malicious ChatGPT Apps That Records Users Action and Steals Sensitive Data Beware of Malicious ChatGPT Apps That Records Users Action and Steals Sensitive Data Cyber Security News
M Cryptocurrency Theft Linked to LastPass Password Manager DataBreach $35M Cryptocurrency Theft Linked to LastPass Password Manager DataBreach Cyber Security News
Python-powered Toolkit for Information Gathering and reconnaissance Python-powered Toolkit for Information Gathering and reconnaissance Cyber Security News
pgAdmin 4 Update: Security Enhancements and New Features pgAdmin 4 Update: Security Enhancements and New Features Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Java Vulnerability Affects Palo Alto Products: Key Details
  • Debian Packages Retain Distrusted Certificates Despite Updates
  • WhatsApp Fixes Android Security Flaw Amid Scam Concerns
  • Microsoft Probes Attachment Upload Issues in New Outlook
  • Critical OpenSSL Vulnerability Discovered in Base64 Encoding

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Java Vulnerability Affects Palo Alto Products: Key Details
  • Debian Packages Retain Distrusted Certificates Despite Updates
  • WhatsApp Fixes Android Security Flaw Amid Scam Concerns
  • Microsoft Probes Attachment Upload Issues in New Outlook
  • Critical OpenSSL Vulnerability Discovered in Base64 Encoding

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark