Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Pre-Auth Exploit Chains Found in Commvault Could Enable Remote Code Execution Attacks

Pre-Auth Exploit Chains Found in Commvault Could Enable Remote Code Execution Attacks

Posted on August 21, 2025August 21, 2025 By CWS

Aug 21, 2025Ravie LakshmananVulnerability / Software program Safety
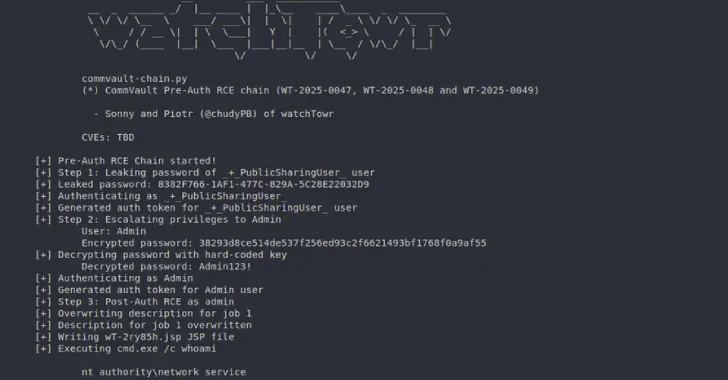
Commvault has launched updates to handle 4 safety gaps that may very well be exploited to attain distant code execution on inclined cases.
The listing of vulnerabilities, recognized in Commvault variations earlier than 11.36.60, is as follows –

CVE-2025-57788 (CVSS rating: 6.9) – A vulnerability in a recognized login mechanism permits unauthenticated attackers to execute API calls with out requiring consumer credentials
CVE-2025-57789 (CVSS rating: 5.3) – A vulnerability through the setup part between set up and the primary administrator login that enables distant attackers to use the default credentials to achieve admin management
CVE-2025-57790 (CVSS rating: 8.7) – A path traversal vulnerability that enables distant attackers to carry out unauthorized file system entry via a path traversal challenge, leading to distant code execution
CVE-2025-57791 (CVSS rating: 6.9) – A vulnerability that enables distant attackers to inject or manipulate command-line arguments handed to inner parts as a result of inadequate enter validation, leading to a sound consumer session for a low-privilege position

watchTowr Labs researchers Sonny Macdonald and Piotr Bazydlo have been credited with discovering and reporting the 4 safety defects in April 2025. All of the flagged vulnerabilities have been resolved in variations 11.32.102 and 11.36.60. Commvault SaaS resolution just isn’t affected.
In an evaluation revealed Wednesday, the cybersecurity firm mentioned risk actors may trend these vulnerabilities into two pre-authenticated exploit chains to attain code execution on inclined cases: One that mixes CVE-2025-57791 and CVE-2025-57790, and the opposite that strings CVE-2025-57788, CVE-2025-57789, and CVE-2025-57790.
It is price noting that the second pre-auth distant code execution chain turns into profitable provided that the built-in admin password hasn’t been modified since set up.
The disclosure comes practically 4 months after watchTowr Labs reported a essential Commvault Command Middle flaw (CVE-2025-34028, CVSS rating: 10.0) that would enable arbitrary code execution on affected installations.
A month later, the U.S. Cybersecurity and Infrastructure Safety Company (CISA) added the vulnerability to its Identified Exploited Vulnerabilities (KEV) catalog, citing proof of lively exploitation within the wild.
The Hacker News Tags:Attacks, Chains, Code, Commvault, Enable, Execution, Exploit, PreAuth, Remote

Post navigation

Previous Post: Cybercriminals Deploy CORNFLAKE.V3 Backdoor via ClickFix Tactic and Fake CAPTCHA Pages
Next Post: How to Stay Safe from Fake Job Offers

Related Posts

Two Critical Flaws Uncovered in Wondershare RepairIt Exposing User Data and AI Models Two Critical Flaws Uncovered in Wondershare RepairIt Exposing User Data and AI Models The Hacker News
Hidden Setting in Muse AI Poses Security Threat Hidden Setting in Muse AI Poses Security Threat The Hacker News
Phishing Risks and Cyber Threats: Top Stories of the Week Phishing Risks and Cyber Threats: Top Stories of the Week The Hacker News
Gainsight Expands Impacted Customer List Following Salesforce Security Alert Gainsight Expands Impacted Customer List Following Salesforce Security Alert The Hacker News
CL-STA-0969 Installs Covert Malware in Telecom Networks During 10-Month Espionage Campaign CL-STA-0969 Installs Covert Malware in Telecom Networks During 10-Month Espionage Campaign The Hacker News
Fake AI Tools Used to Spread Noodlophile Malware, Targeting 62,000+ via Facebook Lures Fake AI Tools Used to Spread Noodlophile Malware, Targeting 62,000+ via Facebook Lures The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark