Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
DDoS Mitigation Provider targeted In 1.5 Gpps 1.5 Billion Packets per Second DDoS Attack

DDoS Mitigation Provider targeted In 1.5 Gpps 1.5 Billion Packets per Second DDoS Attack

Posted on September 11, 2025September 11, 2025 By CWS

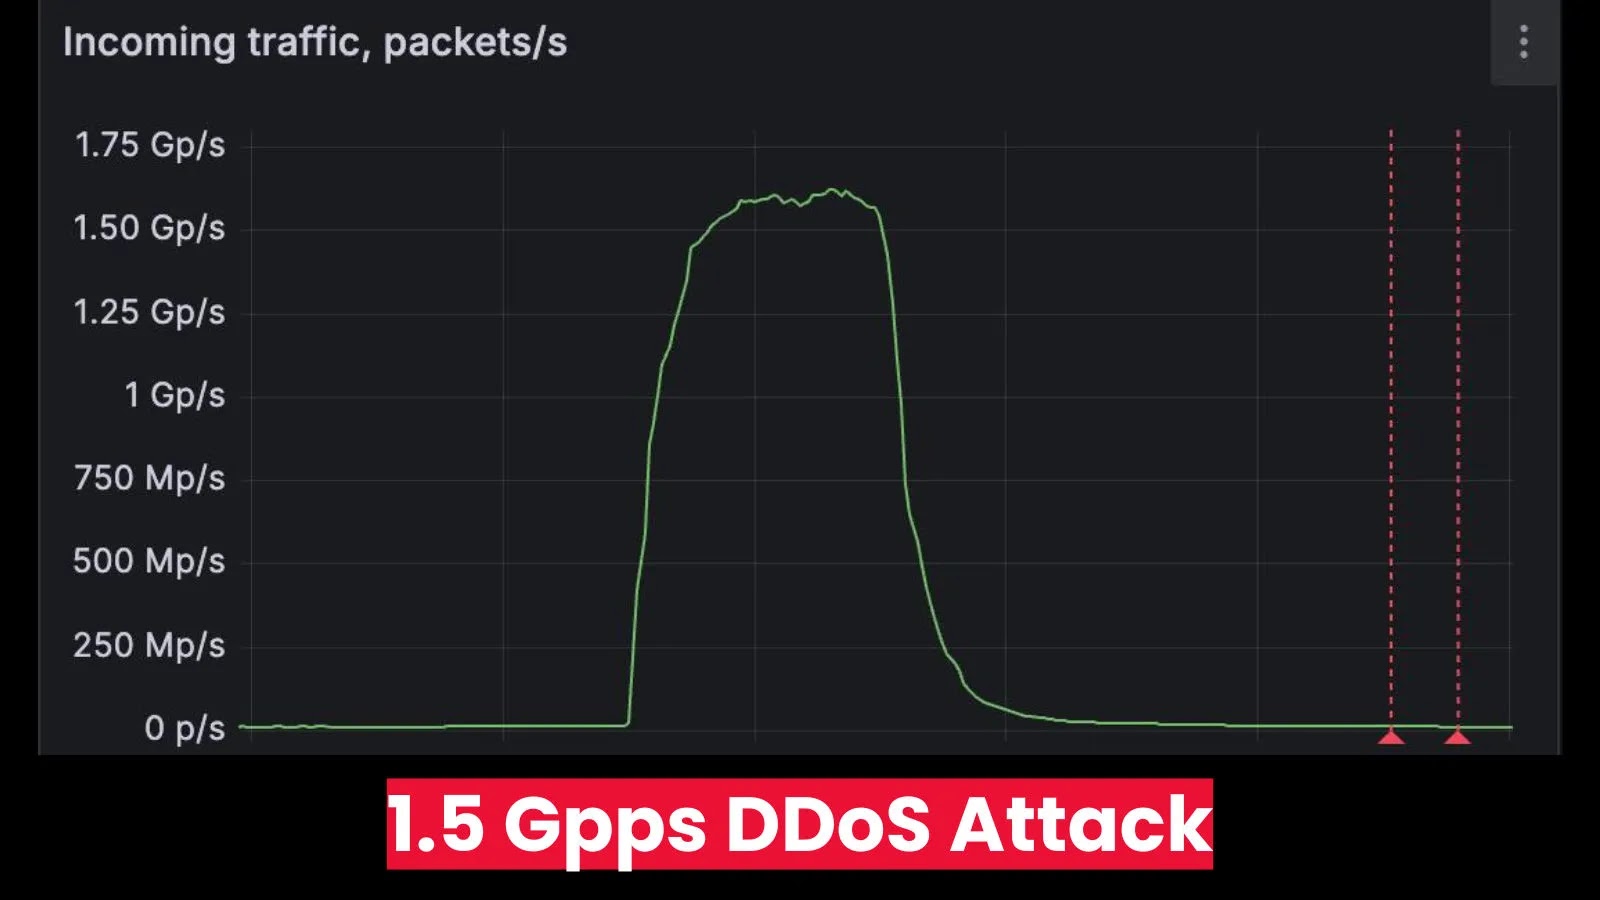
FastNetMon, a distinguished supplier of DDoS detection options, introduced this week that it had recognized and helped mitigate a record-breaking distributed denial-of-service (DDoS) assault.

The assault focused a serious DDoS scrubbing vendor situated in Western Europe, pushing packet-forwarding charges to an astonishing 1.5 billion packets per second (1.5 Gpps).

This incident stands as one of the vital intense packet-rate floods ever publicly disclosed. The assault was primarily a UDP flood, a normal methodology utilized by menace actors to overwhelm a goal’s sources.

The malicious site visitors originated from an unlimited and globally distributed botnet of compromised customer-premises gear (CPE).

DDoS Assault

This community of hijacked gadgets included on a regular basis electronics similar to IoT devices and routers, unfold throughout greater than 11,000 distinctive networks world wide.

By harnessing a lot of gadgets, the attackers had been in a position to generate a crippling quantity of site visitors directed at a single goal, sarcastically, an organization that makes a speciality of defending in opposition to such occasions.

This huge packet flood comes simply days after Cloudflare reported mitigating a separate, colossal 11.5 Tbps DDoS assault, signaling a transparent and worrying escalation within the capabilities of cybercriminals.

Whereas that assault targeted on bandwidth quantity (bits per second), the FastNetMon incident highlights a special however equally harmful vector: packet quantity (packets per second).

Excessive packet-per-second charges are designed to exhaust the {hardware} and software program sources of community gear like routers and firewalls, which might solely course of a finite variety of packets at any given time, no matter their bandwidth.

“This occasion is a part of a harmful pattern,” said Pavel Odintsov, Founding father of FastNetMon. He warned of the rising menace panorama the place tens of 1000’s of insecure shopper gadgets may be weaponized into highly effective, coordinated assault instruments.

The system, which employs extremely optimized C++ algorithms for real-time community site visitors evaluation, routinely recognized the anomalous flood inside seconds of its launch.

This speedy alert enabled the seller to activate its mitigation protocols, efficiently stopping any important disruption to its companies and defending its infrastructure from being overwhelmed.

The incident highlights the essential significance of high-speed, automated detection in an period of more and more subtle DDoS threats.

Discover this Story Fascinating! Comply with us on Google Information, LinkedIn, and X to Get Extra Instantaneous Updates.

Cyber Security News Tags:Attack, Billion, DDoS, Gpps, Mitigation, Packets, Provider, Targeted

Post navigation

Previous Post: ACSC Warns Of Sonicwall Access Control Vulnerability Actively Exploited In Attacks
Next Post: 1.5 Billion Packets Per Second DDoS Attack Detected with FastNetMon

Related Posts

Critical NGINX Security Flaws Patched by F5 Critical NGINX Security Flaws Patched by F5 Cyber Security News
Cursor AI Vulnerability Risks Developer Credentials Cursor AI Vulnerability Risks Developer Credentials Cyber Security News
TA829 Hackers Employs New TTPs and Upgraded RomCom Backdoor to Evade Detections TA829 Hackers Employs New TTPs and Upgraded RomCom Backdoor to Evade Detections Cyber Security News
CrowdStrike Fires Insider for Sharing Internal System Details with Hackers CrowdStrike Fires Insider for Sharing Internal System Details with Hackers Cyber Security News
FortiBleed 2.0 Uncovers Thousands of Exposed Fortinet Credentials FortiBleed 2.0 Uncovers Thousands of Exposed Fortinet Credentials Cyber Security News
Critical Apache Tika Core Vulnerability Exploited by Uploading Malicious PDF Critical Apache Tika Core Vulnerability Exploited by Uploading Malicious PDF Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark