Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Researcher Reveals Potential AI Model Jailbreak Technique

Researcher Reveals Potential AI Model Jailbreak Technique

Posted on July 25, 2026 By CWS

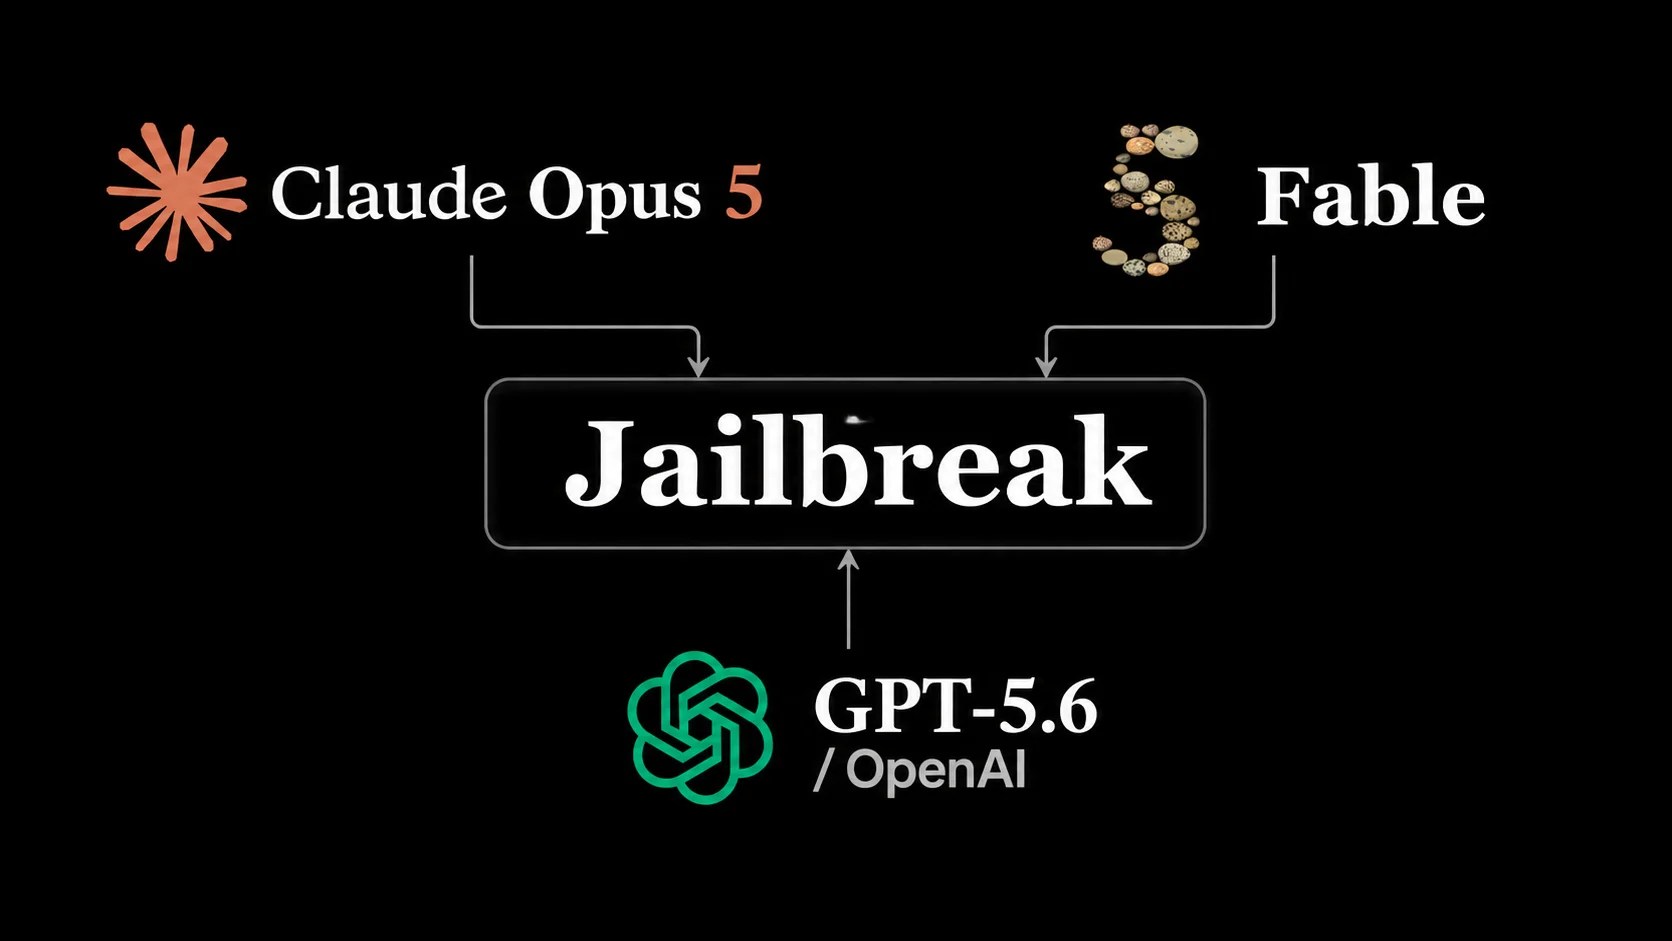
An acclaimed AI security researcher has announced the development of a universal jailbreak technique that could potentially compromise leading artificial intelligence models, including GPT-5.6 Sol, Claude Opus 5, and Fable. This revelation has sparked significant interest and concern within the AI community.

Universal Jailbreak Technique Unveiled

Pliny the Liberator, a prominent figure in AI red teaming, disclosed this breakthrough in a public statement on the social media platform X. According to Pliny, the method is effective across all tested AI models and categories. He emphasized that the inherent nature of the technique might render it exceptionally challenging to fully address or mitigate.

Unlike many previous disclosures that are immediately shared with the open-source community, Pliny has chosen to temporarily withhold the complete details of his technique. He aims to provide a responsible disclosure period, allowing AI laboratories, security researchers, and policymakers to evaluate and address the potential implications comprehensively.

Implications for AI Security

The concept of a universal jailbreak is particularly noteworthy, as most existing bypasses are typically model-specific and are often patched following disclosure. If Pliny’s claims withstand independent validation, it could highlight persistent vulnerabilities in safety training, the strength of model guardrails, and the generalization of attack strategies across different AI systems.

Pliny does not believe that publicizing the technique would inherently increase global risk. However, he acknowledges the potential for differing opinions and is focused on assessing the full impact of the method, understanding the additional capabilities it may unlock, and providing a data-driven framework for decision-makers.

Industry Response and Next Steps

The AI industry is urged to view this announcement as a preliminary alert rather than confirmed evidence of a widespread vulnerability. For the time being, organizations using these models should maintain standard security protocols, such as monitoring outputs, restricting tool access, conducting human reviews of high-risk tasks, and having clear procedures for policy breaches.

Pliny intends to release the full details of the jailbreak technique when deemed appropriate. Until then, the response from AI labs and the broader industry—whether through private testing or public engagement—will be crucial in determining the trajectory of this development.

As the AI sector awaits further information, the focus remains on ensuring robust security practices and fostering collaboration among stakeholders to address potential vulnerabilities effectively.

Cyber Security News Tags:AI models, AI policy, AI safety, AI security, AI vulnerabilities, Claude Opus 5, Cybersecurity, GPT-5.6, Jailbreak, Pliny the Liberator, security research

Post navigation

Previous Post: DevMan RaaS Centralizes Cyber Operations and Affiliations
Next Post: SourTrade Campaign Uses Malvertising for Malware Assembly

Related Posts

New PamStealer Malware Targets Mac Passwords New PamStealer Malware Targets Mac Passwords Cyber Security News
Go Module Attack: Password Theft and Backdoor Insertion Threat Go Module Attack: Password Theft and Backdoor Insertion Threat Cyber Security News
Hackers Exploit Microsoft Teams, Posing as IT Help Desk for Screen Sharing and Remote Access Hackers Exploit Microsoft Teams, Posing as IT Help Desk for Screen Sharing and Remote Access Cyber Security News
Kenyan Filmmakers Installed With FlexiSPY Spyware That Monitors Messages and Social Media Kenyan Filmmakers Installed With FlexiSPY Spyware That Monitors Messages and Social Media Cyber Security News
Threat Actors Allegedly Selling Monolock Ransomware on Dark Web Forums Threat Actors Allegedly Selling Monolock Ransomware on Dark Web Forums Cyber Security News
Windows Shortcuts Exploit PowerShell for Remote Attacks Windows Shortcuts Exploit PowerShell for Remote Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH
  • Anthropic’s Record-Breaking IPO Amid AI Safety Concerns
  • Microsoft Teams Scams: A New Cybersecurity Threat
  • AI Coding Agents at Risk from Malicious Downloads
  • Hackers Target 953 Magento Stores with Stealthy JavaScript

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH
  • Anthropic’s Record-Breaking IPO Amid AI Safety Concerns
  • Microsoft Teams Scams: A New Cybersecurity Threat
  • AI Coding Agents at Risk from Malicious Downloads
  • Hackers Target 953 Magento Stores with Stealthy JavaScript

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark