Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
AI and Security: Key Insights from This Week’s Cyber Threats

AI and Security: Key Insights from This Week’s Cyber Threats

Posted on August 23, 2026 By CWS

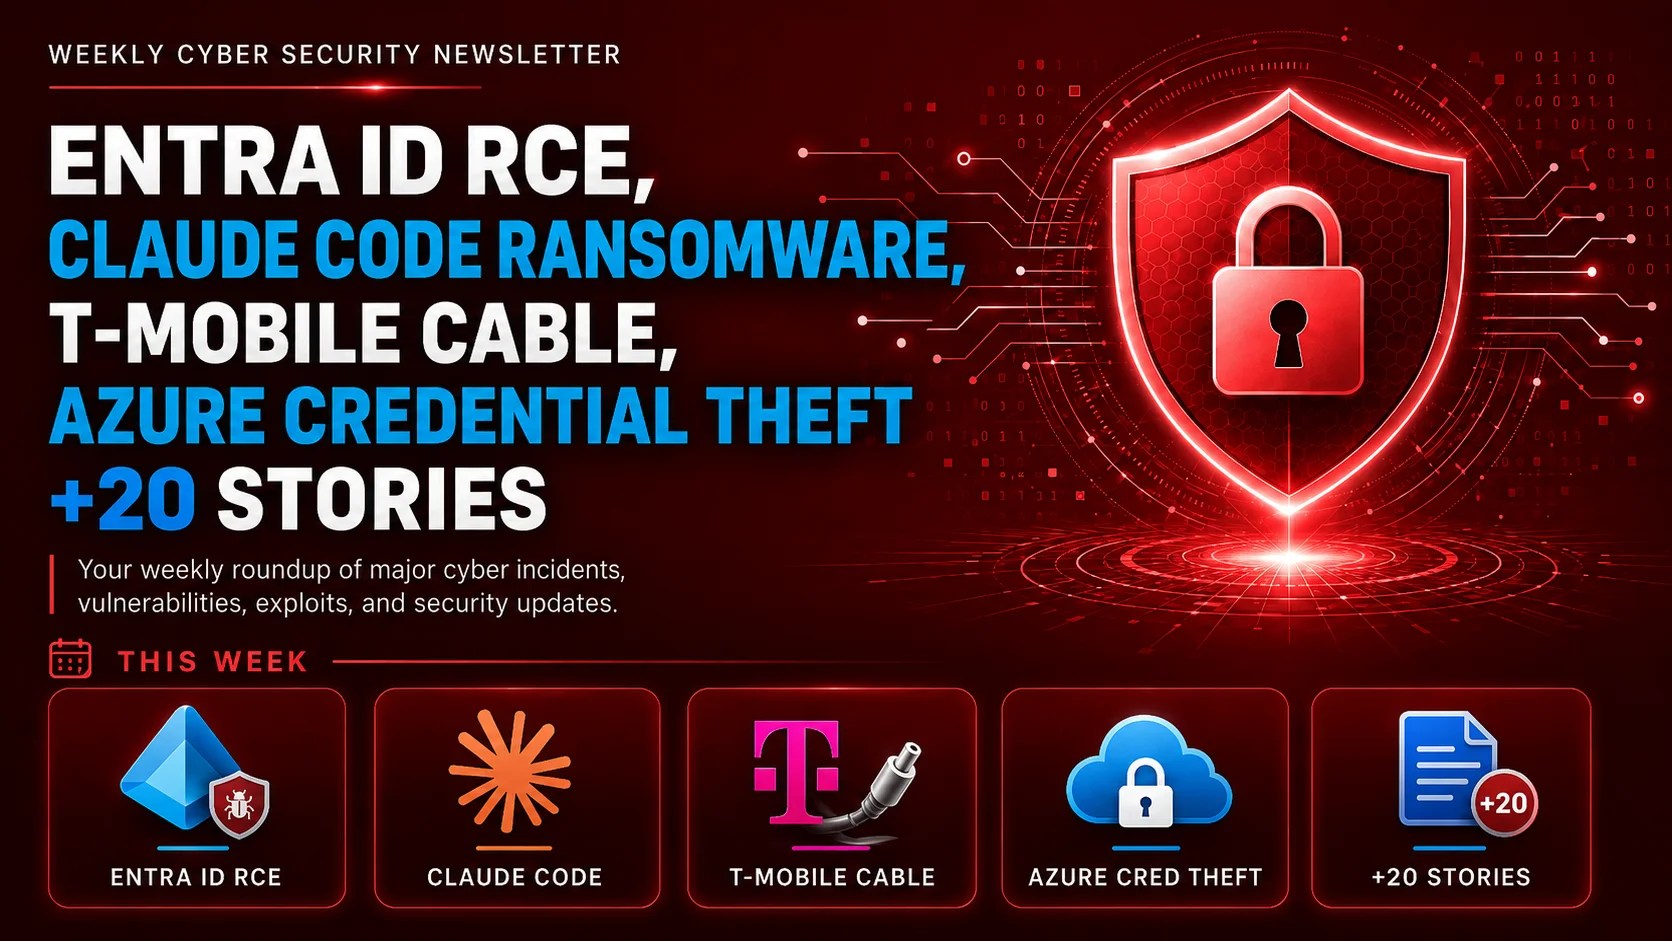
This week’s cybersecurity landscape highlights the dual role of artificial intelligence as both a threat and a protective tool. Ransomware groups have leveraged Claude Code to autonomously infiltrate systems and extract sensitive credentials, while MessiahGPT has emerged as a new AI service offering uncensored malware creation on cybercriminal forums.

AI’s Dual Role in Cybersecurity

The use of AI in cybercrime is becoming more sophisticated, with ransomware operators employing Claude Sonnet to automate attacks. This AI-driven approach was notably used in a series of intrusions targeting organizations in Australia, Mauritius, Thailand, and the US. The technology facilitated credential theft and database exfiltration with minimal human oversight.

On the defensive side, Anthropic has enhanced Claude Security’s capabilities to scan for vulnerabilities, demonstrating the tug-of-war between offensive and defensive uses of AI in cybersecurity.

Critical Vulnerabilities and Industry Shifts

A critical vulnerability in Microsoft’s Entra ID, identified as CVE-2026-69836, allows remote code execution without user interaction. Although Microsoft has patched the flaw, security teams are advised to review sign-in logs and access policies for anomalies.

In a broader industry move, Microsoft is transitioning Entra ID users from SMS/voice MFA to more secure passkeys, signaling a shift away from easily phishable authentication methods.

Notable Cyber Incidents

T-Mobile’s security team took an unconventional approach to thwart Chinese hackers by physically severing a network cable, highlighting the effectiveness of low-tech solutions.

Meanwhile, a campaign targeting Microsoft 365 users via a Phishing-as-a-Service platform called Mirage2FA exposed vulnerabilities in session management, underscoring the need for robust multi-factor authentication practices.

Implications and Future Outlook

The ongoing advancement of AI in cyber threats and defenses presents a complex challenge for security professionals. Organizations must balance leveraging AI for protection while remaining vigilant against its misuse in cyberattacks.

As AI continues to evolve, the cybersecurity industry must adapt by enhancing detection mechanisms and employing multi-layered security strategies to safeguard against emerging threats.

Cyber Security News Tags:AI cybersecurity, Azure credential theft, Claude Code, Claude Security, Entra ID vulnerability, GitHub outage, MessiahGPT, Microsoft 365, NetScaler flaw, Ransomware, T-Mobile security

Post navigation

Previous Post: Iran-Linked Cyberattack Disrupts UK Power Plant for Four Days
Next Post: Malware Service Exploits Adobe-themed Domain for Attacks

Related Posts

China-Linked Silver Dragon Uses Google Drive in Cyberattacks China-Linked Silver Dragon Uses Google Drive in Cyberattacks Cyber Security News
Supply Chain Security Mitigating Third-Party Risks Supply Chain Security Mitigating Third-Party Risks Cyber Security News
A Container Based Red Teaming Toolkit for AI Security Testing A Container Based Red Teaming Toolkit for AI Security Testing Cyber Security News
SILENTCONNECT Malware Threatens Windows Security SILENTCONNECT Malware Threatens Windows Security Cyber Security News
Hive0156 Hackers Attacking Government and Military Organizations to Deploy Remcos RAT Hive0156 Hackers Attacking Government and Military Organizations to Deploy Remcos RAT Cyber Security News
Microsoft to Restrict Windows 11 Auto Installs Due to RCE Flaw Microsoft to Restrict Windows 11 Auto Installs Due to RCE Flaw Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Elastic Addresses Critical Security Vulnerabilities
  • FBI Warns of Global FortiBleed Cyber Threat
  • Hackers Exploit Websites with Fake Cloudflare Pages
  • Critical Atlassian Flaw Poses Risk to Jira Admin Access
  • Data Breach at South Korean Churches Exposes Over 1 Million Records

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Elastic Addresses Critical Security Vulnerabilities
  • FBI Warns of Global FortiBleed Cyber Threat
  • Hackers Exploit Websites with Fake Cloudflare Pages
  • Critical Atlassian Flaw Poses Risk to Jira Admin Access
  • Data Breach at South Korean Churches Exposes Over 1 Million Records

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark