Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Security Flaws in Connective eID Extension Resolved

Critical Security Flaws in Connective eID Extension Resolved

Posted on August 10, 2026 By CWS

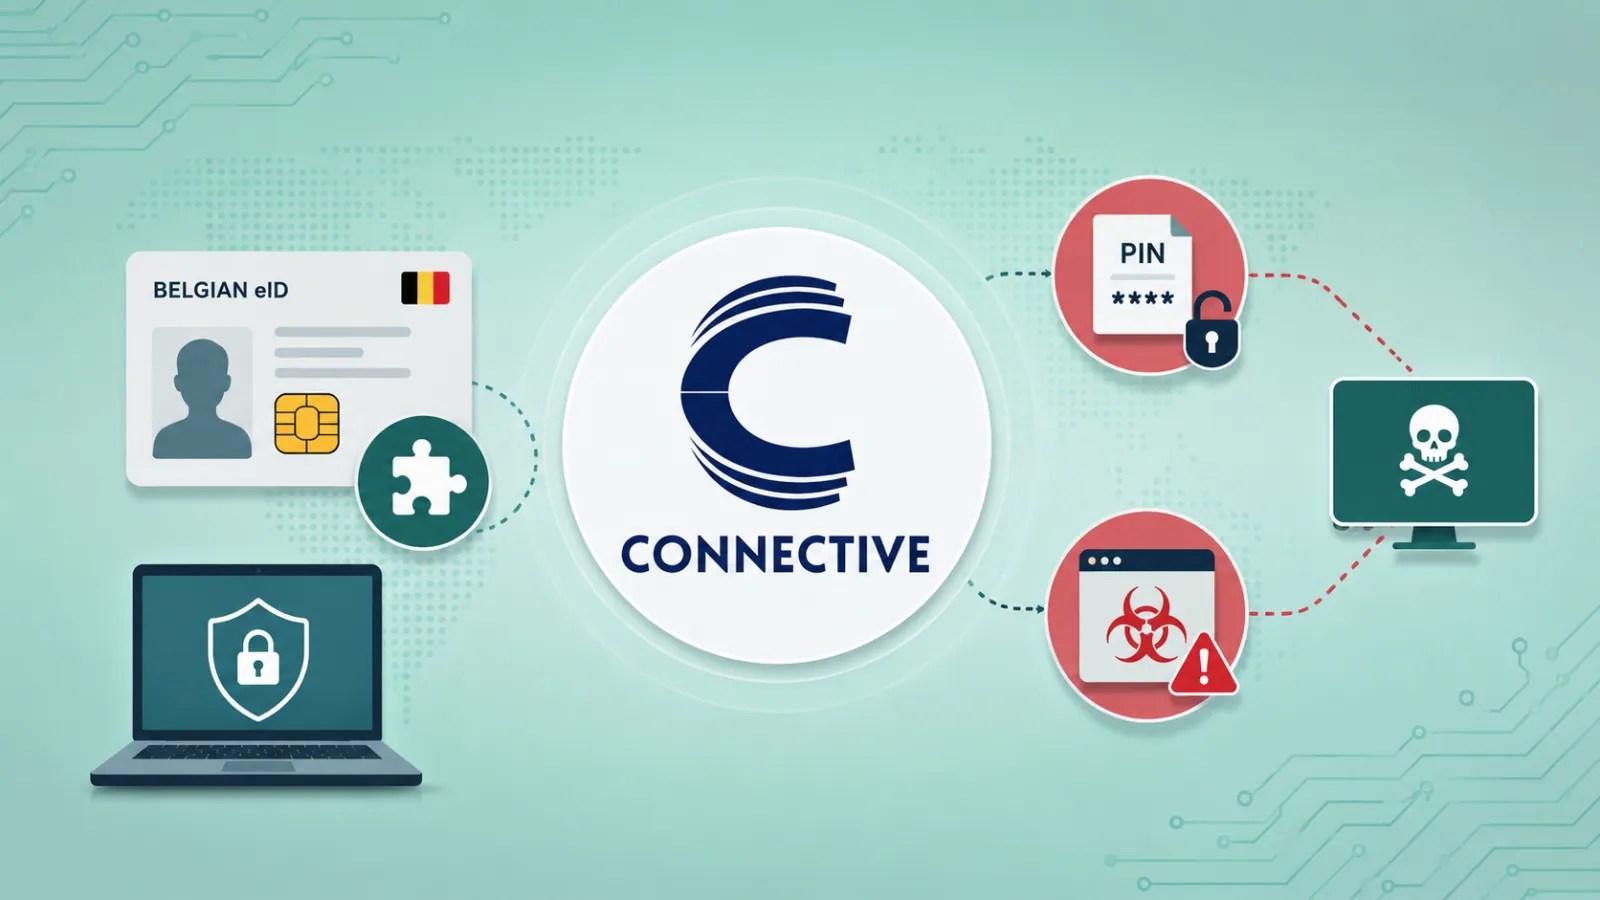
Significant vulnerabilities have been identified and addressed in the Connective Signing Extension, a widely used browser component by over 2 million Belgian users for accessing electronic identity cards and Maestro payment cards.

Potential Exploitation of User Data

The security flaws, which have now been patched, could have permitted malicious websites, advertisements, or concealed iframes to access card data, steal eID PINs, initiate fraudulent signing requests, and execute code controlled by attackers on Windows systems.

The Connective software functions as an intermediary between websites, a browser extension, and a native application on the user’s device, interfacing with smart-card readers for authentication and document signing.

Impact on Belgian Banking and Public Sector

This model is prevalent in Belgian banking and public services, including those using eIDAS-qualified electronic signatures, which are legally equivalent to handwritten signatures across the European Union.

Researchers from Have I Been Pwned identified a flaw where requests were not adequately bound to their originating websites. Although most commands necessitated an activation token, these tokens lacked sufficient origin protection.

This vulnerability allowed a token issued to a legitimate site to be reused by another site, enabling an attacker-controlled page to interact with the native host and extract data from Belgian eID or Maestro cards without significant user knowledge.

Risks of PIN Verification and Remote Code Execution

A critical flaw in the PIN verification process allowed malicious websites to display Connective PIN dialogs with attacker-controlled titles and messages, potentially deceiving users into entering their PINs under the guise of trusted services.

This could result in the exposure of a user’s eID PIN to malicious sites following a phishing attack, allowing unauthorized authentication or signing with an accessible eID card.

Additionally, a drive-by remote code execution issue was discovered, where a command executed on the native host could load a library from a path specified by a web request. This could allow attackers to execute malicious code at the user’s privilege level without requiring an eID card connection.

Response and Remediation by Nitro Software

The fallout extended beyond individual identity theft, as Belgian eID workflows are used for accessing high-value services. A compromised signing capability could facilitate account takeovers or fraudulent identity verification.

Nitro Software Belgium, the organization behind Connective, and an EU-listed Qualified Trust Service Provider, issued fixes in stages to address these vulnerabilities.

The final remediation involved disabling the risky library-loading feature, altering PIN-token handling so websites receive only a reference value, and enforcing origin checks for requests. These measures were completed 146 days post initial report, with no CVEs assigned at the time.

Stay informed on cybersecurity developments and safeguard your digital identity by integrating security solutions into your operations.

Cyber Security News Tags:Belgium, browser extension, Connective, CSAM, Cybersecurity, eID, EU eIDAS, identity theft, identity verification, Nitro Software, PIN security, remote code execution, security flaws, web security

Post navigation

Previous Post: Critical SQL Flaw Patched by Metabase Amid Zero-Day Exploit
Next Post: Cyberattacks Target Water Systems in New Jersey and Alabama

Related Posts

Google Engineer Accused of .2 Million Insider Trading Google Engineer Accused of $1.2 Million Insider Trading Cyber Security News
ClickFix Malware Attacks macOS Users to Steal Login Credentials ClickFix Malware Attacks macOS Users to Steal Login Credentials Cyber Security News
SmarterTools SmarterMail Vulnerability Enables Remote Code Execution Attack SmarterTools SmarterMail Vulnerability Enables Remote Code Execution Attack Cyber Security News
Global Effort Shuts Down 45,000 Malicious IPs in Cybercrime Sweep Global Effort Shuts Down 45,000 Malicious IPs in Cybercrime Sweep Cyber Security News
Hundreds of GitHub Malware Repos Targeting Novice Cybercriminals Linked to Single User Hundreds of GitHub Malware Repos Targeting Novice Cybercriminals Linked to Single User Cyber Security News
Threat Actors Attack PayPal Users in New Account Profile Set up Scam Threat Actors Attack PayPal Users in New Account Profile Set up Scam Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Innovative Method Challenges RSA Security Without Factoring
  • AI-Induced Hacks Challenge Legal Frameworks
  • SCOUTz Launches Beta for MSPs with New Intelligence Platform
  • AI Search Poisoning and Security Risks: Key Cyber News
  • Hackers Target Critical VPN Flaws in Check Point Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Innovative Method Challenges RSA Security Without Factoring
  • AI-Induced Hacks Challenge Legal Frameworks
  • SCOUTz Launches Beta for MSPs with New Intelligence Platform
  • AI Search Poisoning and Security Risks: Key Cyber News
  • Hackers Target Critical VPN Flaws in Check Point Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark