Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
DreamHost Initiates Password Resets After Security Incident

DreamHost Initiates Password Resets After Security Incident

Posted on October 27, 2026 By CWS

DreamHost has implemented a mandatory password reset for certain email and FTP/SFTP accounts due to a recent security incident. This measure follows disruptions to the company’s webmail and File Manager services, which prevented users from accessing their accounts until new passwords were set.

Precautionary Measures Following Service Disruptions

While DreamHost has labeled the password resets as a precaution, the company has not yet provided specific details about the cause of the incident or confirmed if any data was compromised. The issue initially surfaced on October 23, 2026, when users began experiencing connectivity problems with the File Manager.

Subsequent reports indicated similar issues with webmail services, prompting the expansion of password resets to include FTP/SFTP accounts. By October 26 at 3:35 p.m. PDT, DreamHost engineers had restored File Manager functionality and continued to monitor the situation, although password changes remained necessary for users.

Guidance for Affected Users

Initially, DreamHost advised account holders to await instructions, as any manual password changes made before the company’s reset process could be overridden. However, by October 24, the company confirmed that users could safely update their passwords directly through the DreamHost control panel without waiting for further notification.

As of October 25 at 9:32 p.m. PDT, instructions had been distributed to all impacted users. DreamHost also resolved a specific “Failed to edit” error, which had previously hindered some Professional Email customers from changing their passwords.

Maintaining Account Security

DreamHost reassures users that even during login disruptions, affected mailboxes continue to receive messages, and FTP/SFTP data remains intact on their servers. Users are encouraged to access panel.dreamhost.com directly to modify mailbox passwords under “Mail > Manage Email” or update file access credentials through “Websites > SFTP Users & Files.”

Additionally, DreamHost advises users to review mailbox forwarding settings and remove any unfamiliar entries to enhance security. New credentials should be communicated through secure channels, avoiding reliance on potentially compromised DreamHost email accounts.

Unlike the notable GoDaddy security breach, DreamHost has not identified any attackers, malware, or specific entry points associated with this incident. The password reset requirement alone does not confirm data theft or unauthorized access.

DreamHost emphasizes that it will never request password information via email. Users are urged to access the control panel directly and avoid following login links in email notifications. As investigations continue, the key questions of the incident’s origin, scope, and any potential unauthorized access remain unresolved.
Cyber Security News Tags:account security, Cybersecurity, data protection, DreamHost, email security, File Manager, FTP, password resets, security incident, SFTP, system update, user instructions, Webmail

Post navigation

Previous Post: Anthropic’s IPO Highlights AI Risks and Challenges

Related Posts

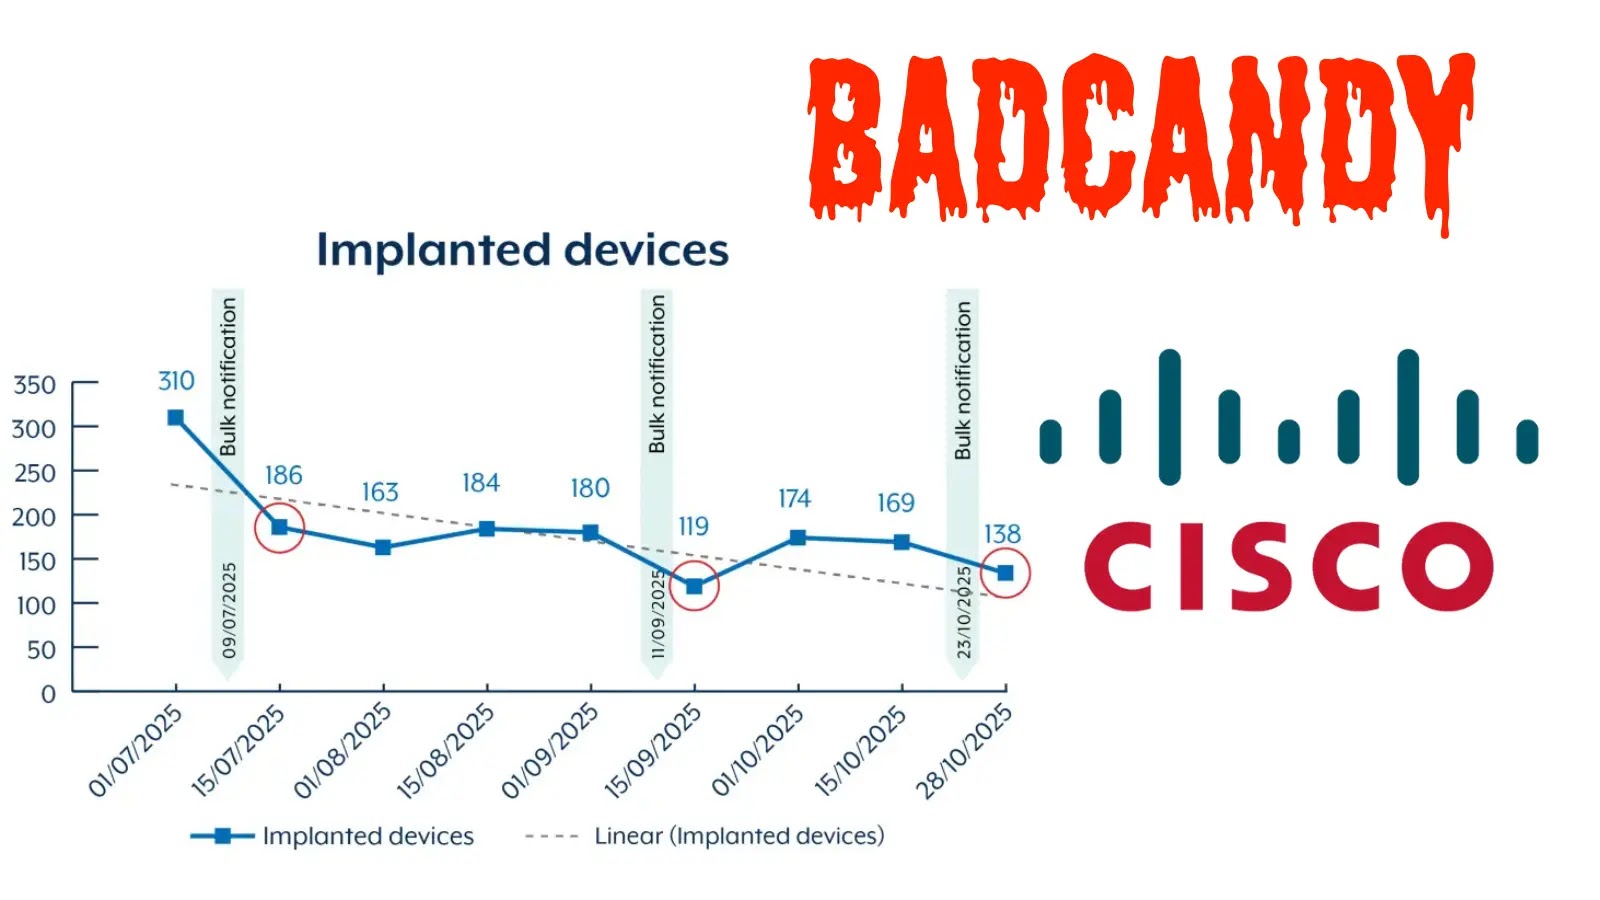
Hackers Exploiting Cisco IOS XE Vulnerability in the Wild to Deploy BADCANDY Web Shell Hackers Exploiting Cisco IOS XE Vulnerability in the Wild to Deploy BADCANDY Web Shell Cyber Security News
Beware of GTA 6 Scam Sites Exploiting Gamers Beware of GTA 6 Scam Sites Exploiting Gamers Cyber Security News
Google Announces Public Preview of Alert Triage and Investigation Agent used in Google Security Operations Google Announces Public Preview of Alert Triage and Investigation Agent used in Google Security Operations Cyber Security News
How Threat Intelligence Enhances SOC Analysts’ Efficiency How Threat Intelligence Enhances SOC Analysts’ Efficiency Cyber Security News
Lazarus APT Hackers Using ClickFix Technique to Steal Sensitive Intelligence Data Lazarus APT Hackers Using ClickFix Technique to Steal Sensitive Intelligence Data Cyber Security News
Anthropic Launches Cyber Mission to Enhance Security Anthropic Launches Cyber Mission to Enhance Security Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • DreamHost Initiates Password Resets After Security Incident
  • Anthropic’s IPO Highlights AI Risks and Challenges
  • OpenAI Compaction Flaw Exposes Model Reasoning
  • Palo Alto Warns of Brotli Vulnerability in PAN-OS
  • Popcorn Time Updater Poses Massive Security Risk

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • DreamHost Initiates Password Resets After Security Incident
  • Anthropic’s IPO Highlights AI Risks and Challenges
  • OpenAI Compaction Flaw Exposes Model Reasoning
  • Palo Alto Warns of Brotli Vulnerability in PAN-OS
  • Popcorn Time Updater Poses Massive Security Risk

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark