Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Enhancing Security in a Rapidly Evolving Threat Landscape

Enhancing Security in a Rapidly Evolving Threat Landscape

Posted on October 30, 2026 By CWS

Adaptive security strategies have become increasingly vital as cyber threats evolve at an unprecedented pace. The ability for malicious actors to quickly change their tactics during an attack, particularly with the aid of AI-enhanced operations, presents a dynamic challenge for cybersecurity professionals. This complex landscape demands that security measures be equally agile, ensuring that applications and APIs remain secure even as the threat environment shifts.

The Role of AI in Modern Cyber Threats

Artificial intelligence is now a significant factor in cyber threats, enabling attackers to dynamically adjust their methods in real-time. A 2026 analysis by Anthropic highlighted the use of AI in 832 banned accounts, illustrating a shift towards autonomous execution and live operational changes. This reality creates a moving target for defenders, as applications and environments themselves are constantly evolving, from on-premises infrastructures to multicloud setups and edge computing.

While traditional preventive controls and threat detection remain crucial, security systems must also monitor live application and API activity. This approach allows defenders to discern patterns and respond to threats as they develop, rather than relying solely on established signatures and known behaviors.

Adapting to Shifting Attack Patterns

Security teams face the challenge of identifying malicious activities that deviate from expected patterns. Attackers often modify their strategies, such as altering API requests or exploiting legitimate functionalities, to bypass traditional defenses. This necessitates a deeper understanding of attacker behavior in real-time, observing changes in request sequences, endpoint interactions, and access patterns.

Industry research indicates that nearly half of organizations update their production APIs daily, yet only a minority maintain a continuously updated API inventory. This highlights the dual challenge of managing an ever-changing application estate alongside unpredictable threat activities.

Ensuring Continuous Security Readiness

To effectively counter adaptive threats, security measures must extend beyond visibility to include robust enforcement capabilities. Real-time application traffic analysis should inform policy enforcement, allowing for immediate responses to suspicious activities without disrupting legitimate operations. This balance is crucial for protecting critical systems, such as payment processing and healthcare platforms, which require uninterrupted service.

As applications span multiple environments, maintaining consistent security across these diverse landscapes is essential. This involves a unified view of application traffic and the capability to respond to threats consistently, regardless of the underlying infrastructure.

Ultimately, the goal is to ensure that security measures are sufficiently agile to recognize and react to changes in threat behavior, preserving application availability while preventing malicious activities from causing operational impacts. Organizations that can swiftly adapt their protections while maintaining business continuity will lead in achieving cyber resilience in this rapidly changing threat landscape.
Cyber Security News Tags:AI threats, API management, application security, business continuity, cyber resilience, Cybersecurity, hybrid multicloud, runtime detection, security enforcement, threat intelligence

Post navigation

Previous Post: WordPress Security Flaw Faces 63,000 Exploitation Attempts
Next Post: NetamLoader Malware Targets Asian Government Windows 10 Systems

Related Posts

New ChatGPT Flaws Allow Attackers to Exfiltrate Sensitive Data from Gmail, Outlook, and GitHub New ChatGPT Flaws Allow Attackers to Exfiltrate Sensitive Data from Gmail, Outlook, and GitHub Cyber Security News
Hackers Use AI Systems for Cyber Attacks and Cryptocurrency Mining Hackers Use AI Systems for Cyber Attacks and Cryptocurrency Mining Cyber Security News
New Maranhão Stealer Via Pirated Software Leveraging Cloud-Hosted Platforms to Steal Login Credentials New Maranhão Stealer Via Pirated Software Leveraging Cloud-Hosted Platforms to Steal Login Credentials Cyber Security News
EvilTokens: A New Phishing Threat Targeting Microsoft Accounts EvilTokens: A New Phishing Threat Targeting Microsoft Accounts Cyber Security News
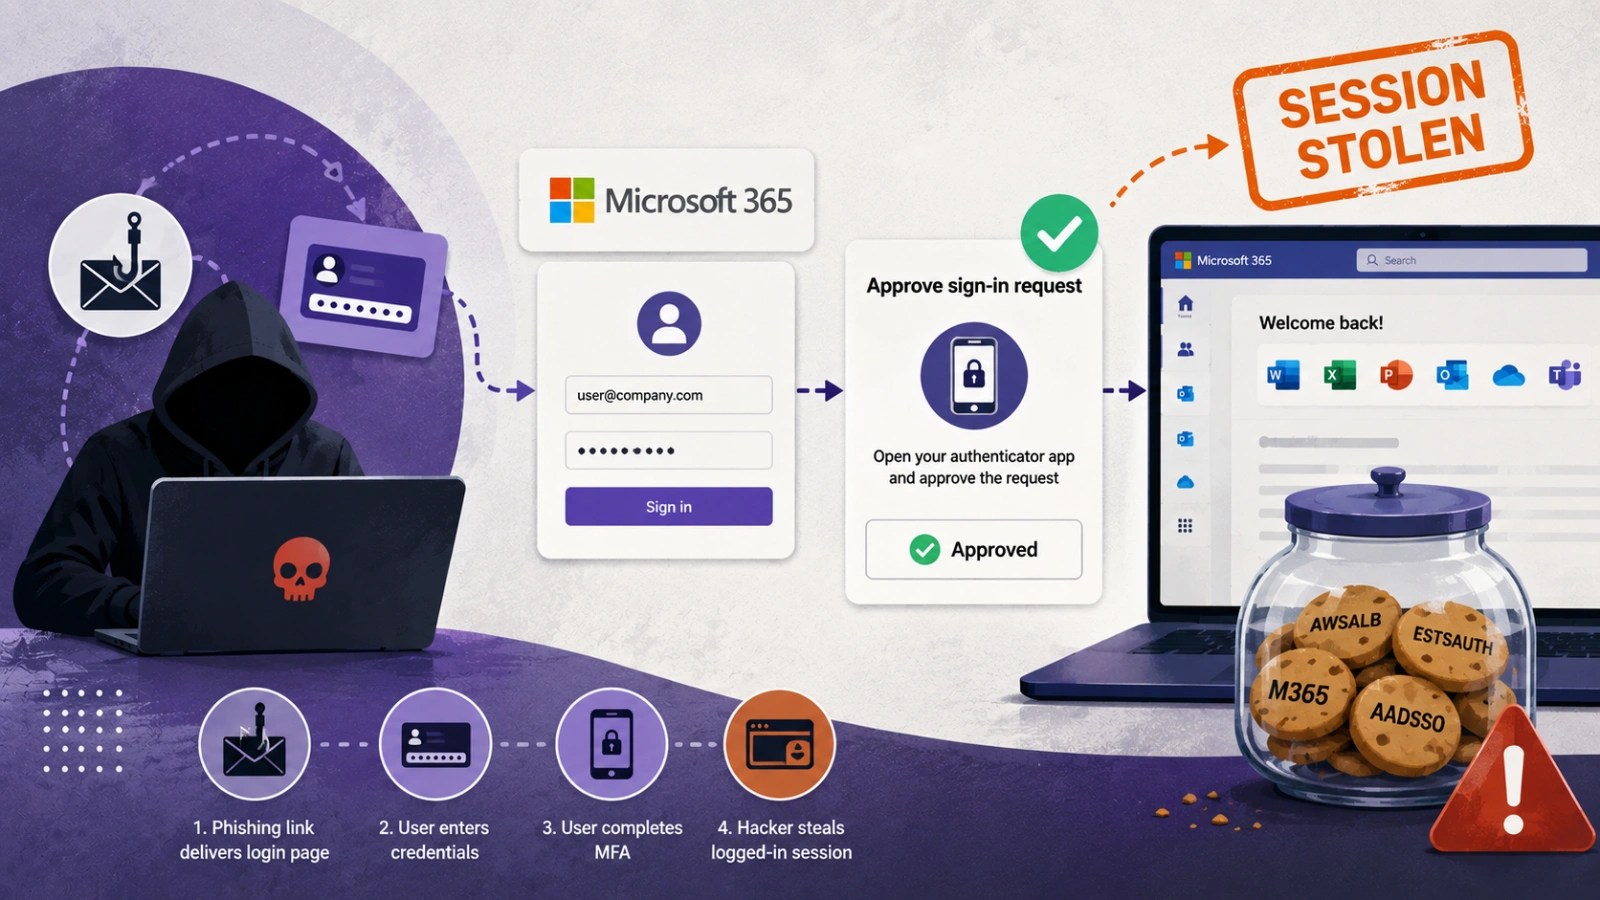
Hackers Exploit MFA to Hijack Microsoft 365 Sessions Hackers Exploit MFA to Hijack Microsoft 365 Sessions Cyber Security News
Critical Apache Tika Core Vulnerability Exploited by Uploading Malicious PDF Critical Apache Tika Core Vulnerability Exploited by Uploading Malicious PDF Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • NetamLoader Malware Targets Asian Government Windows 10 Systems
  • Enhancing Security in a Rapidly Evolving Threat Landscape
  • WordPress Security Flaw Faces 63,000 Exploitation Attempts
  • North Korean Hackers Exploit Developer Access for Malware
  • Massive $6 Billion Binance Hack Linked to North Korean Group

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • NetamLoader Malware Targets Asian Government Windows 10 Systems
  • Enhancing Security in a Rapidly Evolving Threat Landscape
  • WordPress Security Flaw Faces 63,000 Exploitation Attempts
  • North Korean Hackers Exploit Developer Access for Malware
  • Massive $6 Billion Binance Hack Linked to North Korean Group

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark