Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Exploited Microsoft SharePoint Flaws Risk RCE and Data Breaches

Exploited Microsoft SharePoint Flaws Risk RCE and Data Breaches

Posted on July 20, 2026 By CWS

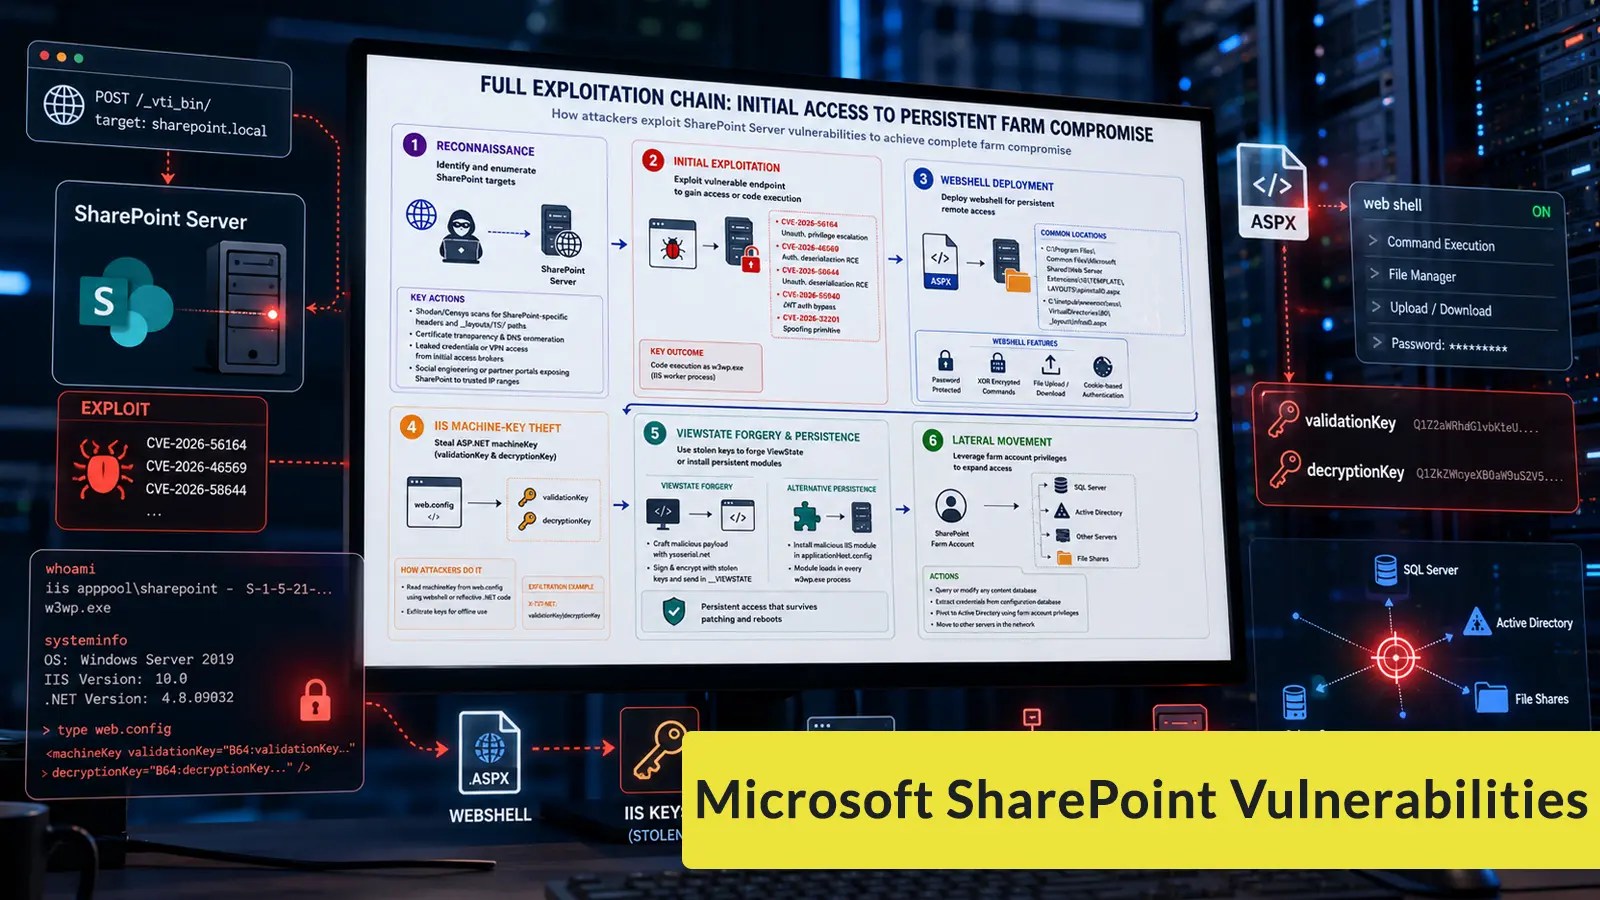
Recent findings reveal that vulnerabilities in Microsoft SharePoint Server are being actively exploited, posing significant risks such as remote code execution (RCE) and unauthorized data access. These exploits target on-premises SharePoint installations, threatening them with potential data breaches and ransomware attacks.

SharePoint Versions at Risk

The affected versions include SharePoint Server Subscription Edition, SharePoint Server 2019, and SharePoint Server 2016. Attackers are exploiting weaknesses in authentication and data processing, allowing them to penetrate corporate networks via exposed collaboration servers.

Research by Resecurity indicates that these attacks quickly escalate from initial web requests to deeper intrusions, affecting SharePoint, IIS, SQL Server, and Active Directory systems. The exploitation of these vulnerabilities remains a concern for public-facing SharePoint infrastructures.

Details of the Exploited Vulnerabilities

The critical vulnerabilities include CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164, all listed in CISA’s Known Exploited Vulnerabilities catalog. These flaws enable attackers to execute remote code and bypass authentication, resulting in unauthorized access and persistent web shell installations.

Particularly concerning is the theft of ASP.NET machineKey values from SharePoint configuration files, which could allow attackers to generate trusted ViewState data, maintaining access even after initial vulnerabilities are resolved.

Mitigating the Threats

Organizations are advised to apply Microsoft’s recent security updates across all SharePoint servers promptly. It is crucial to prioritize these systems for threat hunting and incident response activities.

Additional security measures include enabling AMSI integration, using Full Request Body Scan mode, and restricting direct internet exposure. Regular monitoring of IIS, Windows Event, and SharePoint ULS logs for unusual activities is also recommended to detect potential compromises.

In case of suspected breaches, isolating affected servers and resetting credentials are essential steps. Rotating IIS machine keys should only be considered after ensuring the environment is clear of threats.

By implementing these strategies, organizations can significantly reduce the risk of SharePoint server exploits and safeguard their networks against potential cyber threats.

Cyber Security News Tags:authentication bypass, cryptographic keys, Cybersecurity, data breach, IIS, Microsoft, RCE, SharePoint, SharePoint Server 2019, Vulnerabilities, web shell

Post navigation

Previous Post: Ernst & Young Data Breach Compromises Sensitive Information
Next Post: Mythos’ Impact on Exposure Windows in Security Programs

Related Posts

DinDoor Backdoor Exploits Deno and MSI for Stealth Attacks DinDoor Backdoor Exploits Deno and MSI for Stealth Attacks Cyber Security News
AI Model Identifies Significant Firefox Vulnerabilities AI Model Identifies Significant Firefox Vulnerabilities Cyber Security News
PickleScan 0-Day Vulnerabilities Enable Arbitrary Code Execution via Malicious PyTorch Models PickleScan 0-Day Vulnerabilities Enable Arbitrary Code Execution via Malicious PyTorch Models Cyber Security News
Buterat Backdoor Attacking Enterprises to Establish Persistence and Control Endpoints Buterat Backdoor Attacking Enterprises to Establish Persistence and Control Endpoints Cyber Security News
Critical Flaw Found in Fortinet FortiSandbox, Urgent Patch Required Critical Flaw Found in Fortinet FortiSandbox, Urgent Patch Required Cyber Security News
AI-Powered VoidLink Malware Framework Poses New Cyber Threat AI-Powered VoidLink Malware Framework Poses New Cyber Threat Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Ex-OpenAI Engineer Held for Alleged Spying with Saudi Ties
  • AI-Driven Attacks Target Over 100 Companies, Cost $5,000
  • SBI Alleged Data Breach: Hackers Claim Access to Vast Database
  • ROMULUS Platform Exploited by Hackers for Malware Distribution
  • AI Uncovers Hidden Cryptocurrency Miner on Mac

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Ex-OpenAI Engineer Held for Alleged Spying with Saudi Ties
  • AI-Driven Attacks Target Over 100 Companies, Cost $5,000
  • SBI Alleged Data Breach: Hackers Claim Access to Vast Database
  • ROMULUS Platform Exploited by Hackers for Malware Distribution
  • AI Uncovers Hidden Cryptocurrency Miner on Mac

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark