Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
GitSpawn Vulnerabilities Risk AI Coding Agents

GitSpawn Vulnerabilities Risk AI Coding Agents

Posted on September 2, 2026 By CWS

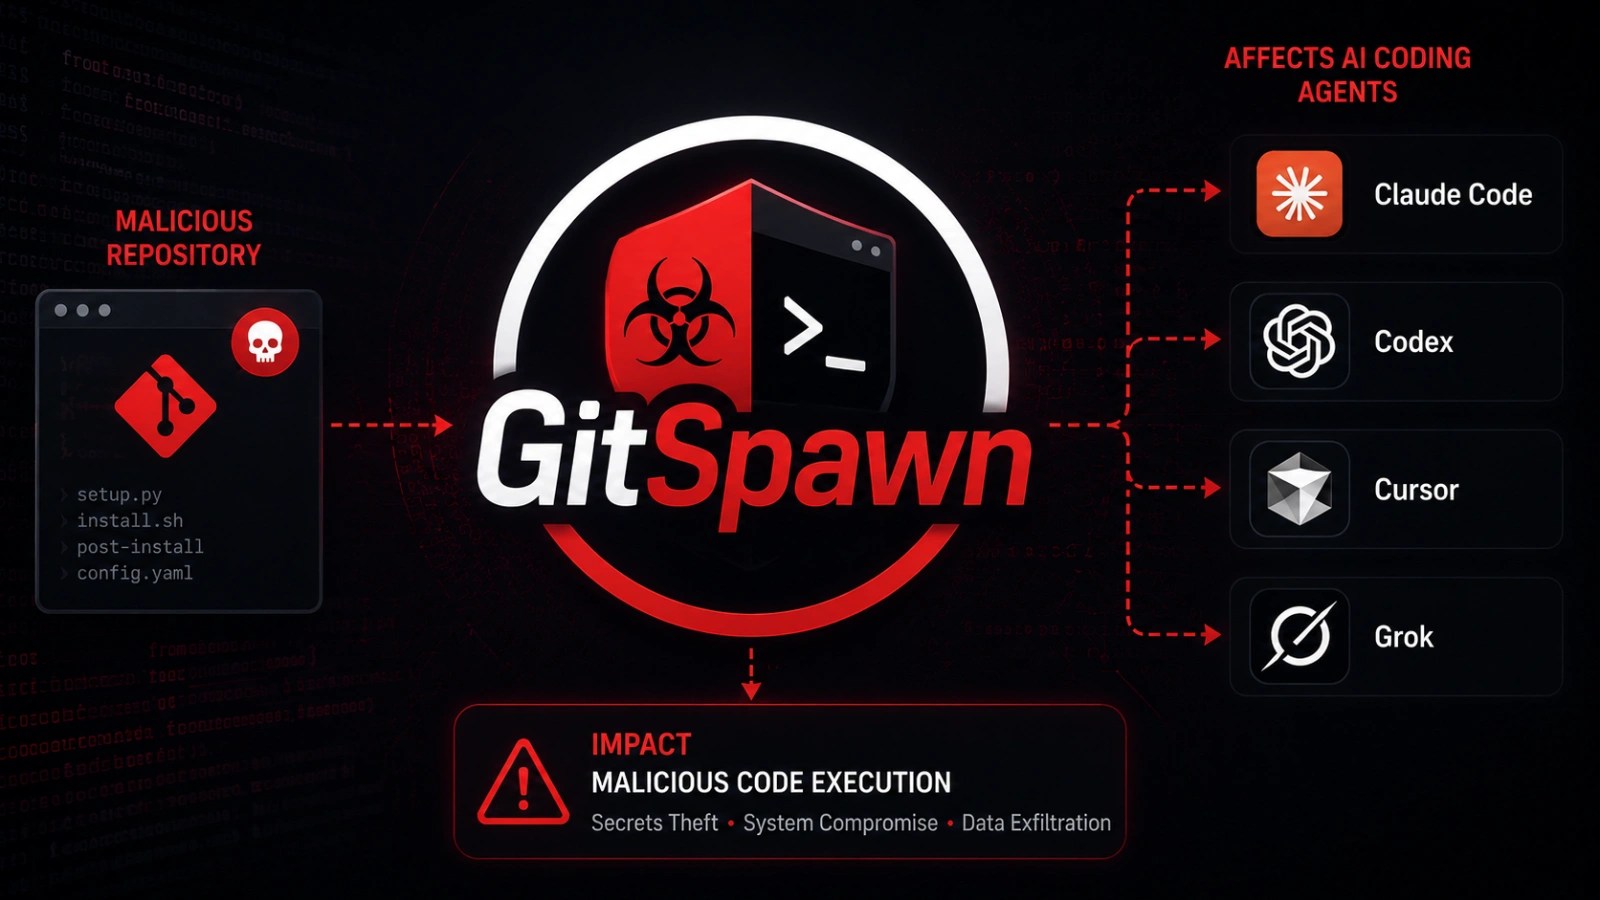
A newly identified set of vulnerabilities, termed GitSpawn, poses a significant risk to developers using AI coding agents. These vulnerabilities allow malicious repositories to execute code on a user’s system as soon as they are opened, without any user interaction or authentication. This alarming discovery was made by security researchers at Manifold Security, who detailed their findings in a recent technical disclosure.

Understanding GitSpawn Vulnerabilities

The researchers examined the startup processes of various command-line interface (CLI) based coding agents. It was found that many agents execute git commands such as git status or git diff automatically to gather project context. This behavior, though common, triggers a refresh of git’s internal index, which is exploited by the GitSpawn vulnerabilities.

Git’s core.fsmonitor setting is at the core of this issue. This setting allows a repository to specify a helper program that runs whenever the index is refreshed. Since this program is read from the repository’s .git/config file, a malicious repository can embed harmful commands that execute with the user’s privileges, bypassing any existing permission checks.

Impact on Popular AI Coding Tools

The vulnerability affects several popular AI coding tools, including Claude Code, Goose, Hermes Agent, Qwen Code, and Grok Build. Together, these tools have amassed nearly half a million stars on GitHub, with Claude Code alone accounting for over 77 million monthly npm downloads. These tools are compromised when they open a repository containing a malicious .git/config file.

OpenAI’s Codex and Cursor were also vulnerable, though patches have been issued following independent reports. Despite these efforts, four critical issues remain unaddressed, including a distinctive flaw in Claude Code’s ultrareview command.

Mitigation and Recommendations

To protect against these vulnerabilities, developers are advised to scrutinize the .git/config file of any repository received as raw files. This precaution is crucial to prevent unauthorized code execution when using AI agents.

Vendors are encouraged to sanitize git configurations during background operations, such as by disabling the core.fsmonitor setting. This proactive measure could prevent this class of vulnerabilities from being exploited.

As the security landscape evolves, it is imperative for developers and vendors to remain vigilant and update their practices to safeguard against emerging threats like GitSpawn.
Cyber Security News Tags:AI coding agents, Claude Code, code execution, Codex, core.fsmonitor, Cursor, Cybersecurity, Git configuration, GitSpawn, Goose, Grok Build, Hermes agent, repository security, security vulnerability, Software Security

Post navigation

Previous Post: OpenLeash Enhances AI Security with Human Oversight
Next Post: Authorities Dismantle Sality Botnet, Halting Malware Spread

Related Posts

INE Named to Training Industry’s 2025 Top 20 Online Learning Library List INE Named to Training Industry’s 2025 Top 20 Online Learning Library List Cyber Security News
Predator Spyware Compamy Used 15 Zero-Days Since 2021 to Target iOS Users Predator Spyware Compamy Used 15 Zero-Days Since 2021 to Target iOS Users Cyber Security News
Horabot Trojan Targets Mexico with Phishing Campaign Horabot Trojan Targets Mexico with Phishing Campaign Cyber Security News
Guided Selling in 3D Product Configurators Guided Selling in 3D Product Configurators Cyber Security News
Indonesia’s Gambling Ecosystem Exposed With Indicators of National-Level Cyber Operations Indonesia’s Gambling Ecosystem Exposed With Indicators of National-Level Cyber Operations Cyber Security News
Vibe-Coded Malware Campaign Exploits AI to Spread Vibe-Coded Malware Campaign Exploits AI to Spread Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Claude AI Unravels 25-Year NSA Cryptography Enigma Swiftly
  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Claude AI Unravels 25-Year NSA Cryptography Enigma Swiftly
  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark