Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Bypass Microsoft Defender with Fake Installers

Hackers Bypass Microsoft Defender with Fake Installers

Posted on September 2, 2026 By CWS

Hackers linked to the Silver Fox group have been utilizing fake software installers to infiltrate Windows systems, effectively undermining the defenses designed to protect these systems. This method has targeted various sectors, including healthcare, manufacturing, and education, putting numerous organizations at risk.

Deceptive Download Tactics

The attackers employ convincing download pages that mimic reputable software brands, enticing users to download seemingly legitimate files. This campaign has primarily impacted China-based operations or Chinese-speaking users, though it has the potential to extend across different industries.

Microsoft analysts have linked this activity to the Silver Fox campaign, also known as Yinhu, with moderate confidence. Although not attributed to any nation-state, the malware effectively establishes a foothold, lowers defenses, and communicates with servers controlled by the attackers.

Technical Details and Modus Operandi

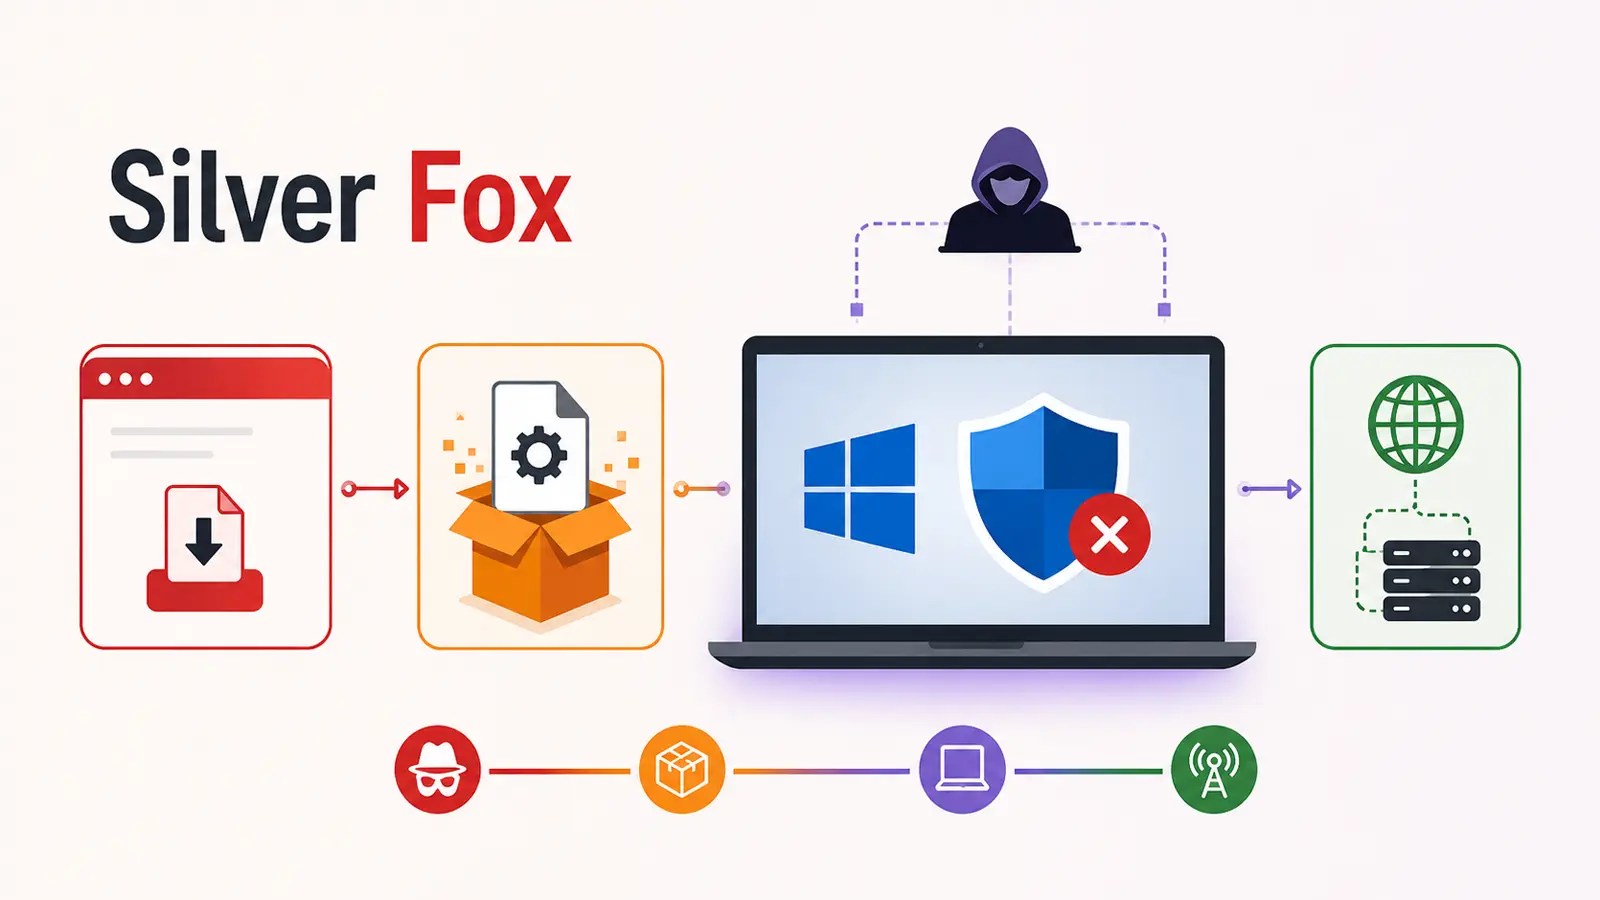
The campaign begins on websites that imitate well-known vendors like Razer and Microsoft Edge. When users click ‘Download now,’ they receive a ZIP file that changes with each request, making it difficult to block based on file names alone. This method mirrors other fake installer malware tactics, exploiting familiar branding to make the malicious download seem benign.

Upon opening the archive, a wrapper executes an installer in a randomly named directory. Using Windows Installer, the malicious code runs through a trusted component, deceiving the user into believing a legitimate installation is occurring. The payloads then create tasks with innocuous names, such as Deadline Mission Target, to maintain persistence by restarting every minute.

Compromise and Mitigation Strategies

The malware further establishes control by creating tasks with SYSTEM privileges, adding Microsoft Defender exclusions, and employing PowerShell to manipulate code integrity policies. It also deletes volume shadow copies to hinder recovery and disables Windows Update services, complicating detection and response efforts.

Organizations are advised to confine downloads to verified sources and treat any unexpected ZIP files with suspicion. Web and email controls should block known malicious delivery routes, while IT teams should monitor unusual executable activity and changes to scheduled tasks.

Conclusion and Recommendations

To minimize the risk of compromise, security administrators should enable tamper and network protection alerts and monitor for changes in Defender exclusions and attempts to disable update services. Users should avoid opening questionable installers and download applications directly from official sources. Swift isolation of affected systems and thorough investigation of network connections are crucial to preventing further breaches.

By prioritizing the identification of spoofed downloads, randomly staged executables, and system task creation, security teams can better defend against these sophisticated threats. Maintaining vigilance and up-to-date threat intelligence is essential for robust cybersecurity defenses.
Cyber Security News Tags:cyber attack, Cybersecurity, endpoint security, fake installers, IT security, Malware, malware prevention, Microsoft Defender, network protection, Silver Fox, software vulnerabilities, system compromise, threat intelligence, Windows security, Yinhu

Post navigation

Previous Post: Urgent Patch Needed for Cleo Harmony Security Flaw
Next Post: Malicious Update Exploits BGP Hijack in Virtualizor

Related Posts

Apache Tomcat Coyote Vulnerability Let Attackers Trigger DoS Attack Apache Tomcat Coyote Vulnerability Let Attackers Trigger DoS Attack Cyber Security News
CISOs Guide to Regulatory Compliance in Global Landscapes CISOs Guide to Regulatory Compliance in Global Landscapes Cyber Security News
Palo Alto Networks Addresses 11 Security Flaws in Latest Update Palo Alto Networks Addresses 11 Security Flaws in Latest Update Cyber Security News
Urgent Security Alert for Microsoft Exchange Server Flaw Urgent Security Alert for Microsoft Exchange Server Flaw Cyber Security News
Microsoft Enforces Mandatory MFA for Microsoft 365 Admin Center Logins Microsoft Enforces Mandatory MFA for Microsoft 365 Admin Center Logins Cyber Security News
Beware of Fake AI Business Tools That Hides Ransomware Beware of Fake AI Business Tools That Hides Ransomware Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Urgent Patch for Major Check Point Vulnerability Released
  • Google Fixes Pixel Zero-Day Vulnerability Amid Attacks
  • Russian Enterprises Face Threats from Cyber Groups
  • TP-Link Camera Vulnerabilities Threaten User Privacy
  • AI-Driven Data Breach Notified to Spanish Authorities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark