Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Expose AI-Driven Attack System

Hackers Expose AI-Driven Attack System

Posted on September 28, 2026 By CWS

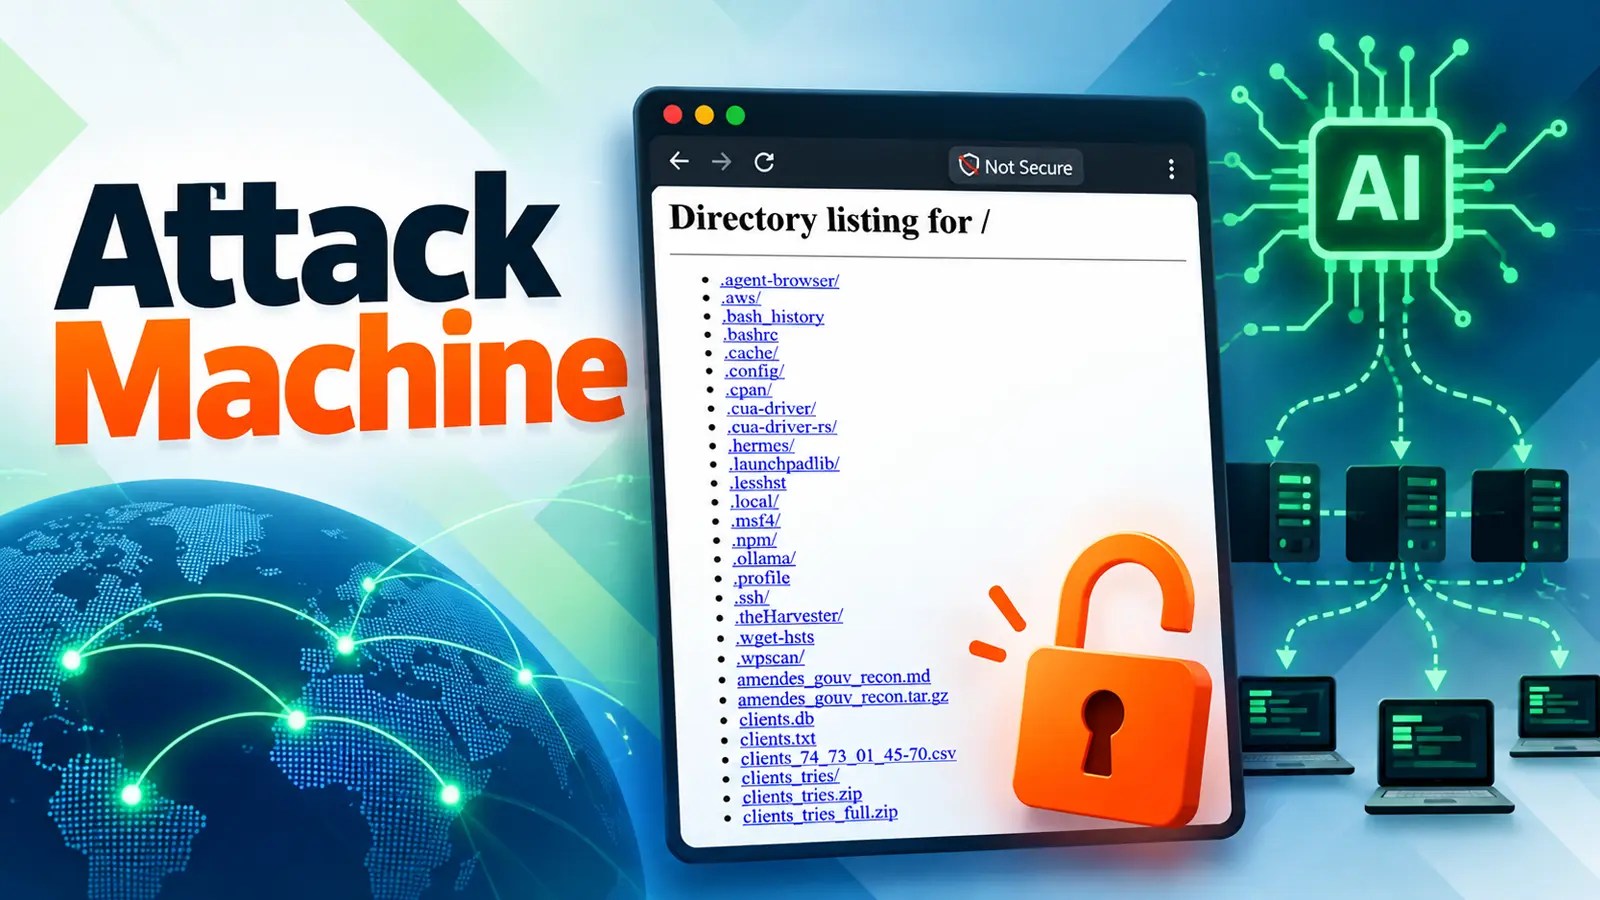
A hacker group associated with Blackhatsect0r and DXQRTXX inadvertently exposed its AI-powered attack system, revealing a trove of operational data. The system, designed to exploit internet vulnerabilities, was left unprotected, providing a rare glimpse into ongoing cyber activities.

The Unveiling of a Cyber Operation

The group’s infrastructure skillfully combined broad internet surveillance with targeted attacks. It identified weak points such as exposed services, leaked credentials, and poorly configured applications, organizing this data for future cyber exploits.

Security researchers discovered a staggering 16,415 credential records alongside approximately 498,000 target URLs. Among these were nearly 449 subdomains belonging to the French government. ThreatMon analysts uncovered this publicly accessible environment due to the absence of authentication controls.

Operational Missteps and Security Gaps

Ironically, despite the group’s discussions on operational security within their Telegram channel, they failed to secure key files, mapping out their activities. This incident underscores how minor configuration errors can amplify the impact of automated cyber attacks.

Rather than leveraging unknown vulnerabilities, the hackers focused on exploiting publicly exposed files and predictable credentials. Such oversights effectively opened avenues for potential breaches.

Automated Exploration and Exploitation

The exposed data portrays an operation designed for sustainability over sporadic attacks. Using a Go-based command framework and a Python-driven discovery tool, they persistently scanned for vulnerable systems, analyzing DNS data and certifying records to identify potential targets.

Reports previously tying this group to AI-driven operations now reveal a more automated discovery approach, rather than confirming AI-directed intrusions. The breached server displayed not just malware, but an array of operational credentials and exploit logs.

Telegram logs further revealed coordination among group members, hinting at a small but organized team. Their activities shifted focus from data theft to the distribution of offensive tools, possibly to democratize access to basic hacking resources.

Lessons in Cybersecurity

This case illustrates the necessity of robust security practices. Researchers highlighted attacks on both France’s ANTAI system and a cryptocurrency exchange, showing how exposed configuration files facilitated unauthorized access attempts.

Security teams should prioritize removing configuration files from public access, maintaining token-signing keys on secure servers, and replacing weak or default secrets. Continuous monitoring and remediation of suspicious activities can significantly reduce vulnerability windows.

Ultimately, the true threat lies in the increasing ease with which automated systems can exploit known flaws. Regular security audits and swift responses to suspicious activities are essential to maintaining a secure digital environment.
Cyber Security News Tags:AI attacks, automated scanning, configuration errors, cyber attack, cyber threat, Cybersecurity, data breach, data protection, exposed credentials, hacker group, internet security, network security, security breach, security vulnerability, threat intelligence

Post navigation

Previous Post: Security Flaw Enables $388M Theft from Bitget Exchange
Next Post: Apple Fixes CoreGraphics Vulnerability in Older OS

Related Posts

TrustAsia Revoked 143 Certificates Following LiteSSL ACME Service Vulnerability TrustAsia Revoked 143 Certificates Following LiteSSL ACME Service Vulnerability Cyber Security News
Threat Actors Leveraging Windows and Linux Vulnerabilities in Real-world Attacks to Gain System Access Threat Actors Leveraging Windows and Linux Vulnerabilities in Real-world Attacks to Gain System Access Cyber Security News
700+ Malicious Android Apps Abusing NFC Relay to Exfiltrate Banking Login Credentials 700+ Malicious Android Apps Abusing NFC Relay to Exfiltrate Banking Login Credentials Cyber Security News
Beware of Fake WinRAR Website That Delivers Malware with WinRAR Installer Beware of Fake WinRAR Website That Delivers Malware with WinRAR Installer Cyber Security News
QNAP NetBak Replicator Vulnerability Let Attackers Execute Unauthorized Code QNAP NetBak Replicator Vulnerability Let Attackers Execute Unauthorized Code Cyber Security News
CISA Adds Critical React2Shell Vulnerability to KEV Catalog Following Active Exploitation CISA Adds Critical React2Shell Vulnerability to KEV Catalog Following Active Exploitation Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Apple Fixes CoreGraphics Vulnerability in Older OS
  • Hackers Expose AI-Driven Attack System
  • Security Flaw Enables $388M Theft from Bitget Exchange
  • Microsoft Uncovers New Malware for Stealthy Network Access
  • IAM Frameworks for AI Agents: Ensuring Secure Operations

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Apple Fixes CoreGraphics Vulnerability in Older OS
  • Hackers Expose AI-Driven Attack System
  • Security Flaw Enables $388M Theft from Bitget Exchange
  • Microsoft Uncovers New Malware for Stealthy Network Access
  • IAM Frameworks for AI Agents: Ensuring Secure Operations

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark