Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
HEIC Image Vulnerability Leads to WordPress Security Risk

HEIC Image Vulnerability Leads to WordPress Security Risk

Posted on October 5, 2026 By CWS

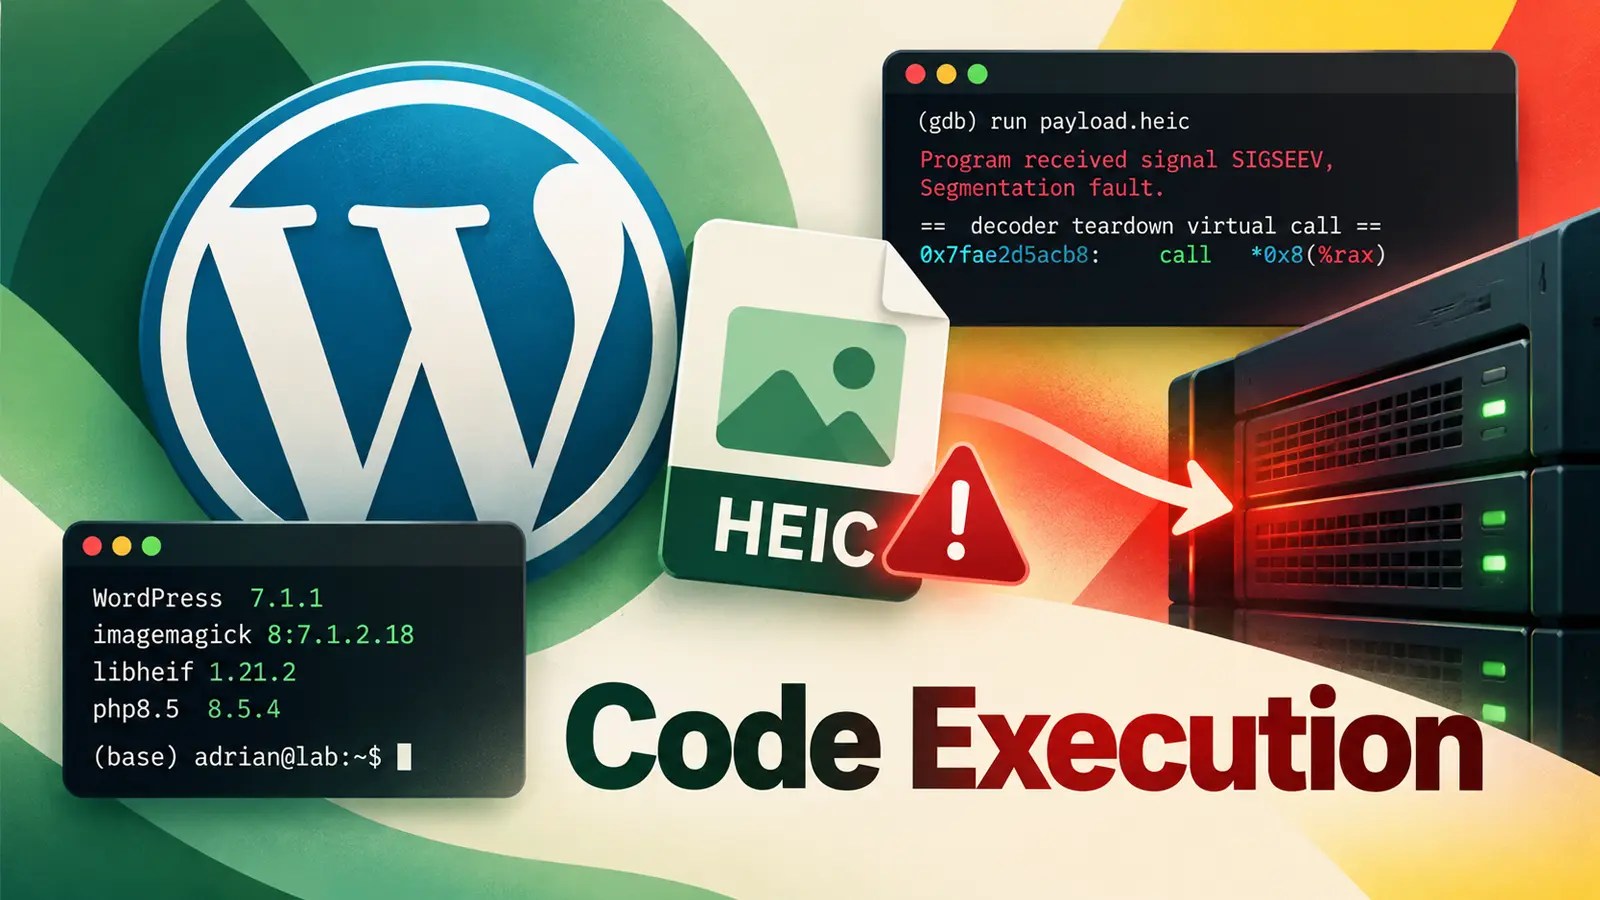
Security researchers have unveiled a potential threat involving HEIC images that can lead to remote code execution on WordPress servers. By exploiting an attack chain, an ordinary image upload can be manipulated to execute code within the PHP-FPM process that powers the site.

The Vulnerability in Image Processing

The root of this vulnerability lies in libheif, a component used to decode HEIC, HEIF, and AVIF files. When a WordPress server processes an image using ImageMagick, a specifically crafted file can take advantage of libheif’s weaknesses to corrupt memory, instead of generating a proper image.

Fortbridge researchers have identified a systematic approach that utilizes this flaw, combined with memory data leaked from WordPress-generated JPEGs, to execute malicious code. This discovery highlights the necessity of scrutinizing image uploads as much as other server-side inputs, especially when high-risk photo formats from modern devices are involved.

Exploitation Criteria and Impact

The attack scenario requires a logged-in WordPress user with permission to upload files, typically an Author or higher. While the findings are largely theoretical and have not yet been observed in active campaigns, they were successfully demonstrated on specific Linux software configurations.

The vulnerability, tracked as GHSA-x8r2-mggj-j6wr, affects the uncompressed image decoder in libheif. An attacker can craft a file to exploit a memory allocation error, causing overflow and potentially redirecting essential program operations.

Mitigation Strategies and Recommendations

To mitigate this risk, administrators are urged to update libheif to version 1.23.3 or later, addressing the vulnerability identified from versions 1.18.0 to 1.23.2. Additional precautionary measures include blocking HEIC and AVIF uploads, removing unnecessary codecs, and processing media in isolated environments.

Operators are advised to investigate any unusual PHP-FPM worker exits or HTTP 503 responses after HEIC uploads. Limiting writable paths and disabling script execution in upload directories can also help minimize damage in case of an exploit.

Although no active exploitation campaigns have been reported, the importance of proactive measures cannot be overstated. Regular updates and vigilance in monitoring server behavior are crucial in safeguarding against potential threats.
Cyber Security News Tags:Cybersecurity, Exploit, Fortbridge, HEIC, image processing, ImageMagick, libheif, PHP-FPM, remote code execution, security risk, server security, software patch, Vulnerability, web development, WordPress

Post navigation

Previous Post: Google Gemini’s Potential Full Access Could Affect Privacy
Next Post: Critical Microsoft Exchange Vulnerability Patched

Related Posts

New Magecart Skimmer Attack With Malicious JavaScript Injection to Skim Payment Data New Magecart Skimmer Attack With Malicious JavaScript Injection to Skim Payment Data Cyber Security News
CISA Adds ASUS Embedded Malicious Code Vulnerability to KEV List Following Active Exploitation CISA Adds ASUS Embedded Malicious Code Vulnerability to KEV List Following Active Exploitation Cyber Security News
Securing Multi-Cloud Infrastructures in 2025 Enterprise Deployments Securing Multi-Cloud Infrastructures in 2025 Enterprise Deployments Cyber Security News
Cavalry Werewolf APT Hackers Attacking Multiple Industries With FoalShell and StallionRAT Cavalry Werewolf APT Hackers Attacking Multiple Industries With FoalShell and StallionRAT Cyber Security News
Microsoft and Authorities Dismatles BEC Attack Chain Powered by RedVDS Fraud Engine Microsoft and Authorities Dismatles BEC Attack Chain Powered by RedVDS Fraud Engine Cyber Security News
New Chinese Nexus APT Hackers Attacking Organizations to Deliver NET-STAR Malware Suite New Chinese Nexus APT Hackers Attacking Organizations to Deliver NET-STAR Malware Suite Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Microsoft Exchange Vulnerability Patched
  • HEIC Image Vulnerability Leads to WordPress Security Risk
  • Google Gemini’s Potential Full Access Could Affect Privacy
  • Senate Approves Bill to Enhance Healthcare Cybersecurity
  • Weekly Cybersecurity Update: NetScaler, FortiMail Flaws

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Microsoft Exchange Vulnerability Patched
  • HEIC Image Vulnerability Leads to WordPress Security Risk
  • Google Gemini’s Potential Full Access Could Affect Privacy
  • Senate Approves Bill to Enhance Healthcare Cybersecurity
  • Weekly Cybersecurity Update: NetScaler, FortiMail Flaws

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark