Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Identifying Breaches: How Tier 1 SOC Analysts Decide

Identifying Breaches: How Tier 1 SOC Analysts Decide

Posted on June 30, 2026 By CWS

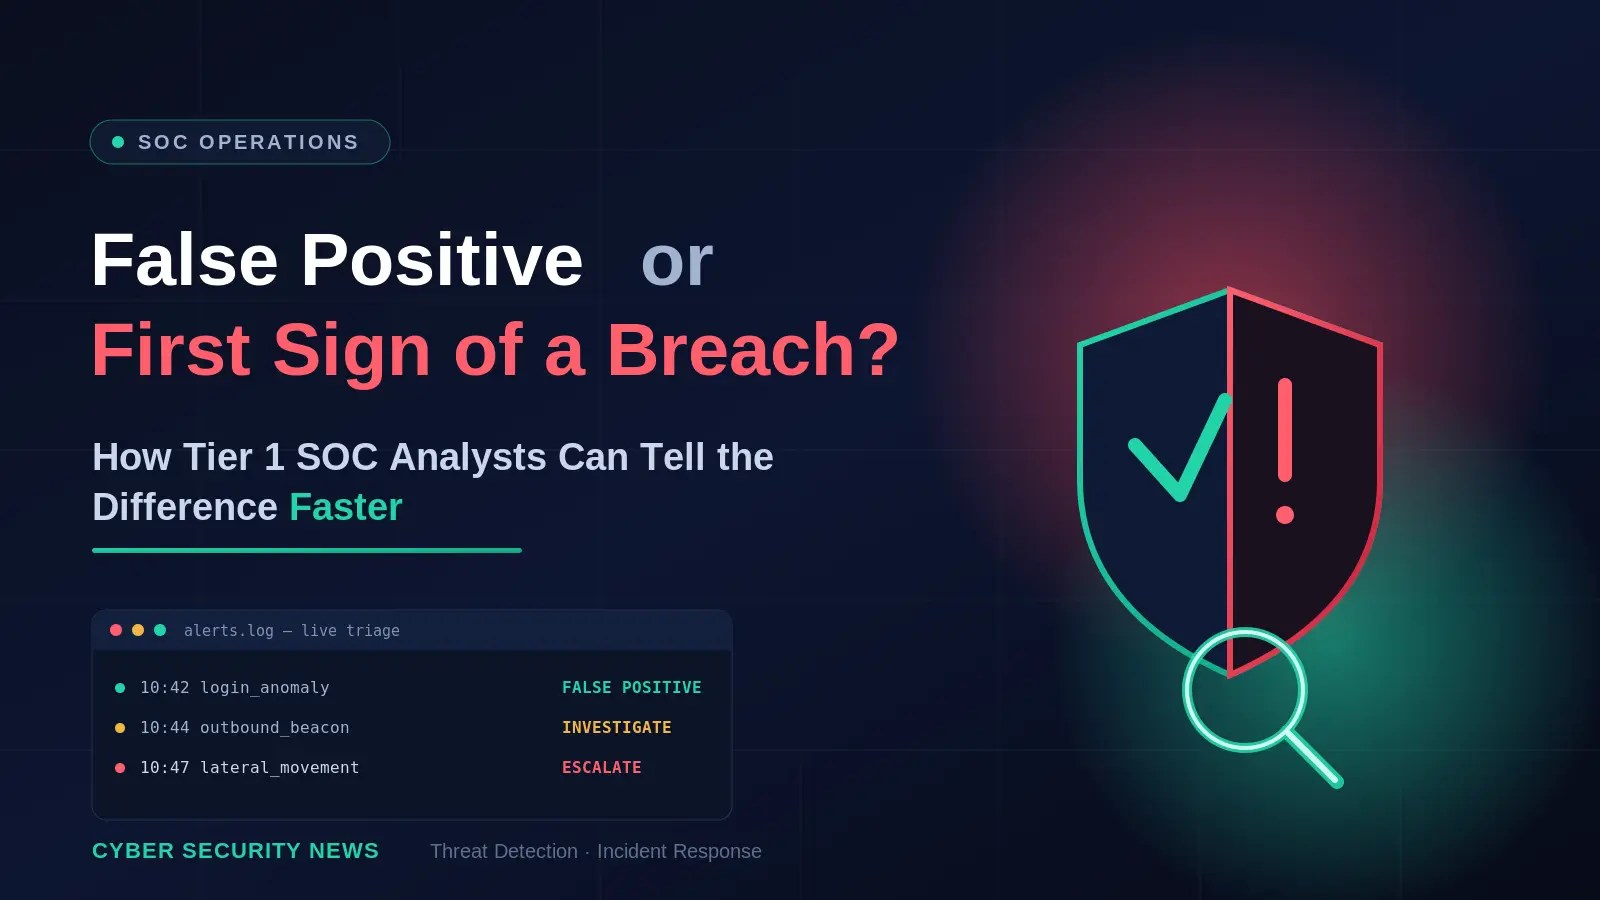
Security Operations Center (SOC) teams are on the frontline of cybersecurity, tasked with evaluating numerous alerts to distinguish between false positives and real threats. For Tier 1 SOC analysts, making swift and accurate decisions is essential to maintaining robust security defenses.

Understanding the Role of Tier 1 SOC Analysts

When an alert is triggered, such as a laptop connecting to an unfamiliar domain, the analyst must decide its significance. Initial alerts may not be dramatic—no malware or ransomware warning—but they are crucial signals that require evaluation. Analysts use various tools to determine if the domain is a new business or a potential phishing attempt.

This decision-making process is often complicated by fragmented evidence, which can delay action or lead to incorrect conclusions. The challenge lies in connecting Indicators of Compromise (IOCs) like domains or IPs to broader threat behaviors and infrastructure.

The Significance of Effective Triage

Effective triage in a SOC involves deciding whether an alert can be closed, monitored, escalated, or blocked. Poor triage can lead to false negatives, where threats go unnoticed, or false positives, which waste resources and obscure real threats. Tier 1 analysts need to piece together evidence to make informed decisions.

For Chief Information Security Officers (CISOs) and SOC leaders, efficient triage is crucial. It impacts incident response costs, analyst workload, and overall security posture. A key principle is evaluating IOCs not in isolation but in the context of associated behaviors and threats.

Utilizing Threat Intelligence for Better Decisions

Threat intelligence plays a pivotal role in helping analysts make quicker and more informed decisions. By employing platforms like ANY.RUN Threat Intelligence Lookup, analysts can gather comprehensive context around suspicious indicators. This includes examining connections to malware, phishing samples, and related domains or IPs.

Such intelligence allows analysts to transform isolated data points into actionable insights, improving the quality of decisions at the SOC’s frontlines. This approach not only speeds up the triage process but also enhances the accuracy of threat assessments.

The integration of threat intelligence into the broader security workflow ensures that alerts are enriched automatically, allowing for better detection and response strategies. This creates a feedback loop that strengthens SOC capabilities and reduces the time analysts spend switching between tools.

Conclusion: Enhancing SOC Efficiency

For SOC teams, the goal is not merely to handle more alerts but to make better decisions based on available evidence. This requires a structured workflow and reliable threat intelligence that contextualizes IOCs within broader threat landscapes.

By improving triage processes, analysts can effectively discern between routine noise and genuine breaches, enabling faster response and containment. This not only protects the organization but also alleviates analyst fatigue, ensuring that smaller threats do not escalate into significant business challenges.

Cyber Security News Tags:alert management, breach detection, Cybersecurity, false positives, incident response, malware detection, network security, security operations, SOC, threat intelligence, Tier 1 analysts

Post navigation

Previous Post: Aflac Japan Cyberattack Exposes 4.38 Million Customers
Next Post: Silent Swap Crypto Clipper Exploits Fake Extension

Related Posts

Rise in Scans Targeting SonicWall Firewall Interfaces Rise in Scans Targeting SonicWall Firewall Interfaces Cyber Security News
Claude Mythos AI Completes Cyber Kill Chain Autonomously Claude Mythos AI Completes Cyber Kill Chain Autonomously Cyber Security News
Critical Cisco IOS XR Vulnerabilities Demand Immediate Attention Critical Cisco IOS XR Vulnerabilities Demand Immediate Attention Cyber Security News
Major Security Breach at Loblaw: Customer Data Compromised Major Security Breach at Loblaw: Customer Data Compromised Cyber Security News
New Attack Technique That Enables Attackers To Exfiltrate Git Credentials In Argocd New Attack Technique That Enables Attackers To Exfiltrate Git Credentials In Argocd Cyber Security News
WinRAR Directory Vulnerability Let Execute Arbitrary Code Using a Malicious File WinRAR Directory Vulnerability Let Execute Arbitrary Code Using a Malicious File Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • FAA Imposes Nationwide Ground Stop Amid Safety Concerns
  • US Halts $2.7 Billion in North Korean Crypto Theft
  • Hackers Exploit Fake Emails to Spread XLoader Malware
  • Trezor Addresses Security Risks in Compromised Wallets
  • SANSAR Malware Masks Cryptocurrency Mining on Linux Servers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • FAA Imposes Nationwide Ground Stop Amid Safety Concerns
  • US Halts $2.7 Billion in North Korean Crypto Theft
  • Hackers Exploit Fake Emails to Spread XLoader Malware
  • Trezor Addresses Security Risks in Compromised Wallets
  • SANSAR Malware Masks Cryptocurrency Mining on Linux Servers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark