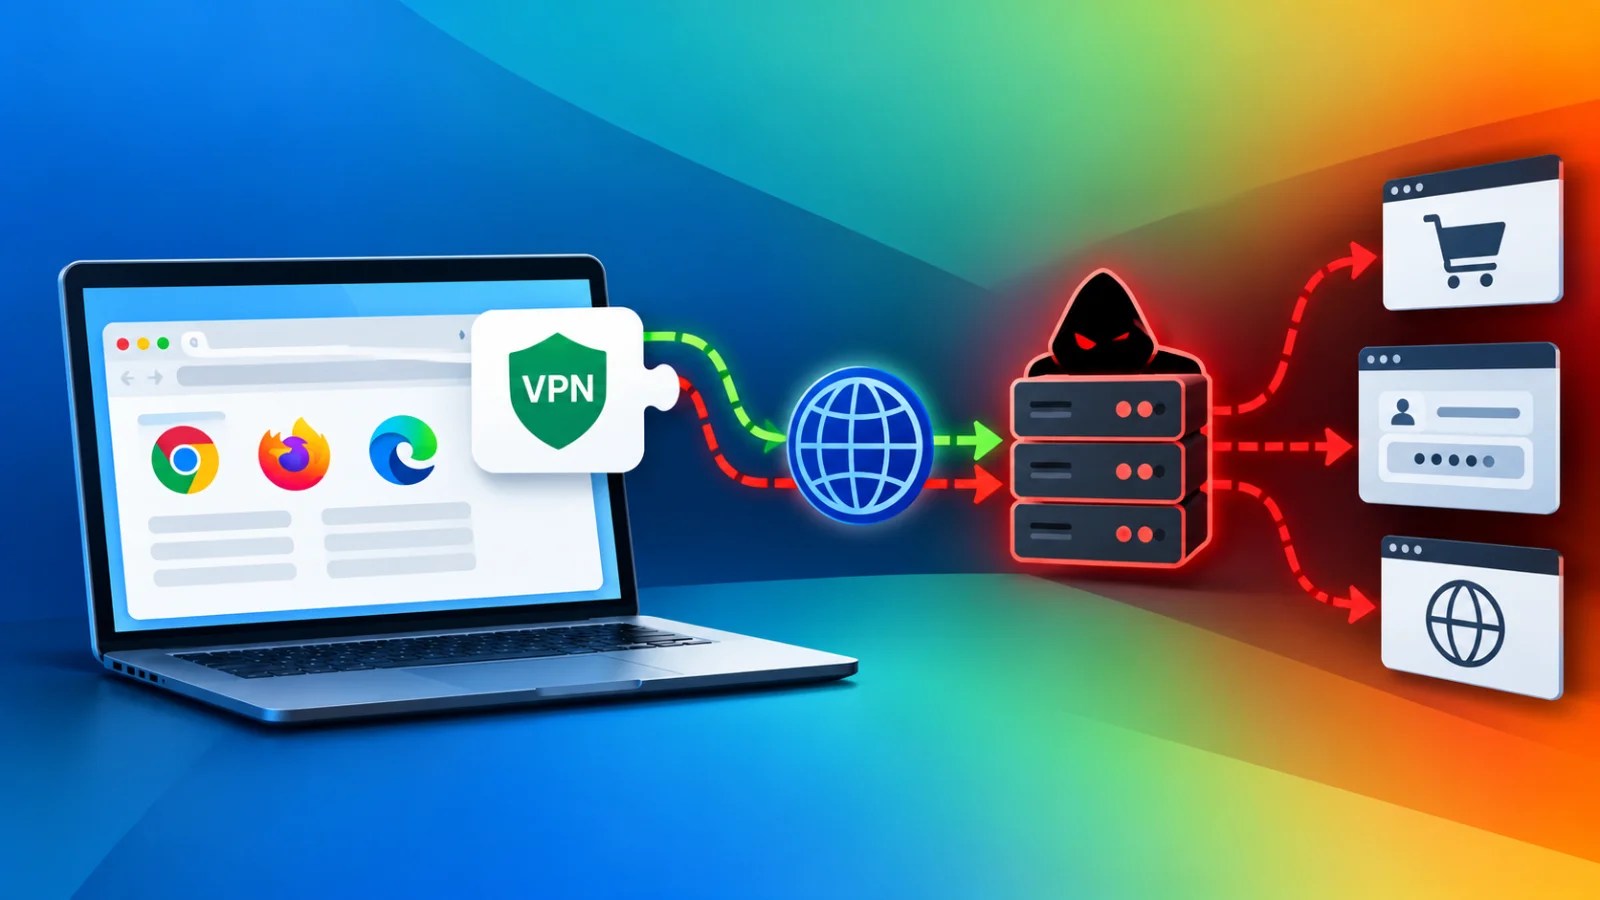
A large-scale operation involving 31 Chrome extensions, predominantly in Russian, has been discovered. These extensions masquerade as ‘VPN for X’ tools while secretly rerouting browser traffic through hidden proxy servers. The campaign, revealed by Risky Plugins on September 19, 2026, remains active and has amassed approximately 356,000 installations.
Widespread Installation and Targeted Platforms
These deceptive extensions aim to attract users looking for access to restricted services. They bear names associated with popular platforms such as RuTracker, YouTube, Telegram, and others, thus misleading users. Analysts have linked these extensions to three publisher accounts, uncovering a shared codebase across all 31. Remarkably, the RuTracker VPN alone has garnered around 200,000 installations.
The extensions exploit Chrome’s proxy API capabilities, requesting powerful permissions to modify browser proxy settings and intercept web requests. This enables them to direct user traffic through a Proxy Auto-Configuration (PAC) script that defines whether URLs connect directly or via a proxy. The proxy list is dynamically updated from external sources, bypassing the need for extension updates.
Technical Analysis and Potential Risks
Research conducted in early September highlighted that the extensions’ PAC scripts are downloaded from various online platforms, including GitHub Pages and Blogspot. Although the proxy server list is obscured using a simple Caesar shift over Base64, it does not provide substantial cryptographic security. The decoded data involves shared proxy credentials that renew monthly, and a VIP service priced at 299 roubles is available through specified APIs.
While most extensions proxy specific service-related traffic, the ‘Total VPN’ variant routes all browser traffic, heightening user exposure. This allows proxy operators to observe metadata and potentially manipulate unencrypted HTTP content. Although HTTPS encrypts content, routing traffic through untrusted proxies increases the risk of monitoring and manipulation.
Recommended Actions for Users and Enterprises
Risky Plugins have archived and analyzed the CRX packages for 28 of the extensions, publishing SHA-256 hashes for detection purposes. They identified fallback hostnames linked to known premium servers, treating these as potential leads for further investigation.
Users are advised to immediately uninstall any suspicious extensions, restart their browsers, and review proxy settings for anomalies. They should also update credentials for sensitive accounts used during the exposure period and monitor for unusual activity. Enterprises should block the identified extension IDs, investigate outbound connections to specific domains, and use archived hashes to safeguard managed endpoints.
The overarching caution is clear: any VPN extension that requests comprehensive URL access and updates routing instructions post-installation poses a significant trust risk. Users should remain vigilant and prioritize privacy and security practices.