Microsoft is about to launch a big safety enhancement for Outlook customers throughout a number of platforms. Beginning April 2025, the corporate will roll out a brand new two-click verification characteristic for encrypted emails, requiring customers to substantiate their intent to entry delicate content material explicitly.
This replace goals to scale back unintended publicity of confidential info, notably in public environments or throughout screen-sharing classes.
Microsoft has introduced a phased rollout schedule for this safety enhancement. For normal Outlook customers worldwide, the characteristic will start showing in early April 2025, with full deployment anticipated by late April.
Authorities Group Cloud (GCC) customers will see the characteristic starting in early Might 2025, with full implementation by the tip of that month. Cellular platform customers on each Android and iOS will obtain the replace beginning mid-June 2025, with completion anticipated by late June.
This safety measure is related to Microsoft 365 Roadmap ID 483883 and represents a big step ahead in Microsoft’s ongoing efforts to strengthen knowledge safety for its enterprise clients.
Microsoft Outlook’s New Two-Click on Function
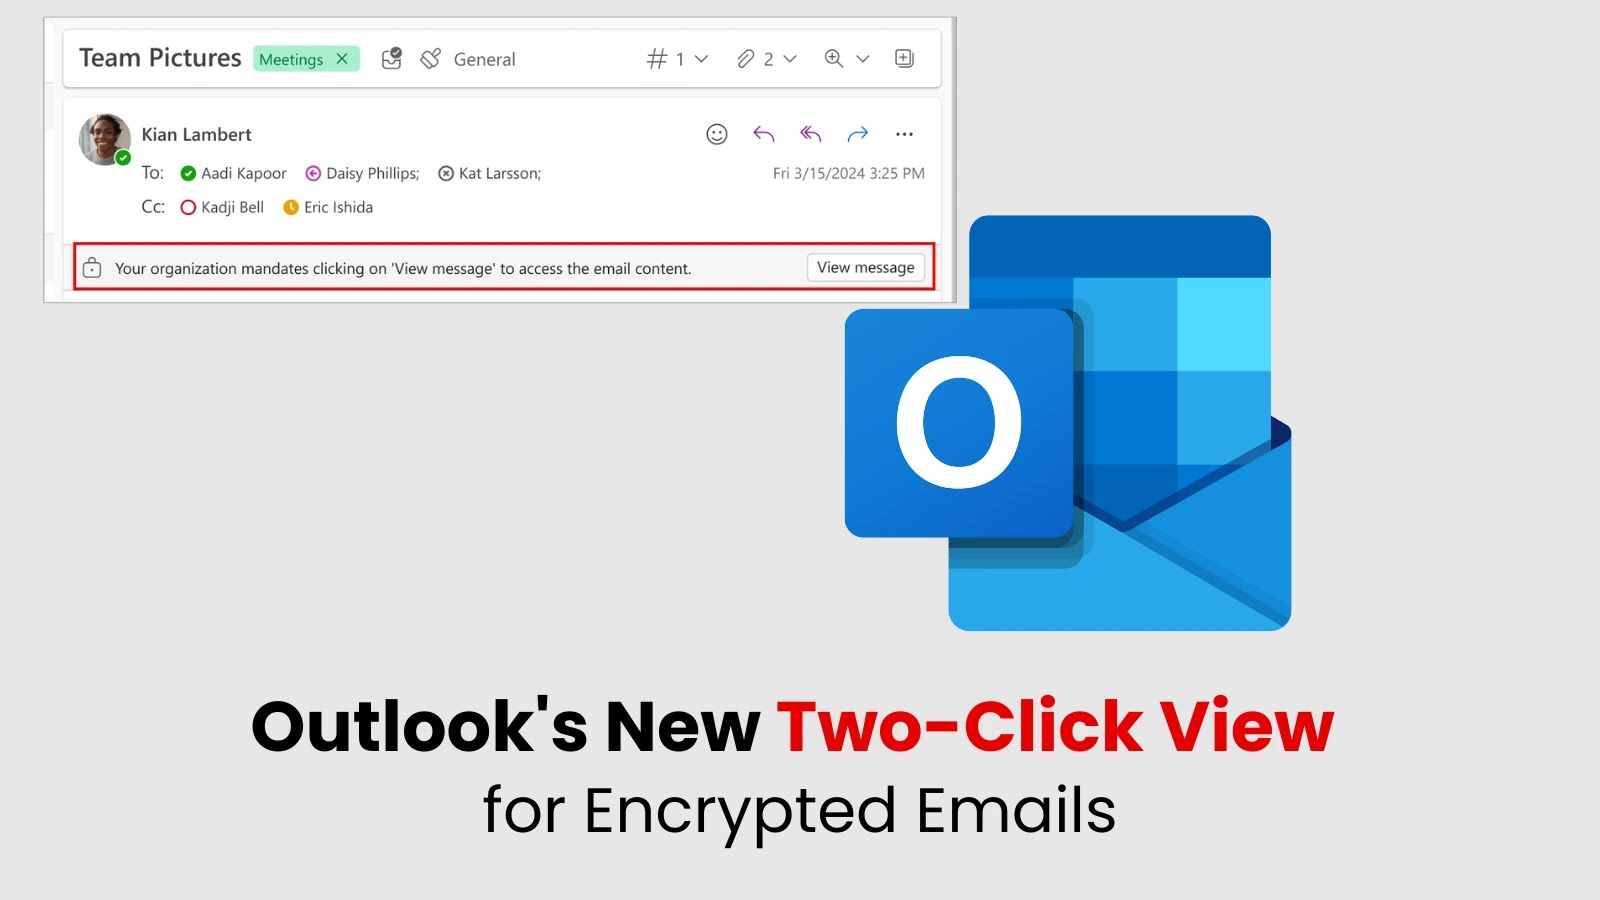
The brand new safety protocol introduces an extra verification step when accessing encrypted emails. When customers obtain an encrypted message, they are going to first see a notification stating, “Your group mandates clicking ‘View Message’ to entry the e-mail content material”. Solely after clicking this button will the encrypted content material be rendered and displayed.
This deliberate two-step course of ensures that delicate info isn’t robotically displayed, lowering the chance of confidential knowledge being inadvertently uncovered when units are utilized in public areas or throughout screen-sharing classes.
The characteristic works constantly throughout Outlook for Home windows desktop, Outlook internet interface, and Outlook cell functions for iOS and Android.
Microsoft has designed this characteristic with administrative flexibility in thoughts. By default, the two-click verification might be disabled, permitting organizations to make implementation choices based mostly on their particular safety necessities. IT directors can allow the characteristic via both the Microsoft Azure portal or PowerShell instructions.
The first good thing about this replace is enhanced safety consciousness amongst customers. By requiring deliberate motion to view encrypted content material, the characteristic creates a second of consciousness that will forestall unintended publicity of delicate info.
That is notably invaluable in organizations dealing with confidential knowledge, mental property, or private info topic to regulatory compliance.
From the person’s perspective, the expertise stays comparatively seamless whereas including a significant safety layer. The interface clearly communicates the requirement to view the message, using a distinguished button that maintains usability whereas enhancing safety protocols.
Microsoft’s introduction of the two-click view for encrypted emails demonstrates the corporate’s dedication to balancing safety enhancements with person expertise.
As organizations proceed to face evolving cybersecurity challenges, options that promote acutely aware safety choices with out considerably disrupting workflow symbolize a sensible strategy to knowledge safety.
Organizations serious about implementing this characteristic ought to put together their IT departments for the upcoming rollout, which is scheduled to start in April 2025.
Stay Credential Theft Assault Unmask & On the spot Protection – Free Webinar