Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Teams Restored After U.S. Service Disruption

Microsoft Teams Restored After U.S. Service Disruption

Posted on October 26, 2026 By CWS

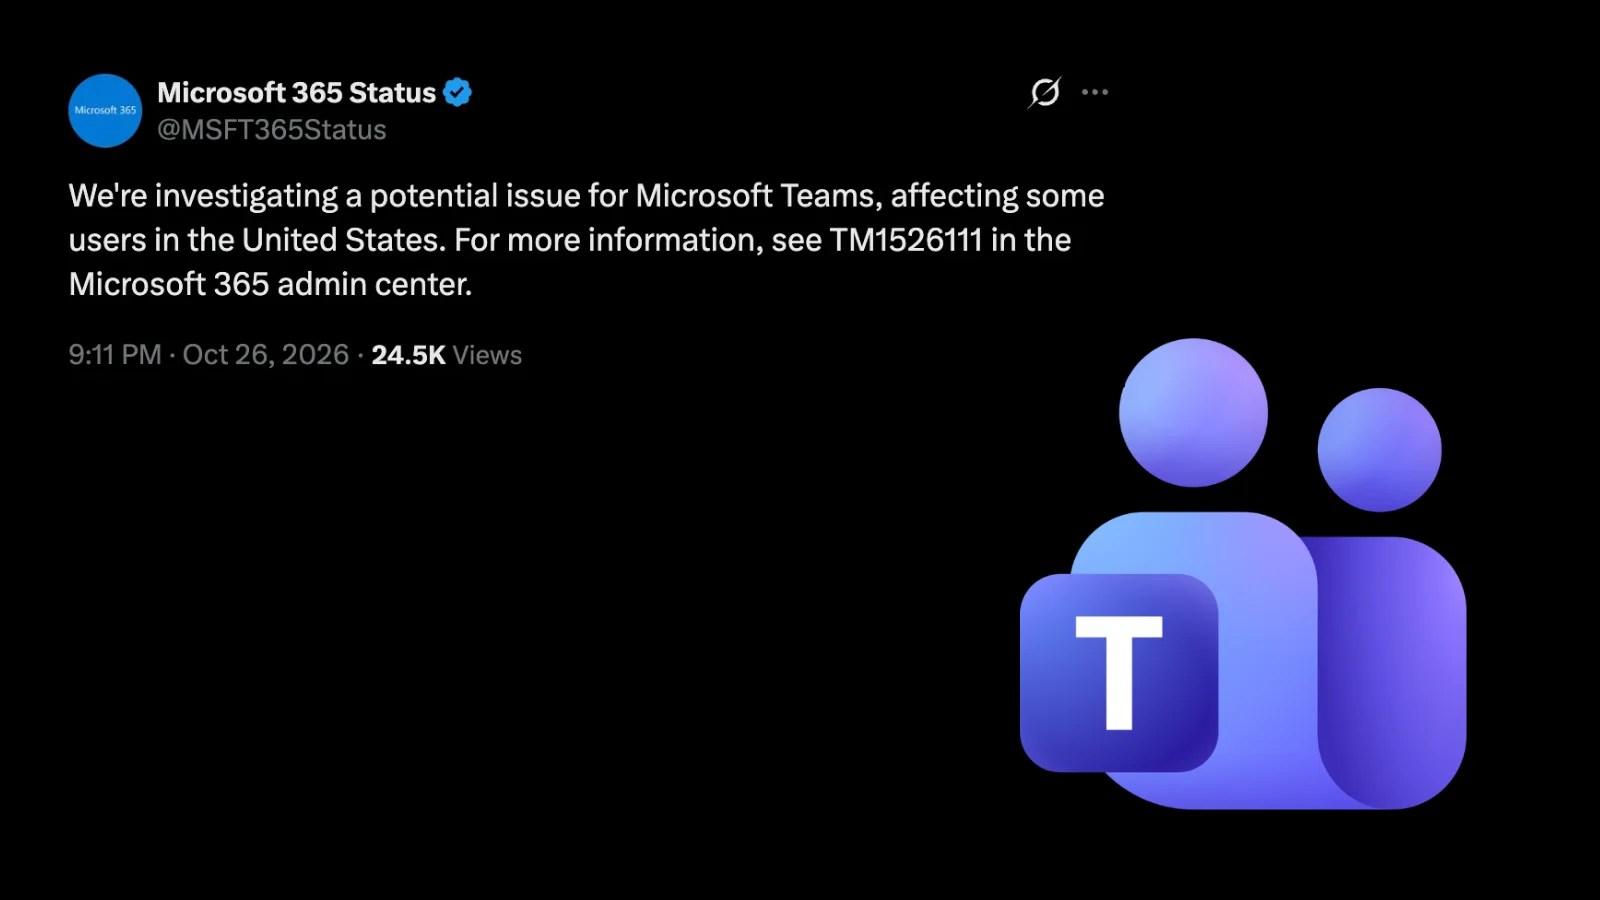
Microsoft recently addressed an issue that impacted Microsoft Teams users in the United States on October 26, 2026. The disruption, categorized as incident TM1526111, saw a swift resolution as the company implemented automatic scaling measures to restore service to optimal levels.

Initial Investigation of the Teams Disruption

Initially, Microsoft issued an advisory through its Microsoft 365 Status account, alerting administrators to a potential issue affecting some users. This notification directed IT professionals to the Microsoft 365 admin center for more comprehensive incident details. The issue was confined to the U.S., avoiding a global crisis.

As the investigation progressed, Microsoft reported that automated recovery processes were underway, with engineers actively monitoring the situation. The company has yet to disclose the exact number of users impacted or specify which Teams features were affected.

Recovery and System Performance

In an update, Microsoft confirmed that telemetry data verified successful automatic scaling, which increased processing throughput. This technical adjustment enhanced the system’s capacity to manage workloads, ensuring service health returned to normal. Nonetheless, the root cause of the disruption remains undisclosed.

Public statements from Microsoft have not suggested any cyberattack or data breach. The incidents did not specify whether users faced issues like failed calls, delayed messages, or meeting disruptions.

Context and Ongoing Monitoring

This incident follows previous Teams disruptions reported by Cybersecuritynews.com, including issues in September and August. While these events provide context for service availability challenges, they do not imply a common cause.

Administrators seeking detailed updates can access the Microsoft 365 admin center and check the service health dashboard for incident TM1526111. This tool offers active incident updates and resolution notices, essential for ongoing IT management.

For organizations evaluating the incident, the distinction between restored service and identified cause is crucial. While service has been restored, Microsoft has yet to explain the initial disruption trigger. The official incident record serves as the reference for further insights.

Cyber Security News Tags:automatic scaling, cloud services, incident TM1526111, IT management, Microsoft, Microsoft 365, Recovery, service disruption, service health, Teams, tech news, Telemetry, U.S

Post navigation

Previous Post: PHP Addresses Windows Security Flaw in Brotli Compression
Next Post: Hackers Target 953 Magento Stores with Stealthy JavaScript

Related Posts

ShinyHunters Takes Responsibility for EY Data Breach ShinyHunters Takes Responsibility for EY Data Breach Cyber Security News
SharePoint 0-Day RCE Vulnerability Actively Exploited in the Wild to Gain Full Server Access SharePoint 0-Day RCE Vulnerability Actively Exploited in the Wild to Gain Full Server Access Cyber Security News
Cyber Threats Concealed by Compromised IoT Devices Cyber Threats Concealed by Compromised IoT Devices Cyber Security News
OpenMatter Highlights Verification at Belgrade Blockchain OpenMatter Highlights Verification at Belgrade Blockchain Cyber Security News
Livewire Filemanager Vulnerability Exposes Web Applications to RCE Attacks Livewire Filemanager Vulnerability Exposes Web Applications to RCE Attacks Cyber Security News
KongTuke Attacking Windows Users With New Interlock RAT Variant Using FileFix Technique KongTuke Attacking Windows Users With New Interlock RAT Variant Using FileFix Technique Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI Coding Agents at Risk from Malicious Downloads
  • Hackers Target 953 Magento Stores with Stealthy JavaScript
  • Microsoft Teams Restored After U.S. Service Disruption
  • PHP Addresses Windows Security Flaw in Brotli Compression
  • Microsoft Urges Immediate .NET Security Update for Brotli Vulnerability

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI Coding Agents at Risk from Malicious Downloads
  • Hackers Target 953 Magento Stores with Stealthy JavaScript
  • Microsoft Teams Restored After U.S. Service Disruption
  • PHP Addresses Windows Security Flaw in Brotli Compression
  • Microsoft Urges Immediate .NET Security Update for Brotli Vulnerability

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark