Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
New Obex Tool Blocks EDR Dynamic Libraries From Loading at Runtime

New Obex Tool Blocks EDR Dynamic Libraries From Loading at Runtime

Posted on October 2, 2025October 2, 2025 By CWS

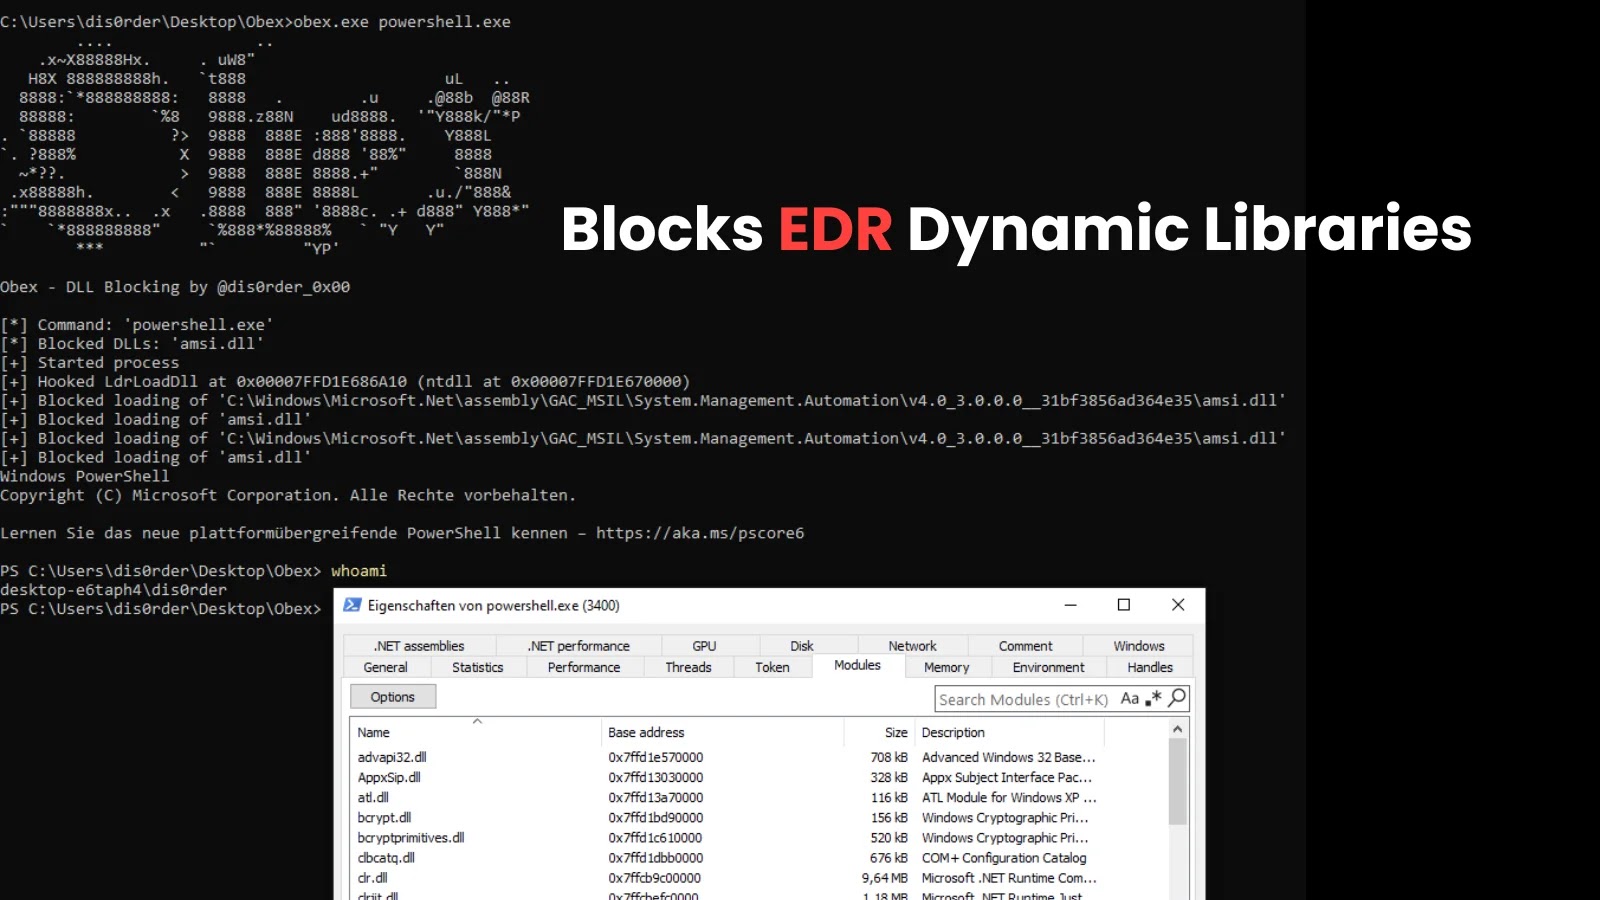
A brand new proof-of-concept (PoC) instrument named Obex has been launched, providing a way to stop Endpoint Detection and Response (EDR) and different monitoring options’ dynamic-link libraries (DLLs) from loading into processes.

The instrument, created by a researcher often known as “dis0rder0x00,” is designed to dam specified DLLs each throughout the preliminary startup of a course of and at runtime, doubtlessly permitting malware or pink staff instruments to function with out being detected by safety software program.

Obex features by launching a goal utility underneath its debug management. This enables it to intercept vital system operations. Particularly, it hooks the ntdll!LdrLoadDll operate, which is answerable for loading DLLs right into a course of.

When an utility makes an attempt to load a DLL, Obex intercepts the decision and checks the DLL’s title in opposition to a configurable blocklist.

If the DLL is on the record, the instrument simulates a failed load try, stopping the library from being injected into the method.

If the DLL is just not on the record, the loading course of is allowed to proceed as regular. This system successfully blinds safety instruments that depend on injecting their very own DLLs into processes to observe their habits.

The instrument is written in C and has no exterior dependencies, making it light-weight and moveable. By default, Obex is configured to dam amsi.dll, the library for the Antimalware Scan Interface, however customers can present a customized record of DLLs to dam.

The developer has made the instrument obtainable on GitHub, positioning it as a method for safety researchers to grasp and take a look at evasion strategies.

Safety options extensively use DLL injection to ascertain user-mode hooks for monitoring API calls and system habits. Instruments like Obex reveal strategies that can be utilized to bypass these defenses.

Whereas worthwhile for penetration testers and pink groups, such instruments additionally present defenders and safety distributors with necessary insights into evasion methods, serving to them to develop extra resilient detection and safety methods in opposition to refined threats.

Comply with us on Google Information, LinkedIn, and X for every day cybersecurity updates. Contact us to function your tales.
Cyber Security News Tags:Blocks, Dynamic, EDR, Libraries, Loading, Obex, Runtime, Tool

Post navigation

Previous Post: Many Attacks Aimed at EU Targeted OT, Says Cybersecurity Agency
Next Post: Confucius Hackers Hit Pakistan With New WooperStealer and Anondoor Malware

Related Posts

New Vulnerability Affects All Intel Processors From The Last 6 Years New Vulnerability Affects All Intel Processors From The Last 6 Years Cyber Security News
China-Linked Silver Dragon Uses Google Drive in Cyberattacks China-Linked Silver Dragon Uses Google Drive in Cyberattacks Cyber Security News
Critical Zero-Day Exploits Unveiled at Pwn2Own Day Two Critical Zero-Day Exploits Unveiled at Pwn2Own Day Two Cyber Security News
New Large-Scale Phishing Attacks Targets Hotelier Via Ads to Gain Access to Property Management Tools New Large-Scale Phishing Attacks Targets Hotelier Via Ads to Gain Access to Property Management Tools Cyber Security News
WordPress Sites Under Threat from Covert Steam Malware WordPress Sites Under Threat from Covert Steam Malware Cyber Security News
G_Wagon npm Package Attacking Users to Exfiltrates Browser Credentials using Obfuscated Payload G_Wagon npm Package Attacking Users to Exfiltrates Browser Credentials using Obfuscated Payload Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark