Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Node.js Updated HackerOne Program to Require a Signal of 1.0 or Higher to Submit Vulnerability Reports

Node.js Updated HackerOne Program to Require a Signal of 1.0 or Higher to Submit Vulnerability Reports

Posted on January 23, 2026January 23, 2026 By CWS

Node.js has up to date its HackerOne vulnerability disclosure program to require a minimal Sign rating of 1.0, aiming to cut back low-quality submissions and enhance processing effectivity.

Node.js has applied a brand new threshold for vulnerability report submissions by way of its HackerOne program, mandating that researchers keep a Sign rating of 1.0 or greater to take part.

Sign is HackerOne’s repute metric that displays the standard and validity of a researcher’s previous submissions, with greater scores indicating a historical past of authentic, impactful safety findings.

Strengthens HackerOne Submission Guidelines

The Node.js safety workforce famous a big enhance in low-quality vulnerability stories as the first driver for this coverage shift.

Between December fifteenth and January fifteenth alone, the undertaking obtained over 30 stories, a lot of which lacked technical advantage.

This enhance has strained the safety workforce’s assets, diverting consideration from authentic safety work and consuming time that may very well be higher spent on precise vulnerability remediation and safety initiatives.

The replace creates a two-tier entry mannequin for the safety analysis group. Established researchers and people with Sign scores of 1.0 or greater can proceed submitting vulnerabilities by way of HackerOne with out restrictions.

They’ll attain the Node.js safety workforce straight by way of the OpenJS Basis Slack channel to debate potential vulnerabilities.

This mechanism preserves alternatives for newer researchers whereas implementing quality control.

Understanding Sign Rating

Sign measures a researcher’s repute primarily based on submission high quality slightly than amount.

This metric helps platforms distinguish real safety researchers from these submitting invalid or irrelevant stories. This method displays broader challenges throughout the vulnerability disclosure ecosystem.

Many bug bounty platforms and open-source tasks have applied related quality-control mechanisms to handle report quantity and enhance processing effectivity.

Nonetheless, newcomers and researchers beneath the edge face limitations. Node.js has supplied an alternate pathway for researchers who don’t meet the Sign requirement.

The Node.js determination prioritizes the sustainability of their safety program over limitless submissions.

Researchers trying to keep entry to Node.js vulnerability reporting ought to concentrate on submission high quality and constructing their Sign rating by way of HackerOne’s ecosystem.

For these beneath the edge, leveraging the OpenJS Basis Slack supplies a direct communication channel with the safety workforce to determine credibility and perceive submission necessities.

The change underscores the continued rigidity between encouraging group participation in safety analysis and sustaining operational effectivity inside vulnerability disclosure packages.

Comply with us on Google Information, LinkedIn, and X for each day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:HackerOne, Higher, Node.js, Program, Reports, Require, Signal, Submit, Updated, Vulnerability

Post navigation

Previous Post: Microsoft to Add Brand Impersonation Protection Warning to Teams Calls
Next Post: New Phishing Kit As-a-service Attacking Google, Microsoft, and Okta Users

Related Posts

ToolShell Exploit Chain Attacking SharePoint Servers to Gain Complete Control ToolShell Exploit Chain Attacking SharePoint Servers to Gain Complete Control Cyber Security News
Understanding OWASP Top 10 – Mitigating Web Application Vulnerabilities Understanding OWASP Top 10 – Mitigating Web Application Vulnerabilities Cyber Security News
CISA Warns of Linux Kernel Use-After-Free Vulnerability Exploited in Attacks to Deploy Ransomware CISA Warns of Linux Kernel Use-After-Free Vulnerability Exploited in Attacks to Deploy Ransomware Cyber Security News
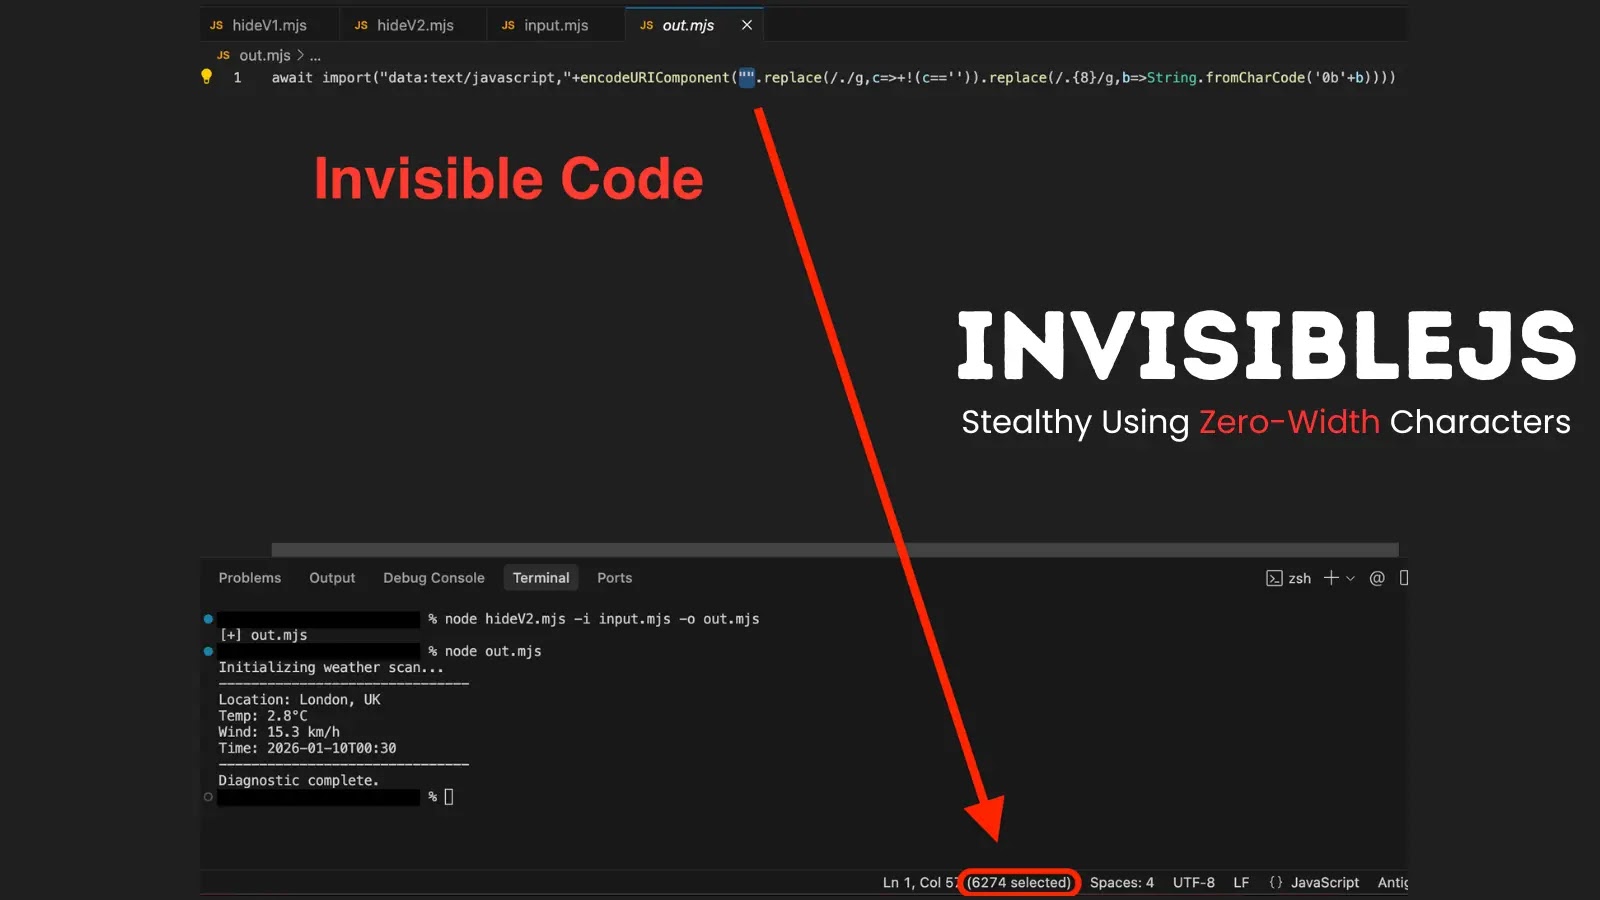
InvisibleJS Emerges as Stealthy JavaScript Obfuscator Using Zero-Width Characters InvisibleJS Emerges as Stealthy JavaScript Obfuscator Using Zero-Width Characters Cyber Security News
Critical Security Updates for Notepad++ to Block Exploits Critical Security Updates for Notepad++ to Block Exploits Cyber Security News
Critical ProFTPD Vulnerability Allows Remote Code Execution Critical ProFTPD Vulnerability Allows Remote Code Execution Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark