The Gentlemen ransomware group has recently added NVIDIA to its list of alleged victims on a dark web forum. The listing, posted on November 18, 2026, claims involvement in a breach of the chipmaker’s systems, yet lacks concrete evidence or confirmation from NVIDIA itself.
NVIDIA’s Alleged Breach: Analyzing the Claims
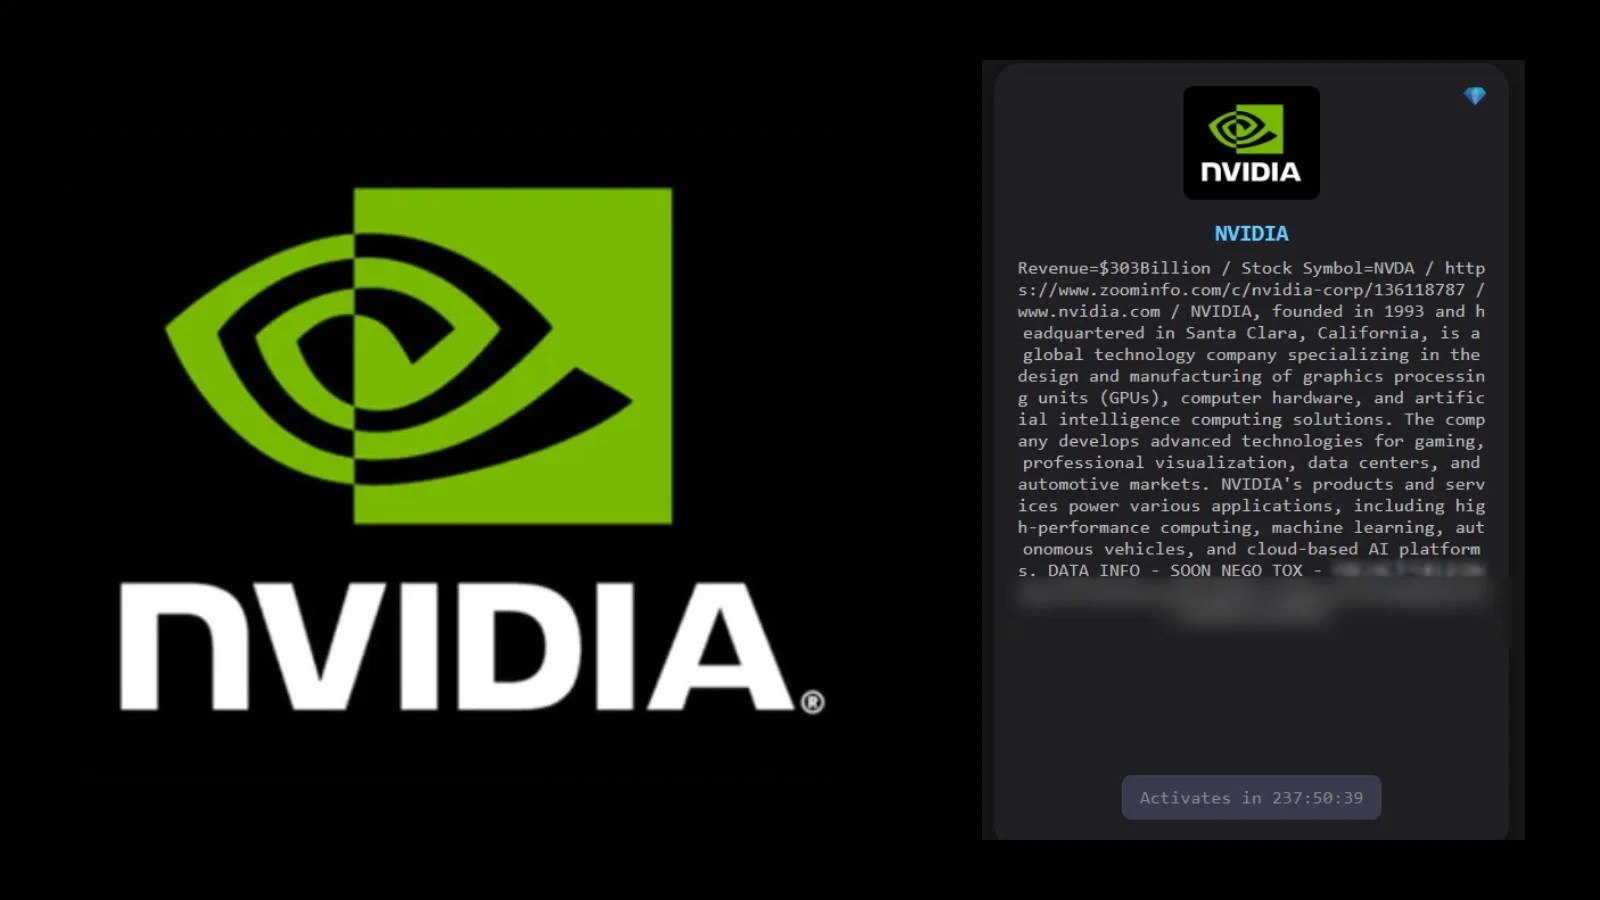
The post on the dark web includes a countdown timer, indicative of ongoing ransom negotiations, but fails to provide any sample files as proof. NVIDIA has not officially acknowledged any security breach, leaving the validity of the group’s claims in question. The posting features NVIDIA’s logo, a stock ticker symbol, and a revenue amount of $303 billion, though it does not specify the timeframe for this figure.
Additionally, the post references ‘DATA INFO – SOON’ and the use of Tox, a messaging service, but stops short of detailing the systems supposedly compromised or files allegedly obtained. The countdown, set to just under 10 days, does not clarify the consequences upon reaching zero.
Understanding The Gentlemen Ransomware Group
Emerging in 2025, The Gentlemen operates as a ransomware-as-a-service entity, allowing affiliates to perform attacks using their tools. This group is known for employing double extortion tactics, which involve both data theft and the threat of public exposure, alongside file encryption. However, such methods have not been confirmed in the context of NVIDIA.
Previous reports from Cyber Security News and a Sophos analysis have described past attacks by The Gentlemen, highlighting techniques such as disabling security measures and encrypting systems swiftly. Nonetheless, these accounts do not provide concrete parallels to the current NVIDIA claims.
Implications and Future Outlook
The breach listing has been recorded by ransomware tracker Breach House, yet its status remains pending, with no definitive proof of an actual system compromise. This incident coincides with recent leadership changes at NVIDIA, although no evidence suggests a connection between these events and the alleged breach.
Ultimately, without further evidence or a company statement, the situation remains speculative. A future release of validated data would be necessary to substantiate claims of data theft or system infiltration. For now, the countdown may merely represent the gang’s deadline rather than a confirmed breach.
In the broader context, organizations must remain vigilant against cyber threats like ransomware, continuously assessing and enhancing their security measures to protect sensitive data and operations.