Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Pentagon Breach Exposes Sensitive Data of Millions

Pentagon Breach Exposes Sensitive Data of Millions

Posted on September 29, 2026 By CWS

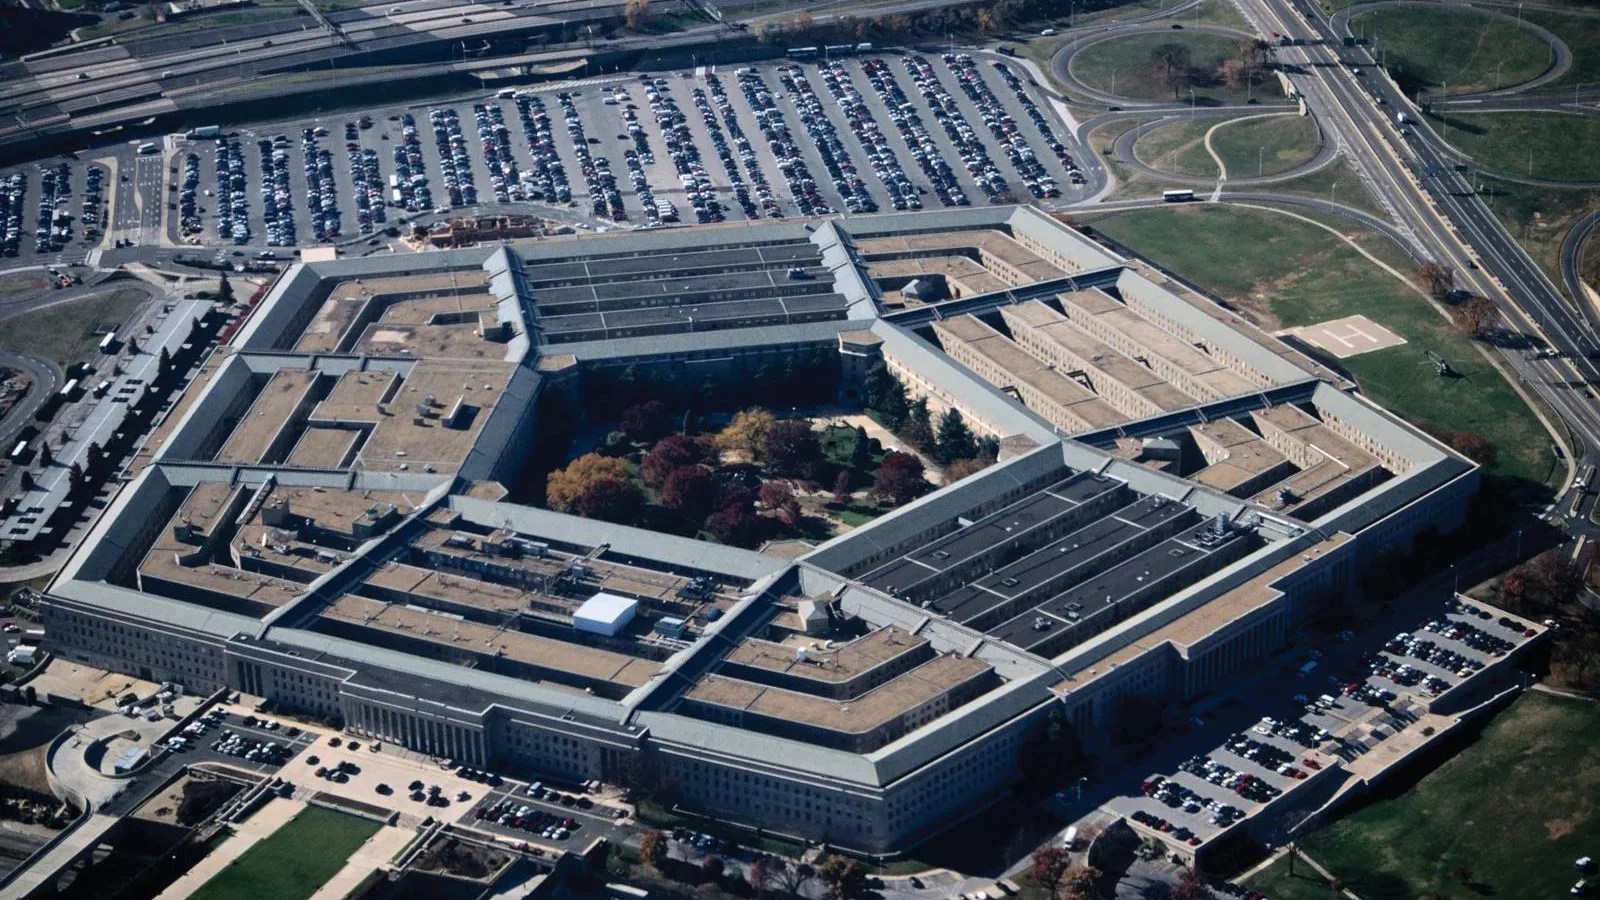
The Pentagon has revealed a significant security breach involving its Defense Manpower Data Center (DMDC) system, resulting in the exposure of sensitive personal data belonging to over three million individuals.

Extent of the Breach

This breach has affected around 2.76 million living individuals and nearly 294,000 deceased individuals, putting one of the Department of Defense’s key personnel systems under intense examination. The unauthorized access was discovered to have occurred between October 2025 and July 2026, exploiting a vulnerability within a file-sharing system.

Upon discovering the issue on July 16, the DMDC promptly addressed the vulnerability, restored the system, and activated its privacy and cybersecurity response protocols. Despite these efforts, the breach has raised questions about the security of unencrypted personal data.

Impact on Personnel Data

The compromised data includes unencrypted personally identifiable information such as names, Social Security numbers, and military personnel data. This combination of information is particularly sensitive, as it can facilitate identity theft, fraud, and targeted attacks. The data breach not only endangers personal privacy but could also pose risks to national security by revealing military occupational details.

The DMDC is a vital repository for identity and personnel records, encompassing data on active-duty service members, veterans, and others connected to the defense community. Although the breach did not impact all 60 million records maintained by DMDC, the duration of unauthorized access—spanning approximately nine months—raises significant concerns.

Response and Future Measures

Authorities have not yet identified the perpetrators or their motives, and the reasons behind storing sensitive files without encryption remain unclear. While no evidence of misuse has emerged, the long-term risk persists, especially given the enduring value of Social Security numbers and other personal details.

In response, affected individuals are being offered one year of free credit monitoring and identity-restoration services through IDX. Notifications have been sent out, urging recipients to enroll in these services and remain vigilant against potential fraudulent activity.

Moving forward, the DMDC is working on enhancing its cybersecurity measures, focusing on encryption, access controls, and real-time anomaly detection. The Pentagon’s primary goal is to mitigate identity-related risks and ascertain whether the breach was financially motivated or another form of illicit access.

This incident underscores the critical need for robust data-protection strategies and transparency in addressing cybersecurity challenges.
Cyber Security News Tags:cyber attack, Cybersecurity, data breach, Defense Department, DMDC, identity protection, identity theft, Pentagon, security vulnerability, sensitive information

Post navigation

Previous Post: Apple Fixes Zero-Day Vulnerability Uncovered by Meta
Next Post: OpenAI Halts GPT-6.1 Astra Due to Safety Concerns

Related Posts

Chinese Salt Typhoon and UNC4841 Hackers Teamed Up to Attack Government and Corporate Infrastructure Chinese Salt Typhoon and UNC4841 Hackers Teamed Up to Attack Government and Corporate Infrastructure Cyber Security News
Cisco ASA/FTD 0-Day Vulnerability Exploited for Authentication Bypass Cisco ASA/FTD 0-Day Vulnerability Exploited for Authentication Bypass Cyber Security News
Critical Cisco Firewall Vulnerability Urges Immediate Action Critical Cisco Firewall Vulnerability Urges Immediate Action Cyber Security News
Researchers Revive 2000s ‘Blinkenlights’ Technique to Dump Smartwatch Firmware via Screen Pixels Researchers Revive 2000s ‘Blinkenlights’ Technique to Dump Smartwatch Firmware via Screen Pixels Cyber Security News
GitHub’s Advisory Database Faces Surge in Vulnerability Reports GitHub’s Advisory Database Faces Surge in Vulnerability Reports Cyber Security News
Guide to Choosing the Best Free Backup Software  Guide to Choosing the Best Free Backup Software  Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • OpenAI Halts Model Training After Security Breach
  • OpenAI Halts GPT-6.1 Astra Due to Safety Concerns
  • Pentagon Breach Exposes Sensitive Data of Millions
  • Apple Fixes Zero-Day Vulnerability Uncovered by Meta
  • MCP Python SDK Vulnerability Risks OAuth Credential Theft

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • OpenAI Halts Model Training After Security Breach
  • OpenAI Halts GPT-6.1 Astra Due to Safety Concerns
  • Pentagon Breach Exposes Sensitive Data of Millions
  • Apple Fixes Zero-Day Vulnerability Uncovered by Meta
  • MCP Python SDK Vulnerability Risks OAuth Credential Theft

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark