Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
PHP Vulnerabilities Risk Data Exposure via JPEG Files

PHP Vulnerabilities Risk Data Exposure via JPEG Files

Posted on May 16, 2026 By CWS

Two significant vulnerabilities in PHP’s image processing capabilities have been identified, posing potential risks for data leaks and denial-of-service attacks. These security concerns, discovered by Positive Technologies researcher Nikita Sveshnikov, involve the widely used getimagesize and iptcembed functions, highlighting the importance of addressing these issues promptly.

Details of PHP Memory Safety Vulnerabilities

The initial vulnerability, cataloged as CVE-2025-14177 with a CVSS score of 6.3, is linked to information disclosure when the getimagesize function handles JPEG APP segments in multi-chunk mode. This flaw affects specific PHP versions, including 8.1.* before 8.1.34, 8.2.* before 8.2.30, 8.3.* before 8.3.29, 8.4.* before 8.4.16, and 8.5.* before 8.5.1.

The core issue arises from improper concatenation of data chunks during JPEG segment processing, leading to uninitialized memory allocation. This flaw can be exploited by attackers using JPEG files with large APP1 segments, potentially exposing sensitive information through the php://filter mechanism.

Heap Buffer Overflow and Its Consequences

The second vulnerability affects the iptcembed function, which integrates binary IPTC data into JPEG files. This issue is a classic heap buffer overflow, occurring due to insufficient buffer space allocation based on file size estimations. As a result, when handling non-standard file types, the function may write out of bounds, leading to potential heap corruption.

This flaw introduces a race condition, where files can increase in size between size checks and reads, allowing attackers to exploit this by manipulating data streams. Such vulnerabilities are critical for systems handling large volumes of user-uploaded images, such as content management systems and image CDNs.

Mitigation Measures and Recommendations

Developers have addressed the CVE-2025-14177 vulnerability by adjusting the php_read_stream_all_chunks function to ensure proper buffer management. A regression test accompanies this fix to prevent recurrence. Additionally, improvements to the iptcembed function now include bounds checking to avoid buffer overflows.

It is crucial for organizations to update their PHP installations to versions 8.1.34, 8.2.30, 8.3.29, 8.4.16, or 8.5.1 and above. Priority should be given to systems with public-facing upload endpoints to mitigate potential exploitation risks. Staying informed through reliable sources like Google News and LinkedIn ensures timely updates on such critical security matters.

Following these updates and recommendations will enhance security by addressing these vulnerabilities, reducing the risk of sensitive data exposure and service disruptions.
Cyber Security News Tags:CVE, CVE-2025-14177, data leak, denial of service, getimagesize, heap buffer overflow, heap memory exposure, image processing, IPTC data, iptcembed, JPEG vulnerabilities, memory safety, PHP security, PHP update, web security

Post navigation

Previous Post: Critical Linux Flaw Exposes SSH Keys and Passwords
Next Post: Critical NGINX Vulnerability PoC Code Released

Related Posts

PoC Exploit Released for Fortinet 0-Day Vulnerability that Allows Remote Code Execution PoC Exploit Released for Fortinet 0-Day Vulnerability that Allows Remote Code Execution Cyber Security News
Critical ServiceNow RCE Vulnerability Addressed Critical ServiceNow RCE Vulnerability Addressed Cyber Security News
EU Classifies ChatGPT as Major Search Engine Post User Surge EU Classifies ChatGPT as Major Search Engine Post User Surge Cyber Security News
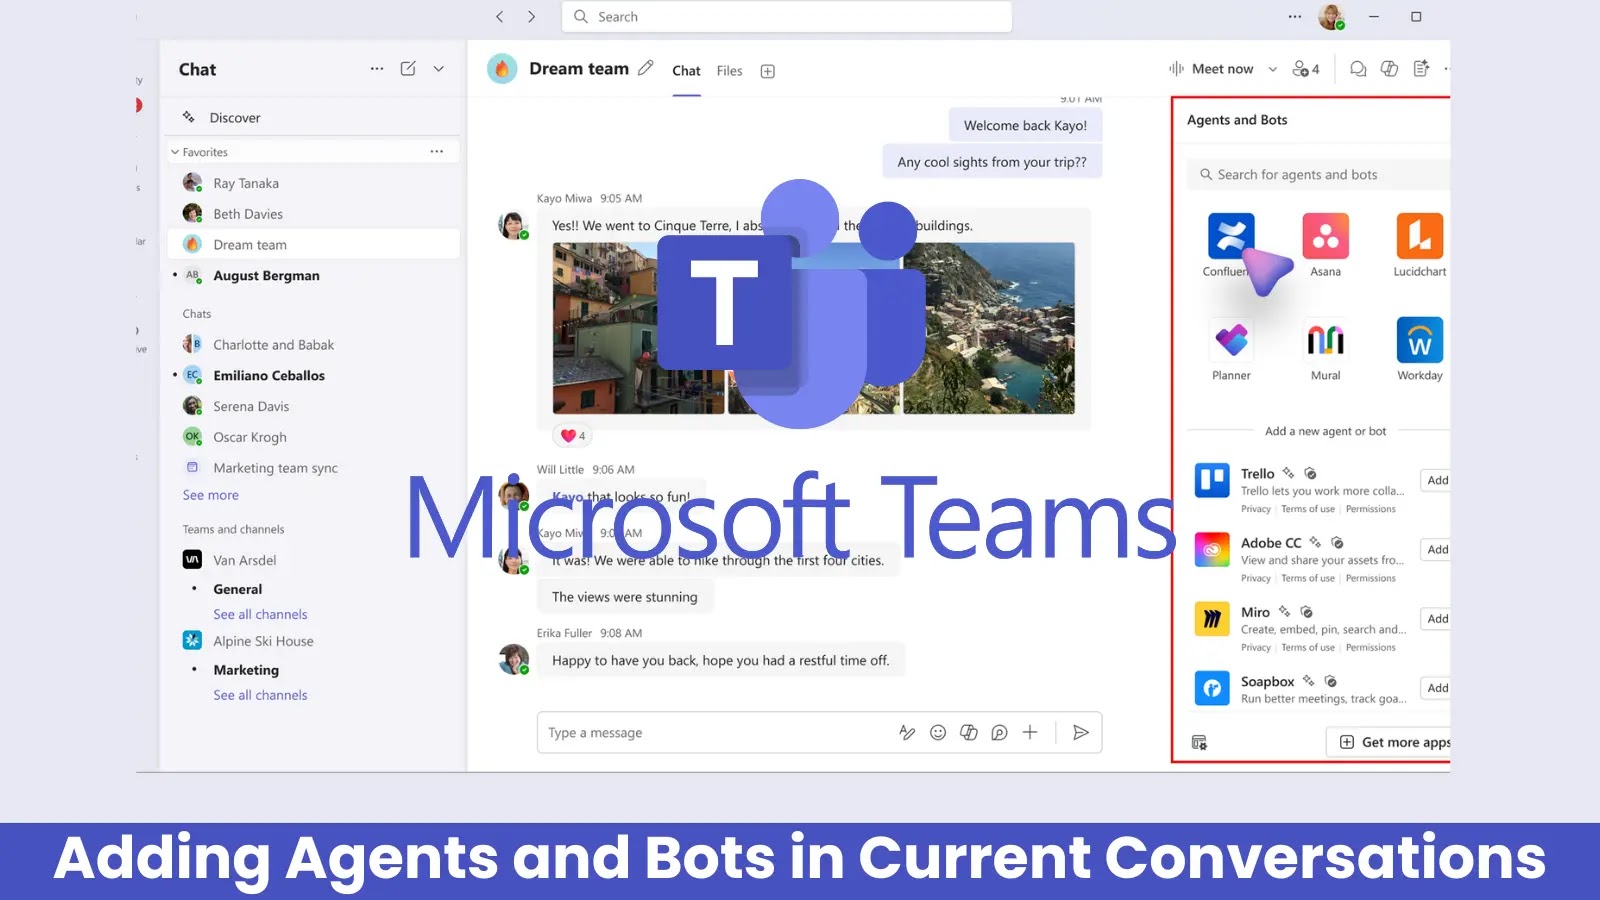
Microsoft Teams to Allow Users Adding Agents and Bots With Their Current Conversation Microsoft Teams to Allow Users Adding Agents and Bots With Their Current Conversation Cyber Security News
Critical Vulnerability in Cursor Exposes Windows Systems Critical Vulnerability in Cursor Exposes Windows Systems Cyber Security News
Threat Intelligence That Powers Best SOCs Worldwide Is Now Free   Threat Intelligence That Powers Best SOCs Worldwide Is Now Free   Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark