Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
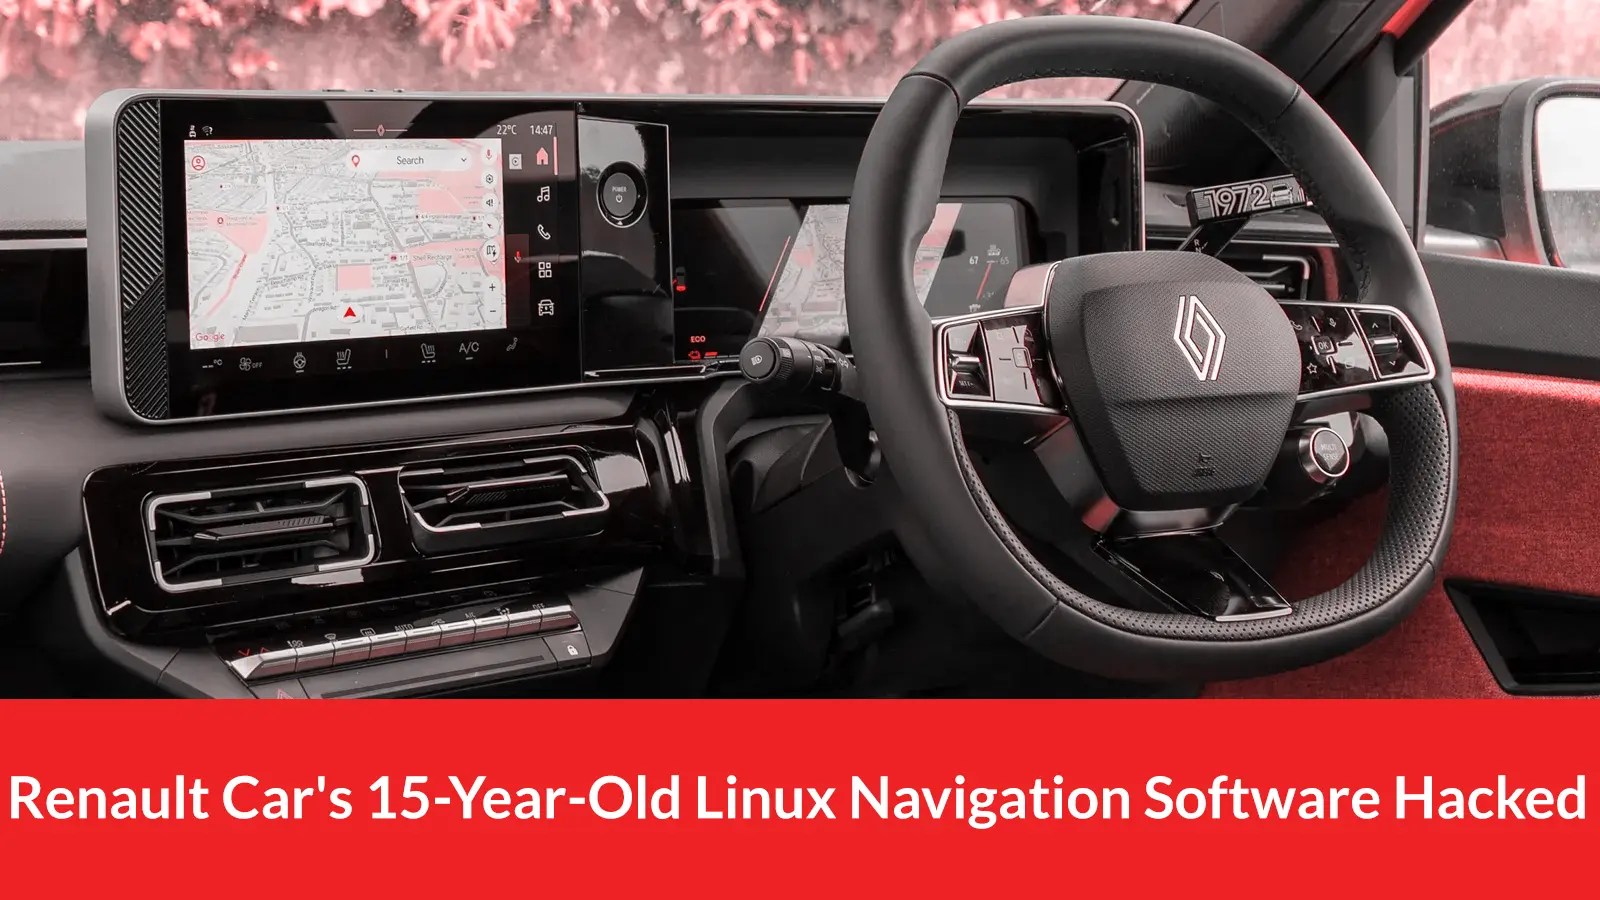
Renault’s Linux Navigation Hacked for Root Command Execution

Renault’s Linux Navigation Hacked for Root Command Execution

Posted on November 3, 2026 By CWS

A recent security breakthrough has revealed a method to execute root-level commands on the navigation system of a 2014 Renault Latitude. The compromised unit, a TomTom Carminat LIVE, operates on a custom-built Linux 2.6.28.10 system, highlighting vulnerabilities in outdated in-car software.

Discovering the Security Flaw

Security researcher Rasmus Moorats stumbled upon this flaw while attempting to adjust the clock post-daylight saving time in Estonia. The absence of a ‘Set time’ option and the inability to access the settings menu without an authentic map SD card led to further investigation. Analysts from NNS.ee identified the issue as stemming from how the unit processes a script file from the SD card.

The investigation revealed a series of minor vulnerabilities that, when combined, permitted full device control. This issue is not isolated, as similar risks have been documented in newer vehicles, such as the PerfektBlue Bluetooth vulnerabilities.

Mechanics of the Exploit

Despite being software from 2011, the system boasts significant security features, including read-only and ‘noexec’ partitions, alongside a DRM check for SD cards. However, Moorats employed an emulator to safely dissect the unit’s behavior, identifying a critical script file, master.script, which runs with root privileges.

The exploit was facilitated by two key commands: SHEX, which runs system programs without arguments, and LOG, which has a path traversal bug allowing unintended file access. By manipulating these commands, Moorats could exploit the system to execute root commands.

Implications and Future Risks

While the hack required physical access to the vehicle, the potential for misuse remains. A malicious actor could insert a prepped SD card, leveraging the system’s flaws. The broader issue lies in the design, where removable media is trusted, and scripts are executed with root access.

These vulnerabilities are not unique to older models. Recent discoveries in newer car systems, like the Nissan Leaf, show similar flaws. The persistence of these issues underscores the need for ongoing vigilance and updates in automotive software.

Protective Measures for Car Owners

Car owners are advised to avoid using unverified SD cards and USB devices in their vehicle’s head unit and to purchase map updates only from reputable sources. It’s also prudent to inquire with dealers about available security patches.

In conclusion, as vehicles continue to evolve technologically, so do the potential security risks. Ensuring robust security measures and regular updates is crucial for safeguarding against such vulnerabilities.
Cyber Security News Tags:car software, embedded systems, Emulation, Hacking, Linux, Navigation, Renault, root access, Security, Vulnerabilities

Post navigation

Previous Post: CrowdStrike’s $495M Acquisition of AI Security Firms
Next Post: cPGuard Update Breach Compromises Linux Servers

Related Posts

Google Project Zero Details ASLR Bypass on Apple Devices Using NSDictionary Serialization Google Project Zero Details ASLR Bypass on Apple Devices Using NSDictionary Serialization Cyber Security News
Malvertising Campaign Exploits ChatGPT for Malware Delivery Malvertising Campaign Exploits ChatGPT for Malware Delivery Cyber Security News
Weekly Cybersecurity News Recap – Top Vulnerabilities, Threat and Data Breaches Weekly Cybersecurity News Recap – Top Vulnerabilities, Threat and Data Breaches Cyber Security News
Hackers Attacking IIS Servers With New Web Shell Script to Gain Complete Remotely Control Hackers Attacking IIS Servers With New Web Shell Script to Gain Complete Remotely Control Cyber Security News
FBI Dismisses Contractor After Security Lapse FBI Dismisses Contractor After Security Lapse Cyber Security News
Hackers Target Developers with Fake Job Interviews Hackers Target Developers with Fake Job Interviews Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • UK Schools Targeted by AI-Driven 3AM Ransomware Attack
  • cPGuard Update Breach Compromises Linux Servers
  • Renault’s Linux Navigation Hacked for Root Command Execution
  • CrowdStrike’s $495M Acquisition of AI Security Firms
  • Google Alerts on Costly LLMjacking Attacks Impacting Enterprises

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • UK Schools Targeted by AI-Driven 3AM Ransomware Attack
  • cPGuard Update Breach Compromises Linux Servers
  • Renault’s Linux Navigation Hacked for Root Command Execution
  • CrowdStrike’s $495M Acquisition of AI Security Firms
  • Google Alerts on Costly LLMjacking Attacks Impacting Enterprises

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark