Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical SolarWinds Vulnerability Exposes 170 Installations

Critical SolarWinds Vulnerability Exposes 170 Installations

Posted on February 5, 2026 By CWS

Over 170 instances of SolarWinds Web Help Desk installations have been identified as vulnerable to a significant remote code execution (RCE) flaw. This vulnerability, actively exploited in the wild, has been added to the Known Exploited Vulnerabilities (KEV) catalog by the Cybersecurity and Infrastructure Security Agency (CISA).

Understanding the SolarWinds Vulnerability

The identified vulnerability, known as CVE-2025-40551, has a critical CVSS score of 9.8. It allows attackers to run arbitrary commands on affected systems without authentication by exploiting insecure data deserialization. The flaw is present in SolarWinds Web Help Desk versions prior to 2026.1 and affects the AjaxProxy functionality.

According to reports from the Shadowserver Foundation, these vulnerable installations have been discovered through their Vulnerable HTTP reports, highlighting the risk as these systems are publicly accessible and require no authentication for exploitation.

Research and Discovery

Research conducted by Horizon3.ai unveiled this vulnerability along with other security issues such as static credentials and bypasses of security protections. The primary concern with CVE-2025-40551 is its potential to compromise entire systems without user interaction, giving attackers control over the system’s confidentiality, integrity, and availability.

SolarWinds has since released version 2026.1 to mitigate this and related vulnerabilities, including CVE-2025-40552, CVE-2025-40553, and CVE-2025-40554, all carrying critical CVSS scores of 9.8.

Active Exploitation and Mitigation

CISA’s addition of CVE-2025-40551 to its KEV catalog on February 3, 2026, highlights ongoing exploitation activities. Federal agencies are mandated to address this vulnerability by February 6, 2026, under Binding Operational Directive 22-01. This urgency underscores the elevated threat beyond just federal systems, as attackers target these vulnerabilities to exploit IT management platforms.

BitSight has assigned a Dynamic Vulnerability Exploit (DVE) score of 9.19 to this flaw, indicating severe technical risk and a high probability of exploitation. The company’s analysis points out the continued focus of attackers on IT management systems due to their critical access and operational roles.

Organizations using affected versions are advised to implement the updates provided by SolarWinds immediately to mitigate these risks. The active exploitation and widespread use of SolarWinds Web Help Desk make it imperative for users to secure their systems promptly.

Stay informed on the latest cybersecurity developments by following us on Google News, LinkedIn, and X.
Cyber Security News Tags:AjaxProxy, BitSight, CISA, CVE, CVE-2025-40551, Cybersecurity, Deserialization, Horizon3.ai, IT security, RCE flaw, Shadowserver Foundation, SolarWinds, Vulnerabilities

Post navigation

Previous Post: SystemBC Botnet Survives Takedown, Infects 10,000 Devices
Next Post: AISURU Botnet Orchestrates Unprecedented 31.4 Tbps DDoS Attack

Related Posts

New ClickFake Interview Attack Using ClickFix Technique to Deliver GolangGhost Malware New ClickFake Interview Attack Using ClickFix Technique to Deliver GolangGhost Malware Cyber Security News
Google AI Incident Highlights Cybersecurity Challenges Google AI Incident Highlights Cybersecurity Challenges Cyber Security News
Microsoft 365 PDF Export LFI Vulnerability Allows Access to Sensitive Server Data Microsoft 365 PDF Export LFI Vulnerability Allows Access to Sensitive Server Data Cyber Security News
GnuTLS 3.8.13 Update: Key Security Vulnerabilities Fixed GnuTLS 3.8.13 Update: Key Security Vulnerabilities Fixed Cyber Security News
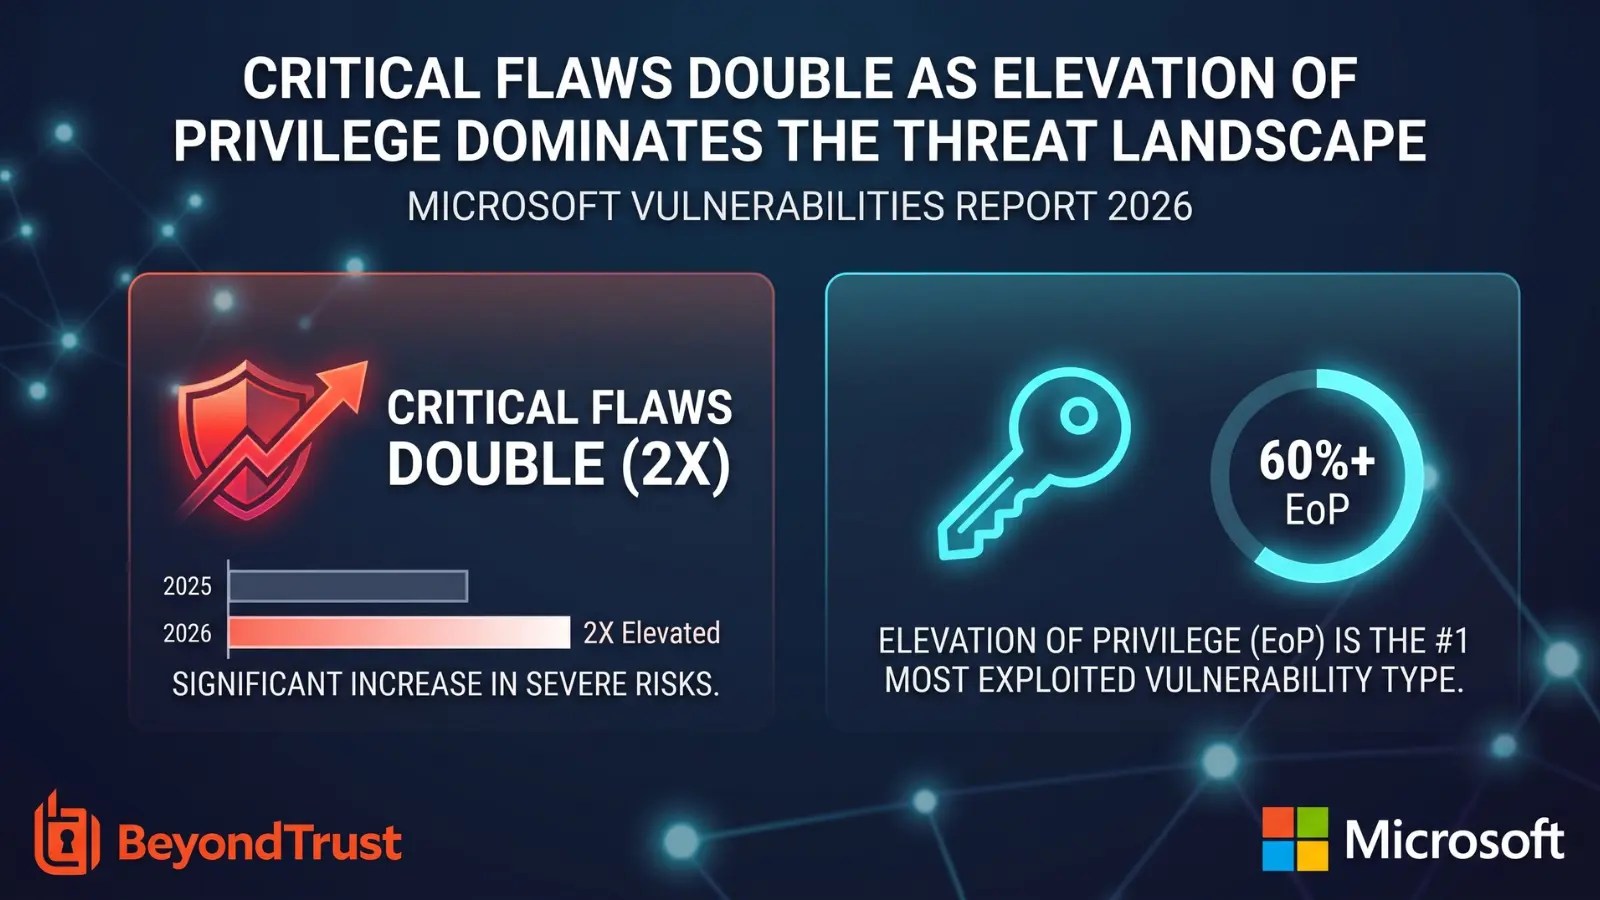
Microsoft Vulnerabilities 2026: Key Insights Revealed Microsoft Vulnerabilities 2026: Key Insights Revealed Cyber Security News
Thousands of Fortinet Firewalls Targeted in Global Cyber Attack Thousands of Fortinet Firewalls Targeted in Global Cyber Attack Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark