Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
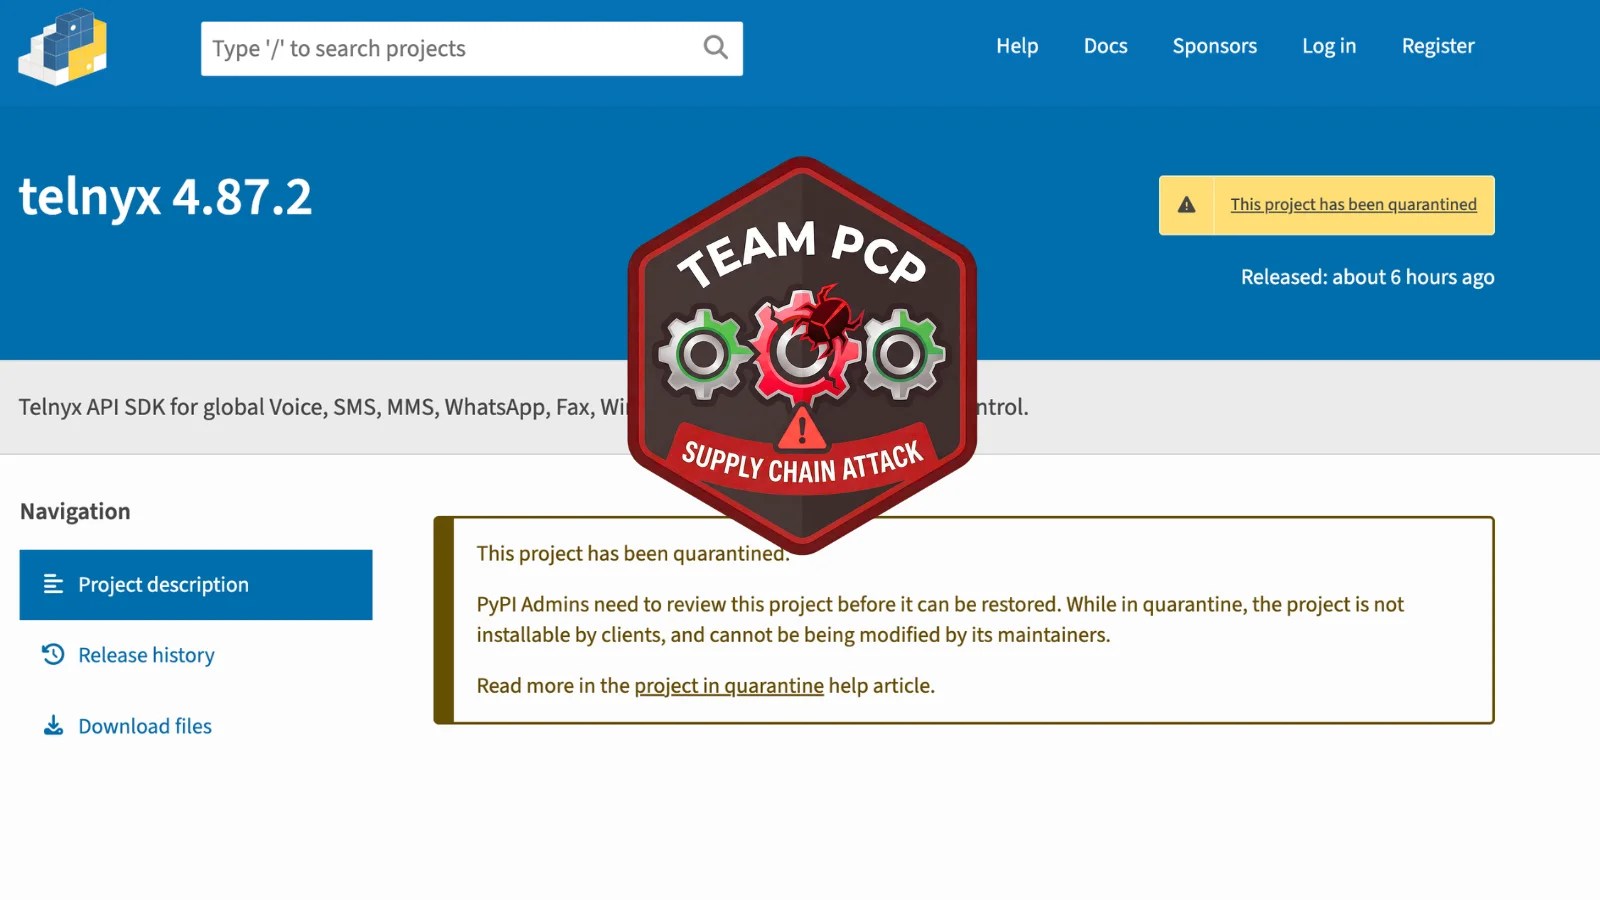
Telnyx Package Breach: TeamPCP’s Latest Supply Chain Attack

Telnyx Package Breach: TeamPCP’s Latest Supply Chain Attack

Posted on March 27, 2026 By CWS

The Telnyx Python package, a widely used software with over 742,000 downloads in the past month, has become the latest target in a series of sophisticated supply chain attacks conducted by a notorious threat actor group known as TeamPCP. The breach was identified on March 27, 2026, when malicious versions of the package were uploaded to the Python Package Index (PyPI).

TeamPCP’s Escalating Campaign

This recent compromise is part of a broader campaign by TeamPCP, a group that has been targeting trusted development tools since March 19, 2026. The group’s method involves infiltrating software supply chains to steal credentials, which are then used to compromise additional targets. Their attacks have affected numerous platforms, including Aqua Security’s Trivy and Checkmarx’s GitHub Actions.

On March 19, TeamPCP backdoored Trivy, assigning it a critical vulnerability score and exploiting it to access sensitive credentials. This breach led to further compromises across npm packages and GitHub repositories, showcasing the group’s ability to move quickly and efficiently within software ecosystems.

Malicious Payload and Execution

The malicious code in the Telnyx package executes at import time, affecting both Windows and Linux/macOS systems. On Windows, it downloads an audio file containing an obfuscated executable, which is designed to persist on the system and execute at startup. On Linux and macOS, a secondary script is embedded within the package, downloading additional payloads in a similar manner.

TeamPCP employs a unique technique involving WAV steganography to evade detection. The payloads are hidden within audio files, which pass standard security checks, making them difficult to identify using traditional filtering methods.

Mitigation and Future Outlook

Organizations using the affected Telnyx versions are urged to treat their systems as compromised. Immediate actions include downgrading to a secure version of the package, rotating all exposed credentials, and monitoring network traffic for suspicious activity. Additionally, it is crucial to audit CI/CD pipelines to prevent further exploitation.

This incident underscores the importance of stringent security measures in software development environments, especially as the FBI warns of potential follow-on intrusions. Organizations are advised to review their dependency management practices and enforce version pinning to mitigate risks.

For more updates on cybersecurity threats and mitigation strategies, follow us on Google News, LinkedIn, and X. Contact us if you wish to feature your cybersecurity stories.
Cyber Security News Tags:credential theft, Cybersecurity, data breach, Malware, PyPI, Python SDK, Software Security, supply chain attack, TeamPCP, Telnyx

Post navigation

Previous Post: TP-Link Addresses Critical Flaws in Archer Routers
Next Post: RSAC 2026: Key Highlights from Days 3-4

Related Posts

Exposed Open Directory Leaks BYOB Framework Across Windows, Linux, and macOS Exposed Open Directory Leaks BYOB Framework Across Windows, Linux, and macOS Cyber Security News
Ransomware Tactics Evolve Beyond Vulnerable Drivers Ransomware Tactics Evolve Beyond Vulnerable Drivers Cyber Security News
Princeton University Data Breach – Database with Donor Info Compromised Princeton University Data Breach – Database with Donor Info Compromised Cyber Security News
Researchers Proposed Game-Theoretic AI for Guiding Attack and Defense Researchers Proposed Game-Theoretic AI for Guiding Attack and Defense Cyber Security News
WhatsApp Enhances Security with Optional Account Password WhatsApp Enhances Security with Optional Account Password Cyber Security News
OpenMatter Network Unveils Secure AI Collaboration Platform OpenMatter Network Unveils Secure AI Collaboration Platform Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Innovative Method Challenges RSA Security Without Factoring
  • AI-Induced Hacks Challenge Legal Frameworks
  • SCOUTz Launches Beta for MSPs with New Intelligence Platform
  • AI Search Poisoning and Security Risks: Key Cyber News
  • Hackers Target Critical VPN Flaws in Check Point Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Innovative Method Challenges RSA Security Without Factoring
  • AI-Induced Hacks Challenge Legal Frameworks
  • SCOUTz Launches Beta for MSPs with New Intelligence Platform
  • AI Search Poisoning and Security Risks: Key Cyber News
  • Hackers Target Critical VPN Flaws in Check Point Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark