Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Trezor Alerts Users to Potential Spy Implant in Crypto Wallets

Trezor Alerts Users to Potential Spy Implant in Crypto Wallets

Posted on October 30, 2026 By CWS

Trezor has issued a warning concerning a potential hardware implant in the Trezor Safe 5, capable of intercepting recovery phrases and transmitting them via mobile networks. This advisory affects Trezor models purchased from CryptoBilis since March 2026, although only a single device has been flagged to date.

Security Alert and Recommendations

On October 30, Trezor advised users who might be affected to transfer their funds to a new wallet with a newly generated seed phrase. The company clarified that it has not physically examined the device nor received reports of any stolen funds from CryptoBilis customers.

The precautionary March 2026 date is meant to encourage user vigilance rather than confirm widespread tampering. The nature and function of the suspected implant are still under assessment in Trezor’s security lab.

Details of the Suspected Implant

This issue was brought to Trezor’s attention by a customer in Indonesia who made their purchase via the CryptoBilis store on Tokopedia in August 2026. After reviewing images and conducting an interview with the customer on October 28, Trezor arranged for the device to be analyzed at their security facility.

The suspicious device reportedly contains an additional circuit board situated between the primary board and the display. This board is equipped with a cellular module and antenna, which are allegedly used to capture and transmit information shown on the wallet’s screen, including recovery phrases, whenever the device is connected.

Trezor’s Ongoing Investigation

The revelation follows another investigation into Ledger wallets distributed by CryptoBilis, where some devices were confirmed to have been physically altered. Trezor removed CryptoBilis from its list of authorized resellers on October 9 and launched its own checks on customer devices.

While the reseller is common to both incidents, Trezor has not yet identified the perpetrators or confirmed any direct link to the Ledger tampering. Collaborative efforts are ongoing with Ledger and other involved parties, with assistance from SEAL 911 in managing customer support and incident reporting.

Steps for Trezor Users

Trezor advises users that simply transferring their existing wallet backup to a new device does not eliminate the risk. A newly generated seed is essential, and users should transfer their assets to this new wallet. Unused devices suspected of being affected should remain inactive, and no existing recovery phrase should be entered.

If a hardware wallet is unavailable, Trezor suggests considering a temporary software wallet or using a trusted exchange. It is crucial to verify the full receiving address before making any transfers. Users are urged to avoid home inspections or relying on device weight to detect tampering.

Eligible customers who purchased through CryptoBilis can reach out to Trezor Support for a direct replacement or a voucher for a new device. Users should be aware of scam attempts exploiting this situation through fake communications. Trezor Support will never request a recovery phrase.
Cyber Security News Tags:crypto news, crypto security, CryptoBilis, Cybersecurity, hardware wallet, Ledger, recovery phrases, spy implant, Trezor, wallet tampering

Post navigation

Previous Post: FBI Seizes Domain Linked to Cybercrime Hosting
Next Post: Chinese Hackers Use AI Tool ARTEX in Global Attacks

Related Posts

Multiple vtenext Vulnerabilities Let Attackers Bypass Authentication and Execute Remote Codes Multiple vtenext Vulnerabilities Let Attackers Bypass Authentication and Execute Remote Codes Cyber Security News
GravityRAT with Remote Access Capabilities Attacking Windows, Android, and macOS Systems GravityRAT with Remote Access Capabilities Attacking Windows, Android, and macOS Systems Cyber Security News
Halo Security Achieves SOC 2 Type 1 Compliance Halo Security Achieves SOC 2 Type 1 Compliance Cyber Security News
Node.js Updates Address Crucial TLS and DNS Vulnerabilities Node.js Updates Address Crucial TLS and DNS Vulnerabilities Cyber Security News
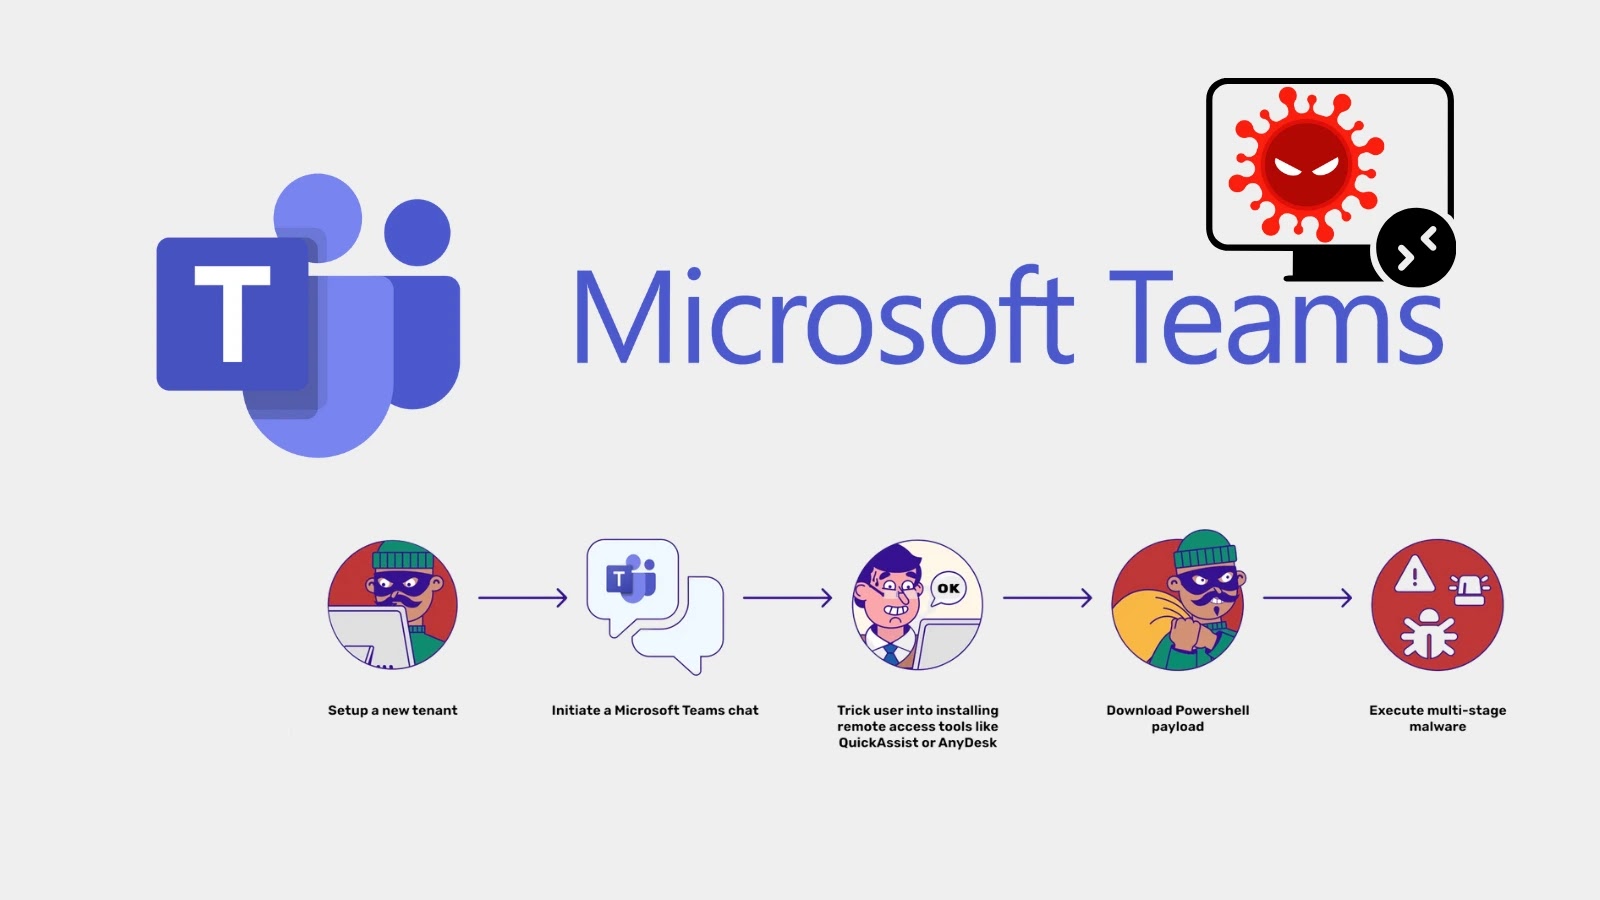
Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Cyber Security News
Cognizant Hit With Multiple US Class-Action Lawsuits Following TriZetto Data Breach Cognizant Hit With Multiple US Class-Action Lawsuits Following TriZetto Data Breach Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • North Korean Hackers Exploit Developer Access for Malware
  • Massive $6 Billion Binance Hack Linked to North Korean Group
  • Chinese Hackers Use AI Tool ARTEX in Global Attacks
  • Trezor Alerts Users to Potential Spy Implant in Crypto Wallets
  • FBI Seizes Domain Linked to Cybercrime Hosting

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • North Korean Hackers Exploit Developer Access for Malware
  • Massive $6 Billion Binance Hack Linked to North Korean Group
  • Chinese Hackers Use AI Tool ARTEX in Global Attacks
  • Trezor Alerts Users to Potential Spy Implant in Crypto Wallets
  • FBI Seizes Domain Linked to Cybercrime Hosting

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark