Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
U.S. Treasury Warns of Crypto ATMs Fueling Criminal Activity

U.S. Treasury Warns of Crypto ATMs Fueling Criminal Activity

Posted on August 6, 2025August 6, 2025 By CWS

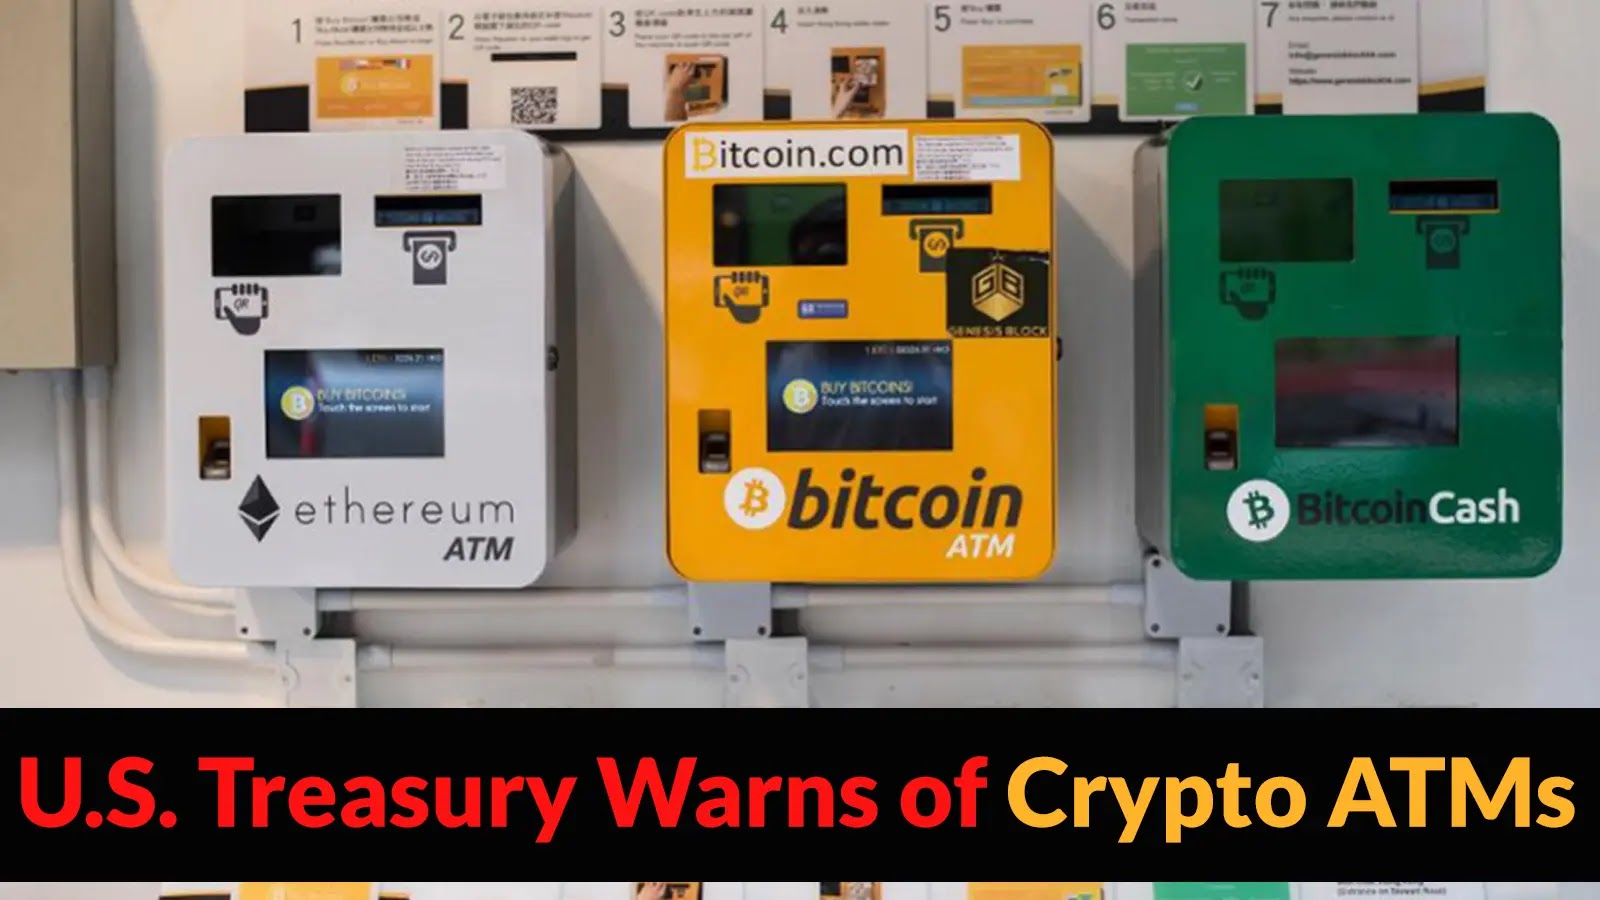
The U.S. Division of the Treasury’s Monetary Crimes Enforcement Community (FinCEN) has issued a important warning in regards to the exploitation of convertible digital forex (CVC) kiosks by felony organizations.

Launched on August 4, 2025, the advisory highlights how these cryptocurrency ATMs, whereas designed as handy entry factors for professional customers, have change into vital vectors for fraudulent actions and cash laundering operations.

FinCEN Director Andrea Gacki emphasised the escalating risk, stating that criminals have tailored to use revolutionary applied sciences like CVC kiosks for monetary theft.

The warning comes as federal businesses observe a regarding rise in rip-off funds processed by means of these automated terminals, notably focusing on weak populations together with older adults.

The illicit actions embody three of FinCEN’s Anti-Cash Laundering and Countering the Financing of Terrorism Nationwide Priorities: fraud, cybercrime, and drug trafficking group operations.

The regulatory discover particularly identifies tech help scams, buyer help fraud, and financial institution imposter schemes as prevalent assault vectors using CVC kiosks.

FinCEN analysts recognized that these scams disproportionately affect aged shoppers who could also be much less aware of cryptocurrency applied sciences, making them prime targets for stylish social engineering assaults.

The criminals exploit the relative anonymity and irreversible nature of cryptocurrency transactions to maximise their illicit features whereas minimizing detection dangers.

Regulatory Compliance and Detection Mechanisms

The Treasury’s warning emphasizes that the chance of illicit exercise is considerably amplified when CVC kiosk operators fail to fulfill their obligations below the Financial institution Secrecy Act (BSA).

Monetary establishments are urged to implement enhanced monitoring protocols and report suspicious actions involving these kiosks.

The discover supplies particular purple flag indicators that establishments ought to monitor, together with uncommon transaction patterns, frequent high-value purchases by the identical people, and transactions that seem inconsistent with buyer profiles.

FinCEN’s directive reinforces the important position of monetary establishments as companions in safeguarding the digital asset ecosystem whereas sustaining professional entry for shoppers and companies working inside regulatory compliance frameworks.

Equip your SOC with full entry to the newest risk information from ANY.RUN TI Lookup that may Enhance incident response -> Get 14-day Free Trial
Cyber Security News Tags:Activity, ATMs, Criminal, Crypto, Fueling, Treasury, U.S, Warns

Post navigation

Previous Post: Microsoft Zero Day Quest Hacking Contest
Next Post: CISA Warns of D-Link Vulnerabilities Actively Exploited in Attacks

Related Posts

Threat Actors Leverage ChatGPT to Attack Mac Devices With AMOS InfoStealer Threat Actors Leverage ChatGPT to Attack Mac Devices With AMOS InfoStealer Cyber Security News
Hackers Exploit ComfyUI 700+ AI Image Generation Servers to Deploy Malware Hackers Exploit ComfyUI 700+ AI Image Generation Servers to Deploy Malware Cyber Security News
Rhadamanthys Infostealer Leveraging ClickFix Technique to Steal Login Credentials Rhadamanthys Infostealer Leveraging ClickFix Technique to Steal Login Credentials Cyber Security News
Phishing Attacks Exploit RCS and iMessage to Evade Security Phishing Attacks Exploit RCS and iMessage to Evade Security Cyber Security News
Hackers Hijacked Apex Legends Game to Control the Inputs of Another Player Remotely Hackers Hijacked Apex Legends Game to Control the Inputs of Another Player Remotely Cyber Security News
Herodotus Android Banking Malware Takes Full Control Of Device Evading Antivirus Herodotus Android Banking Malware Takes Full Control Of Device Evading Antivirus Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles
  • Critical Vulnerability in Oracle PeopleSoft Exploited Globally
  • Kiteworks Recommends Nine-Hour System Shutdown Amid Cyber Threat
  • New Botnet x47.c Leverages AI for Advanced Cyber Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles
  • Critical Vulnerability in Oracle PeopleSoft Exploited Globally
  • Kiteworks Recommends Nine-Hour System Shutdown Amid Cyber Threat
  • New Botnet x47.c Leverages AI for Advanced Cyber Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark