Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
UAC-0099 Hackers Weaponizing HTA Files to Deliver MATCHBOIL Loader Malware

UAC-0099 Hackers Weaponizing HTA Files to Deliver MATCHBOIL Loader Malware

Posted on August 6, 2025August 6, 2025 By CWS

The Ukrainian menace intelligence group UAC-0099 has considerably advanced its cyber warfare capabilities, deploying a complicated new malware toolkit concentrating on Ukrainian state authorities, Protection Forces, and protection industrial enterprises.

The Nationwide Cyber Incident Response Group CERT-UA has documented a collection of coordinated assaults using HTA (HTML Utility) information as the first supply mechanism for the newly recognized MATCHBOIL loader malware.

These assaults start with rigorously crafted phishing emails, predominantly despatched from UKR.NET addresses, masquerading as official courtroom summons.

Instance of an electronic mail and a decoy file (Supply – CERT-UA)

The emails comprise hyperlinks to legit file-sharing companies, together with shortened URLs, which redirect victims to obtain double-archived information containing malicious HTA parts.

This social engineering method exploits the perceived legitimacy of authorized documentation to bypass preliminary person suspicion.

CERT-UA analysts recognized that the HTA information comprise closely obfuscated VBScript designed to determine a number of persistence mechanisms on compromised programs.

Upon execution, the malicious script creates a number of important information together with “documenttemp.txt” containing HEX-encoded information, “temporarydoc.txt” with PowerShell code, and establishes a scheduled process named “PdfOpenTask” for sustained system entry.

The menace actors have developed a multi-component malware ecosystem consisting of three main instruments: MATCHBOIL serves because the preliminary loader, MATCHWOK capabilities as a backdoor for distant command execution, and DRAGSTARE operates as a complete information stealer.

This trinity of malicious software program demonstrates the group’s development from earlier campaigns and suggests a shift towards extra persistent, multi-stage assault operations.

An infection Mechanism and Persistence Structure

The MATCHBOIL loader, developed in C#, implements a complicated multi-stage deployment course of that ensures persistent system compromise.

HTA file content material and decoded VBScript code (Supply – CERT-UA)

The preliminary HTA file execution triggers the creation of the scheduled process “PdfOpenTask” utilizing the command:-

schtasks.exe /create /tn PdfOpenTask /tr “powershell.exe -WindowStyle Hidden -executionpolicy bypass -noprofile -c Invoke-Expression (Get-Content material ‘%TMPpercenttemporarydoc.txt’ -Uncooked)” /sc as soon as /st 12:02 /f

This process converts HEX-encoded information into executable bytes, writes them to “%PUBLICpercentDownloadsAnimalUpdate.txt”, then strikes the file to “AnimalUpdate.exe” whereas establishing one other scheduled process “AnimalSoftUpdateAnimalSoftware” for execution.

The loader subsequently gathers system fingerprinting information together with CPU {hardware} identifiers, BIOS serial numbers, and MAC addresses, transmitting this info through HTTP headers to command-and-control servers hosted on domains like egyptanimals[.]com and geostat[.]lat.

Equip your SOC with full entry to the most recent menace information from ANY.RUN TI Lookup that may Enhance incident response -> Get 14-day Free Trial
Cyber Security News Tags:Deliver, Files, Hackers, HTA, Loader, Malware, MATCHBOIL, UAC0099, Weaponizing

Post navigation

Previous Post: Google’s Salesforce Instances Hacked in Ongoing Attack
Next Post: Trend Micro Patches Apex One Vulnerabilities Exploited in Wild

Related Posts

iOS 27.0.1 Jailbreak Achieved on iPhone 18 Pro iOS 27.0.1 Jailbreak Achieved on iPhone 18 Pro Cyber Security News
AI Tools Misused for Stealthy Malware Communication AI Tools Misused for Stealthy Malware Communication Cyber Security News
Malicious Bing Ads deploy Weaponized PuTTY to Exploit Kerberos and Attack Active Directory services Malicious Bing Ads deploy Weaponized PuTTY to Exploit Kerberos and Attack Active Directory services Cyber Security News
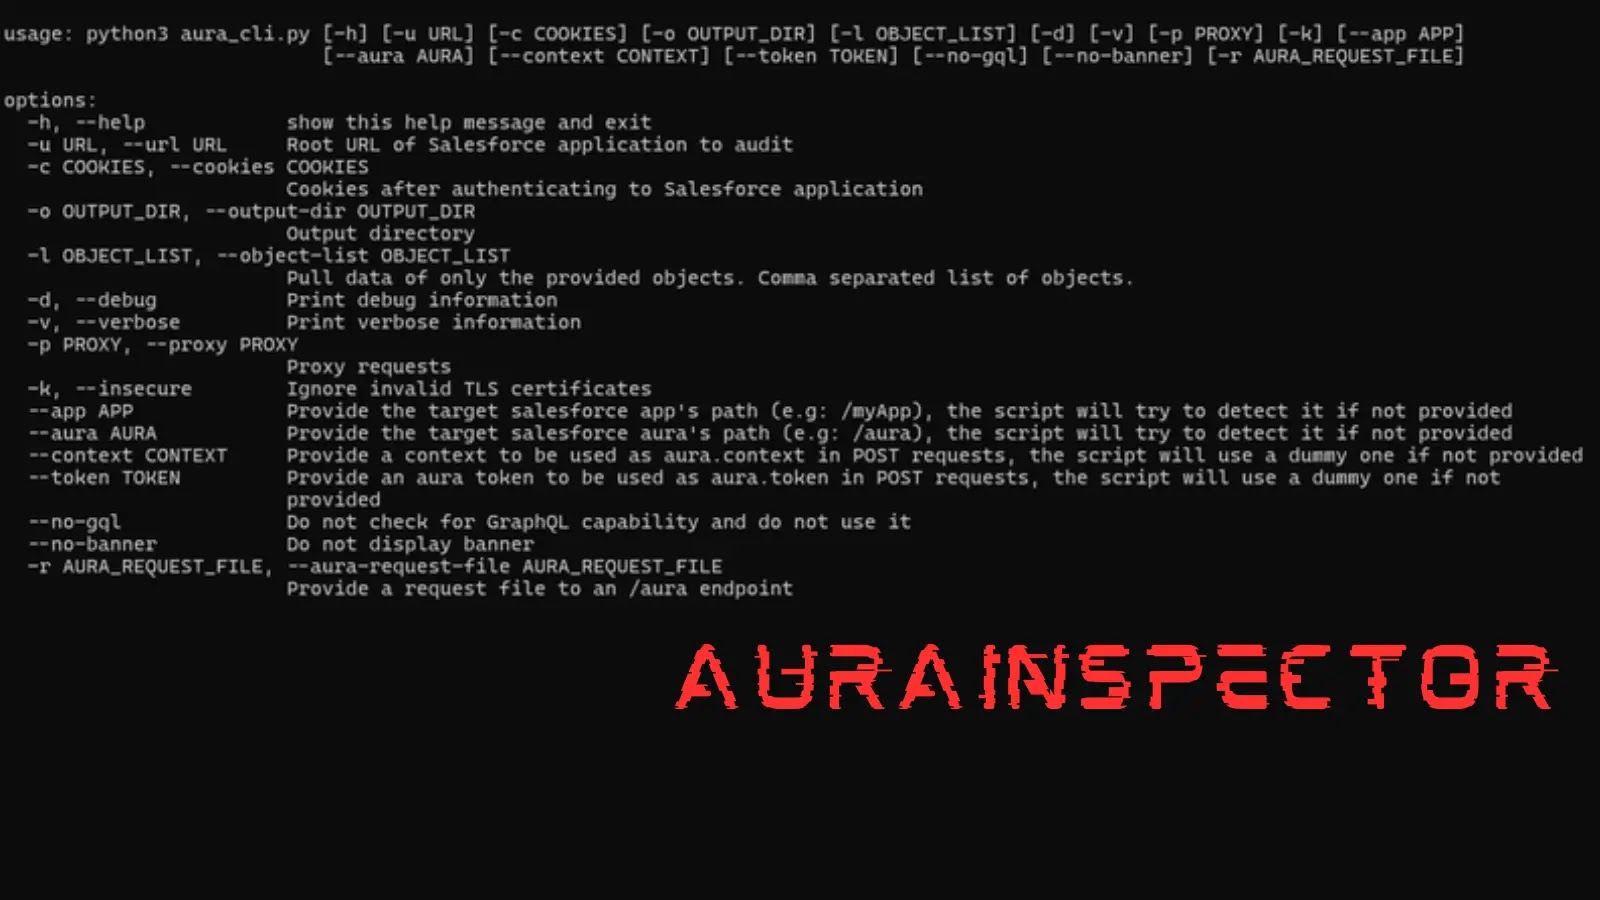
Open-Source Tool for Salesforce Aura Framework Misconfiguration Analysis Open-Source Tool for Salesforce Aura Framework Misconfiguration Analysis Cyber Security News
MacSync macOS Infostealer Leverage ClickFix-style Attack to Trick Users Pasting a Single Terminal Command MacSync macOS Infostealer Leverage ClickFix-style Attack to Trick Users Pasting a Single Terminal Command Cyber Security News
Enhancing macOS Security: Closing Gaps by 2026 Enhancing macOS Security: Closing Gaps by 2026 Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Grok AI App Builder Data Breach Risks Thousands of Apps
  • Critical Vulnerabilities Patched by Citrix and Ivanti
  • Hackers Target Qlik Sense Servers with Exploits
  • N-able Issues Urgent Hotfix Following Security Vulnerabilities
  • Asus and Zoom Issue Critical Security Updates

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Grok AI App Builder Data Breach Risks Thousands of Apps
  • Critical Vulnerabilities Patched by Citrix and Ivanti
  • Hackers Target Qlik Sense Servers with Exploits
  • N-able Issues Urgent Hotfix Following Security Vulnerabilities
  • Asus and Zoom Issue Critical Security Updates

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark