Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Understanding DCSync Attacks on Active Directory

Understanding DCSync Attacks on Active Directory

Posted on July 28, 2026 By CWS

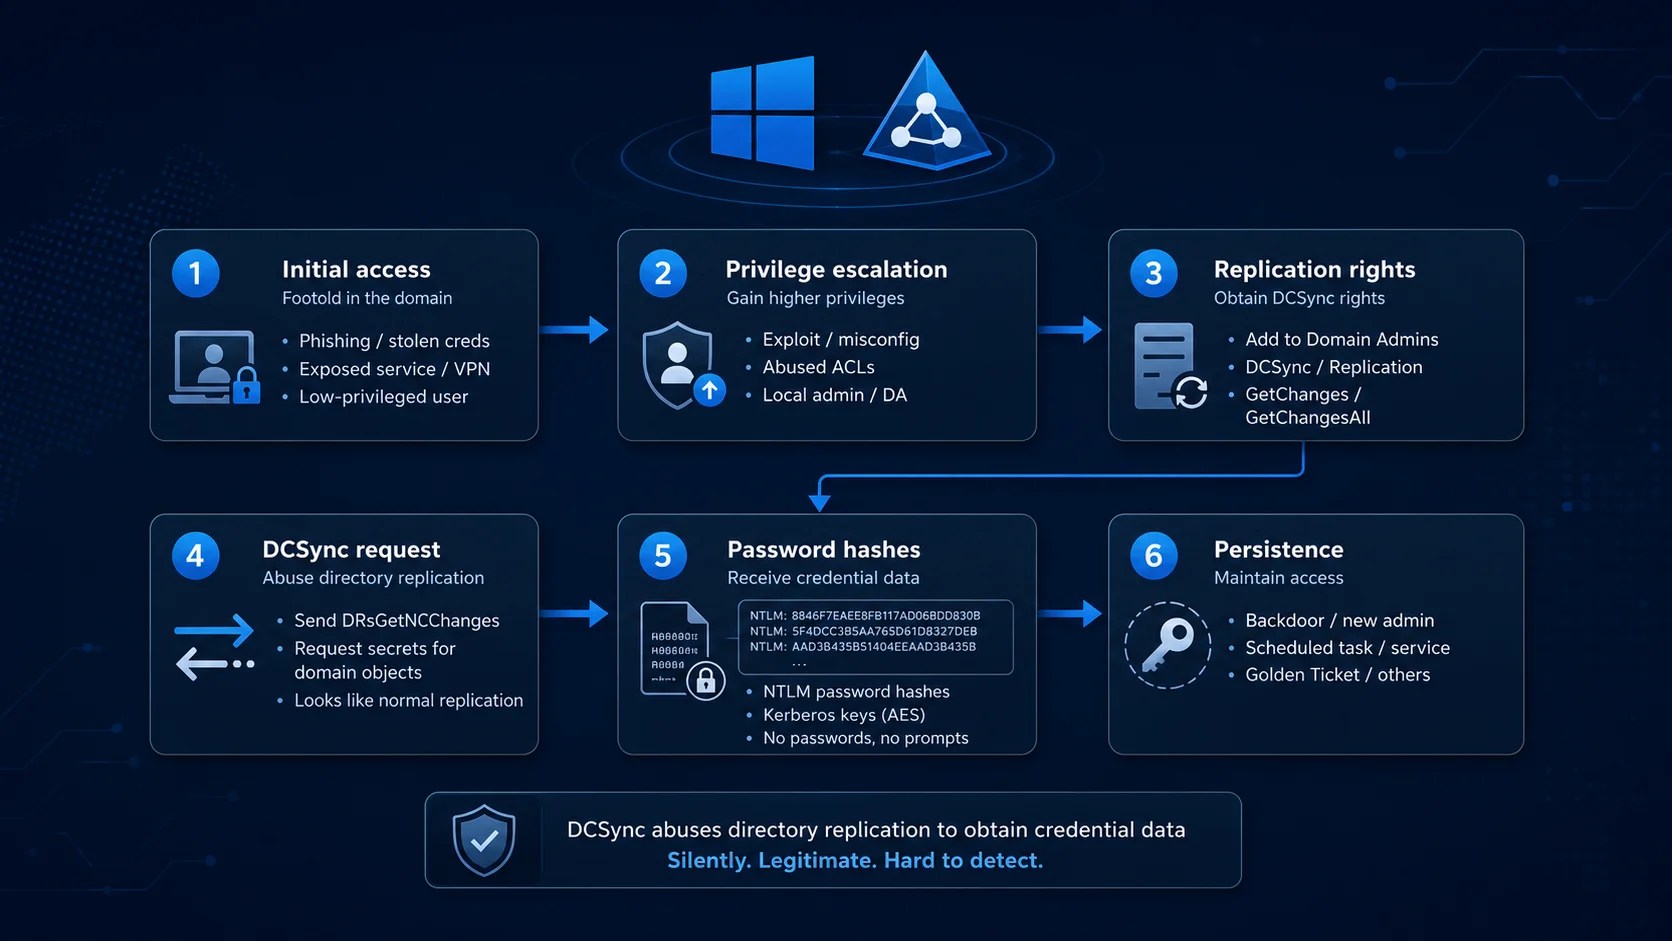
Active Directory is a critical component in managing identities within organizations, holding the valuable password hashes of users, services, and machines. A DCSync attack enables attackers to extract these hashes without accessing domain controllers directly. Instead, they exploit the replication protocol designed for domain synchronization, posing as a domain controller.

How DCSync Exploits Active Directory

In a DCSync attack, the adversary impersonates a domain controller to request sensitive information via the Microsoft Directory Replication Service Remote Protocol (MS-DRSR). The attacker connects to the DRSUAPI RPC interface and requests credential attributes through IDL_DRSGetNCChanges. The targeted domain controller, mistaking the request for legitimate peer replication, provides NTLM hashes, Kerberos keys, and password histories.

This technique was first implemented in Mimikatz, making it a standard method in malicious playbooks. DCSync attacks are cataloged under MITRE ATT&CK as T1003.006, emphasizing their significance in credential dumping strategies.

The Covert Nature of DCSync Attacks

Unlike other credential-theft methods, DCSync does not leave behind typical footprints. Traditional attacks like LSASS dumping or NTDS.dit theft trigger alarms by interacting with disk files, but DCSync’s covert nature allows it to mimic legitimate directory synchronization traffic. As a result, detection relies heavily on directory-service auditing and network monitoring.

The attack’s severity lies in its capability to extract the krbtgt account hash, allowing attackers to forge Golden Tickets. These self-minted Kerberos tickets grant unrestricted domain access, leading to widespread compromise without triggering traditional security alerts.

Prerequisites and Execution of DCSync

To execute a DCSync attack, an attacker must first acquire an identity with replication rights. This is typically achieved by compromising high-privilege accounts or exploiting misconfigured access control lists (ACLs). Once in control, the attacker can initiate DCSync using tools like Mimikatz or Impacket’s secretsdump.py.

Defenders must proactively audit replication rights and manage ACLs to prevent unauthorized replication access. Monitoring Event ID 4662, particularly when associated with non-domain controller accounts, is crucial for early detection of potential DCSync attempts.

Mitigation and Defense Strategies

Organizations need to restrict replication rights to essential accounts and continuously monitor directory service activities. Enforcing a tiered administrative model and deploying identity threat detection solutions can further bolster defenses against DCSync attacks.

In the event of a compromise, immediate rotation of the krbtgt account and other privileged credentials is necessary to mitigate the risk of further unauthorized access. By maintaining vigilance and implementing robust security measures, enterprises can defend against the stealthy tactics of DCSync attacks.

Cyber Security News Tags:Active Directory, attack detection, credential theft, cyber security, DCSync, Directory Service, domain controller, IT security, Kerberos, Mimikatz, network security, NTLM, password hashes, Replication Protocol, Replication Rights

Post navigation

Previous Post: Critical Vulnerability in Arista VeloCloud Exploited
Next Post: Critical Fastjson Security Flaw Exploited in Attacks

Related Posts

Telegram Users Targeted by Advanced Phishing Scheme Telegram Users Targeted by Advanced Phishing Scheme Cyber Security News
LofyStealer Targets Minecraft Players with Advanced Tactics LofyStealer Targets Minecraft Players with Advanced Tactics Cyber Security News
Node.js Developers Face Advanced Social Engineering Threat Node.js Developers Face Advanced Social Engineering Threat Cyber Security News
Four Hackers Arrested by UK Police for Attacks on M&S, Co-op and Harrods Stores Four Hackers Arrested by UK Police for Attacks on M&S, Co-op and Harrods Stores Cyber Security News
Russian Nationals Charged in M Cybercrime Case Russian Nationals Charged in $62M Cybercrime Case Cyber Security News
Arizona Woman Sentenced for Helping North Korean IT Workers by Operating Laptop Farm Arizona Woman Sentenced for Helping North Korean IT Workers by Operating Laptop Farm Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH
  • Anthropic’s Record-Breaking IPO Amid AI Safety Concerns
  • Microsoft Teams Scams: A New Cybersecurity Threat
  • AI Coding Agents at Risk from Malicious Downloads
  • Hackers Target 953 Magento Stores with Stealthy JavaScript

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH
  • Anthropic’s Record-Breaking IPO Amid AI Safety Concerns
  • Microsoft Teams Scams: A New Cybersecurity Threat
  • AI Coding Agents at Risk from Malicious Downloads
  • Hackers Target 953 Magento Stores with Stealthy JavaScript

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark