Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Web3 Developer Environments Targeted by Social Engineering Campaign Leveraging Fake Interview Software

Web3 Developer Environments Targeted by Social Engineering Campaign Leveraging Fake Interview Software

Posted on January 12, 2026January 12, 2026 By CWS

The cybersecurity panorama is experiencing a significant shift in how attackers function. Menace actors have moved away from conventional looking strategies like phishing emails and chilly outreach.

As a substitute, they’re now creating refined traps designed to make high-value targets stroll immediately into their schemes.

This new strategy, known as “inbound” social engineering, is at the moment specializing in Web3 and cryptocurrency sectors with important success charges.

The assault technique depends on a easy however efficient psychological strategy. Attackers create convincing faux corporations or copy reputable Web3 companies, then publish job openings for engaging positions by web sites like youbuidl.dev.

This methodology lowers the sufferer’s defenses as a result of job seekers imagine they’re those initiating contact.

They don’t anticipate hazard from a chance they’re pursuing. The true goal right here is the individual behind the display, who doubtless has private cryptocurrency wallets put in on their laptop.

Many victims even apply for these faux jobs utilizing their company laptops, giving attackers a direct path into main monetary establishments.

Aris Haryanto recognized and documented this rising menace after discovering the technical mechanics of how the malware operates inside these recruitment campaigns.

His evaluation revealed that the assault follows an ordinary company interview workflow to take care of legitimacy all through the method.

The execution begins when candidates obtain a professional-looking interview invitation from fraudulent domains like collaborex.ai. In the course of the video interview stage, victims are requested to obtain what seems to be a reputable assembly utility.

The malicious file, named collaborex_setup.msi, is downloaded and executed on the sufferer’s system. As soon as launched, the installer quietly initiates a Command and Management connection to the attacker’s server at IP tackle 179.43.159.106 within the background.

Command and Management Communication and Information Exfiltration

The malware’s connection to the C2 server marks the start of full system compromise. When the collaborex_setup.msi file runs, it establishes a hidden communication channel with the attacker’s infrastructure.

This connection permits the menace actors to remotely management the contaminated laptop with out the person’s data.

The attackers can then extract delicate data similar to non-public cryptocurrency keys, pockets credentials, and company information.

For builders working at crypto exchanges or DeFi protocols, this entry means direct theft of institutional funds and mental property.

The malware runs silently within the background, making it extraordinarily troublesome for traditional antivirus options to detect the malicious exercise.

The menace actors can preserve persistent entry to the system indefinitely, repeatedly monitoring and stealing information as wanted.

Comply with us on Google Information, LinkedIn, and X to Get Extra Instantaneous Updates, Set CSN as a Most popular Supply in Google.

Cyber Security News Tags:Campaign, Developer, Engineering, Environments, Fake, Interview, Leveraging, Social, Software, Targeted, Web3

Post navigation

Previous Post: LLMs in Attacker Crosshairs, Warns Threat Intel Firm
Next Post: Russia’s APT28 Targeting Energy Research, Defense Collaboration Entities

Related Posts

APT28 Exploits MSHTML Zero-Day Vulnerability Before Patch APT28 Exploits MSHTML Zero-Day Vulnerability Before Patch Cyber Security News
MEDUSA Security Testing Tool With 74 Scanners and 180+ AI Agent Security Rules MEDUSA Security Testing Tool With 74 Scanners and 180+ AI Agent Security Rules Cyber Security News
Threat Actors Exploit AI Tool to Spread Infostealer Threat Actors Exploit AI Tool to Spread Infostealer Cyber Security News
Sophisticated DevilsTongue Windows Spyware Tracking Users Globally Sophisticated DevilsTongue Windows Spyware Tracking Users Globally Cyber Security News
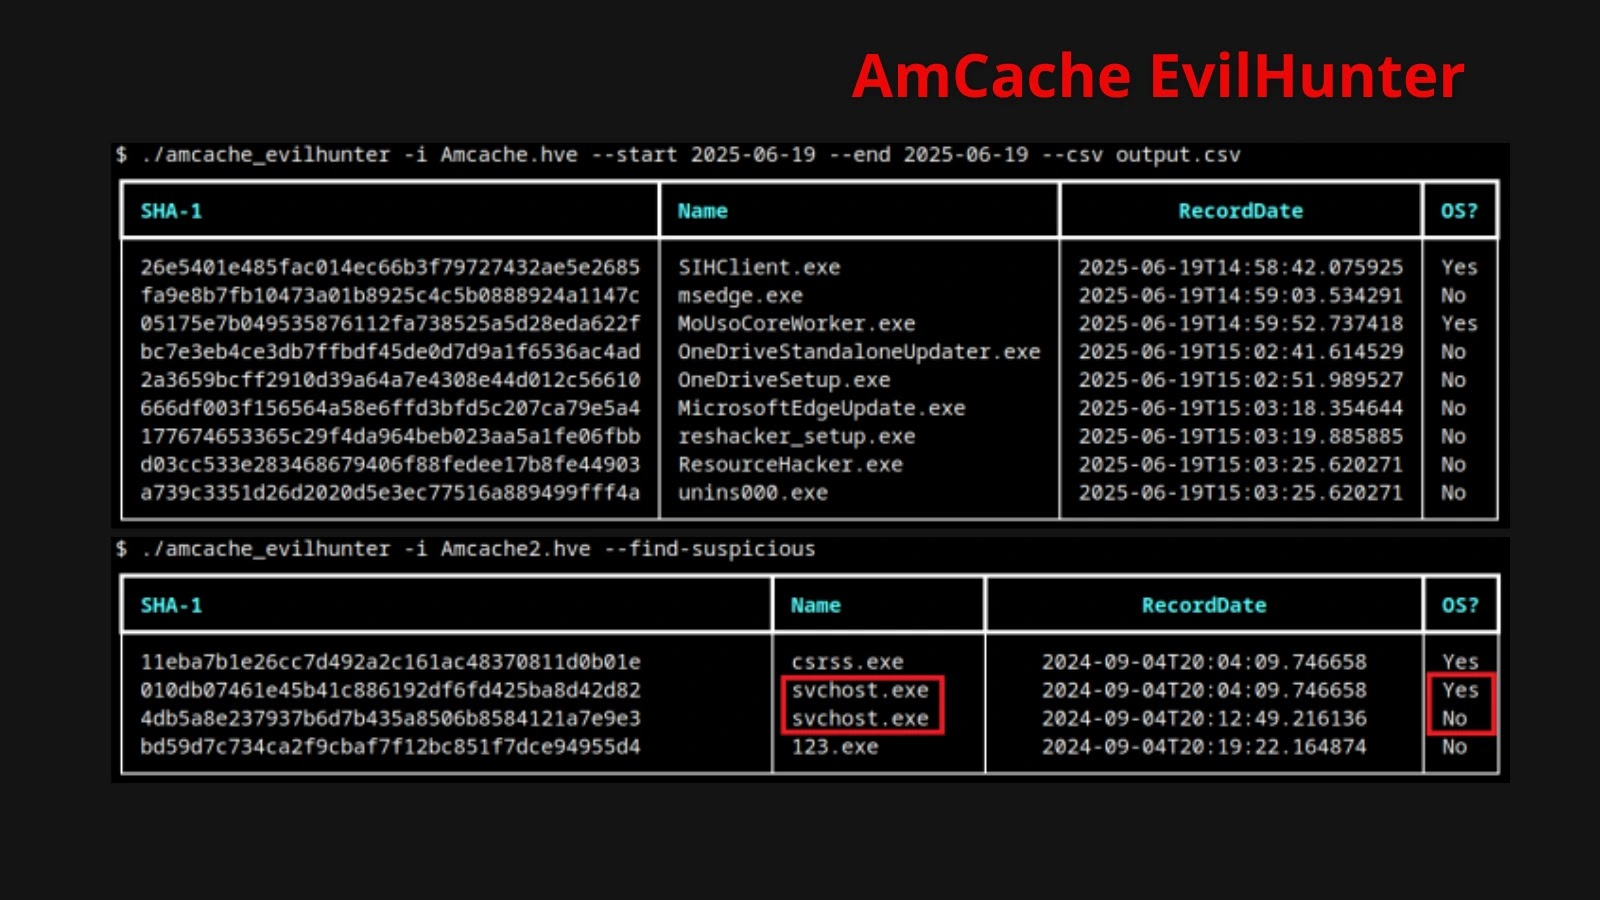
New AmCache EvilHunter Tool For Detecting Malicious Activities in Windows Systems New AmCache EvilHunter Tool For Detecting Malicious Activities in Windows Systems Cyber Security News
131 Malicious Extensions Targeting WhatsApp Used Found in Chrome Web Store 131 Malicious Extensions Targeting WhatsApp Used Found in Chrome Web Store Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers
  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark