Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Windows Remote Access Connection Manager 0-Day Vulnerability Exploited in Attacks

Windows Remote Access Connection Manager 0-Day Vulnerability Exploited in Attacks

Posted on October 15, 2025October 15, 2025 By CWS

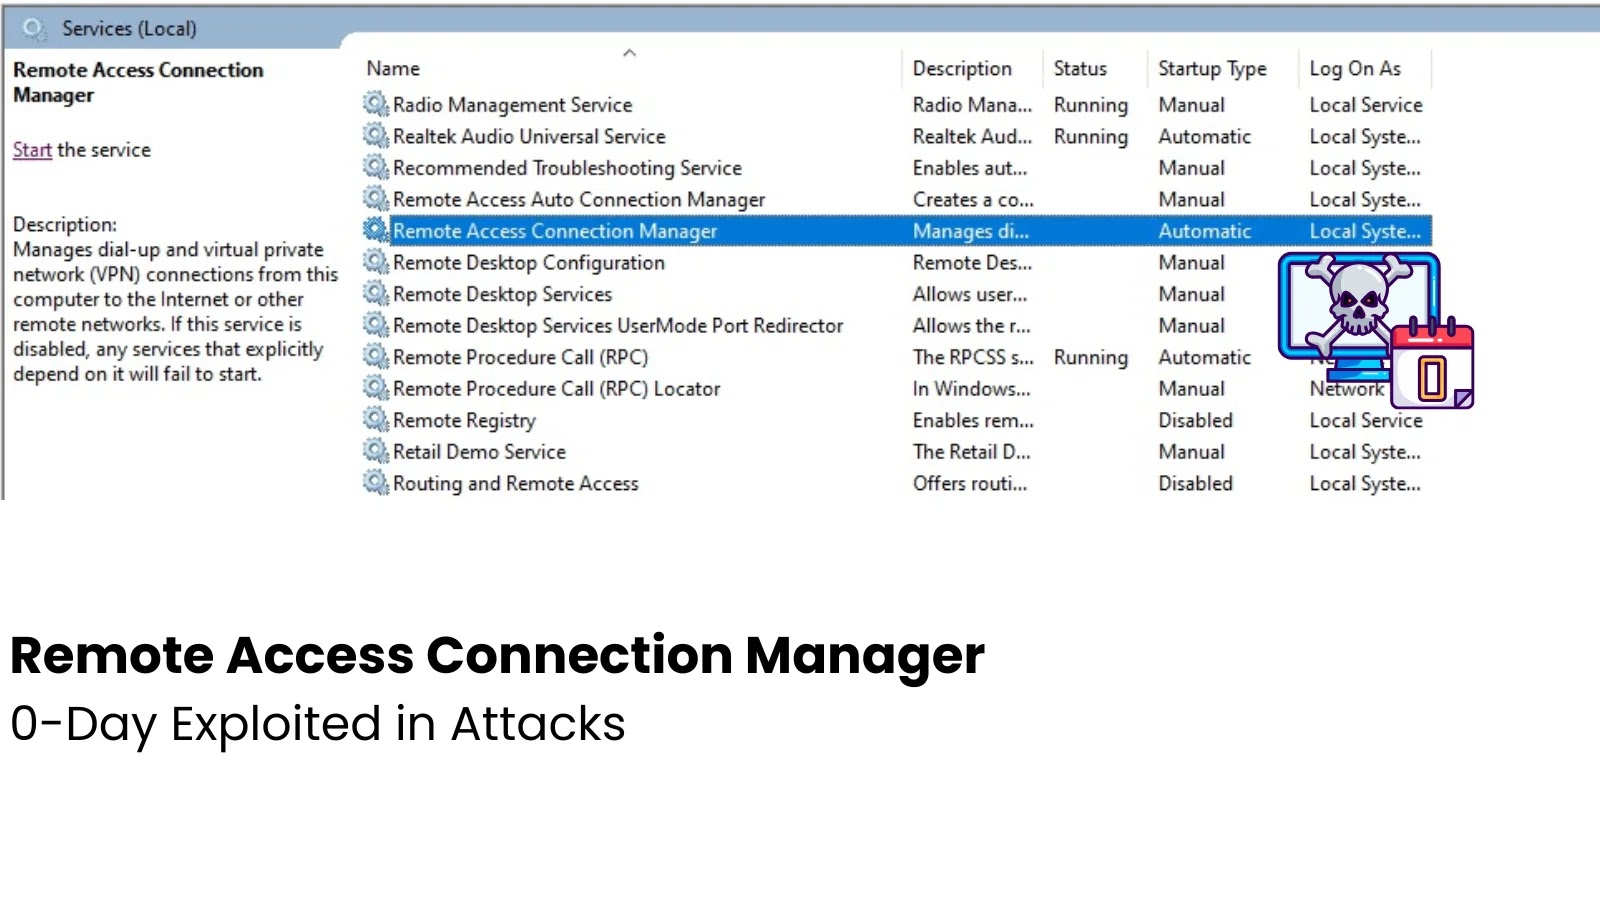
Microsoft has confirmed energetic exploitation of a vital zero-day vulnerability within the Home windows Distant Entry Connection Supervisor (RasMan) service, permitting attackers to escalate privileges and probably compromise whole techniques.

Tracked as CVE-2025-59230, the flaw stems from improper entry management, enabling low-privileged customers to realize SYSTEM-level entry.

Disclosed on October 14, 2025, the vulnerability impacts a number of Home windows variations and has already drawn consideration from risk actors focusing on enterprise environments.

The difficulty resides in RasMan, a core part dealing with distant entry connections like VPNs and dial-up. A licensed native attacker can exploit weak permission checks to govern service configurations, bypassing commonplace privilege boundaries.

With a CVSS v3.1 base rating of seven.8 (Excessive severity), it requires solely native entry and low privileges, making it a chief goal for post-compromise escalation in breaches.

Microsoft classifies it as “Exploitation Detected,” indicating real-world assaults, although specifics on affected victims stay undisclosed.

No public proof-of-concept (PoC) code has been launched, however safety researchers describe potential exploits involving registry manipulation or DLL injection into RasMan processes.

For example, an attacker would possibly leverage low-integrity processes to overwrite accessible information within the RasMan listing (e.g., C:WindowsSystem32ras), injecting malicious code that executes with elevated rights upon service restart.

This might chain with preliminary footholds from phishing or unpatched apps, amplifying injury in lateral motion eventualities.

Vulnerability Particulars

To assist speedy evaluation, the next desk summarizes key CVE-2025-59230 metrics:

MetricValueDescriptionCVSS v3.1 Base Score7.8 (Excessive)Total severity ratingAttack VectorLocal (AV:L)Requires bodily or logged-in accessAttack ComplexityLow (AC:L)Simple exploitationPrivileges RequiredLow (PR:L)Primary person account sufficesUser InteractionNone (UI:N)No sufferer engagement neededConfidentiality/Integrity/Availability ImpactHigh (C:H/I:H/A:H)Full system compromise possibleExploit MaturityFunctional (E:F)Proof-of-exploits exist in wild

Affected techniques embody Home windows 10 (variations 1809 and later), Home windows 11, and Home windows Server 2019-2025. Microsoft urges fast patching by way of the October 2025 Patch Tuesday updates, emphasizing that unpatched machines face a excessive threat from nation-state actors or ransomware teams.

Comply with us on Google Information, LinkedIn, and X for each day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:0Day, Access, Attacks, Connection, Exploited, Manager, Remote, Vulnerability, Windows

Post navigation

Previous Post: PolarEdge With Custom TLS Server Uses Custom Binary Protocol for C2 Communication
Next Post: Microsoft Patches 173 Vulnerabilities, Including Exploited Windows Flaws

Related Posts

706,000+ BIND 9 Resolver Instances Vulnerable to Cache Poisoning Exposed Online 706,000+ BIND 9 Resolver Instances Vulnerable to Cache Poisoning Exposed Online Cyber Security News
Discord Data Breach – 1.5 TB of Data and 2 Million Government ID Photos Extorted Discord Data Breach – 1.5 TB of Data and 2 Million Government ID Photos Extorted Cyber Security News
Telerik Vulnerability Chain Allows Remote Code Execution Telerik Vulnerability Chain Allows Remote Code Execution Cyber Security News
Top 10 Best Autonomous Endpoint Management Tools in 2025 Top 10 Best Autonomous Endpoint Management Tools in 2025 Cyber Security News
ShadowSyndicate Adopts Server Transition in Cyber Attacks ShadowSyndicate Adopts Server Transition in Cyber Attacks Cyber Security News
Achieving Continuous Compliance in Dynamic Threat Environments Achieving Continuous Compliance in Dynamic Threat Environments Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical SAP Flaws Allow Unauthorized System Access
  • Sparrow Malware Links Three Espionage Campaigns
  • Toyota Allegedly Targeted by BYOD Ransomware Group
  • SAP Addresses Critical Security Vulnerabilities in Recent Update
  • Critical Xen Orchestra Flaw Exploited by Hackers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark