Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Windows User Account Control Bypassed Using Character Editor to Escalate Privileges

Windows User Account Control Bypassed Using Character Editor to Escalate Privileges

Posted on August 8, 2025August 8, 2025 By CWS

A classy new method that exploits the Home windows Non-public Character Editor to bypass Person Account Management (UAC) and obtain privilege escalation with out person intervention, elevating important issues for system directors worldwide.

The assault disclosed by Matan Bahar leverages eudcedit.exeMicrosoft’s built-in Non-public Character Editor, positioned in C:WindowsSystem32, which was initially designed to create and edit Finish-Person Outlined Characters (EUDC).

These customized characters permit customers to create personalised glyphs mapped to Unicode code factors to be used in paperwork and functions. Nevertheless, safety researchers have found that this seemingly benign utility will be weaponized to bypass Home windows’ major safety gatekeeper.

App File

Home windows Person Account Management Bypassed

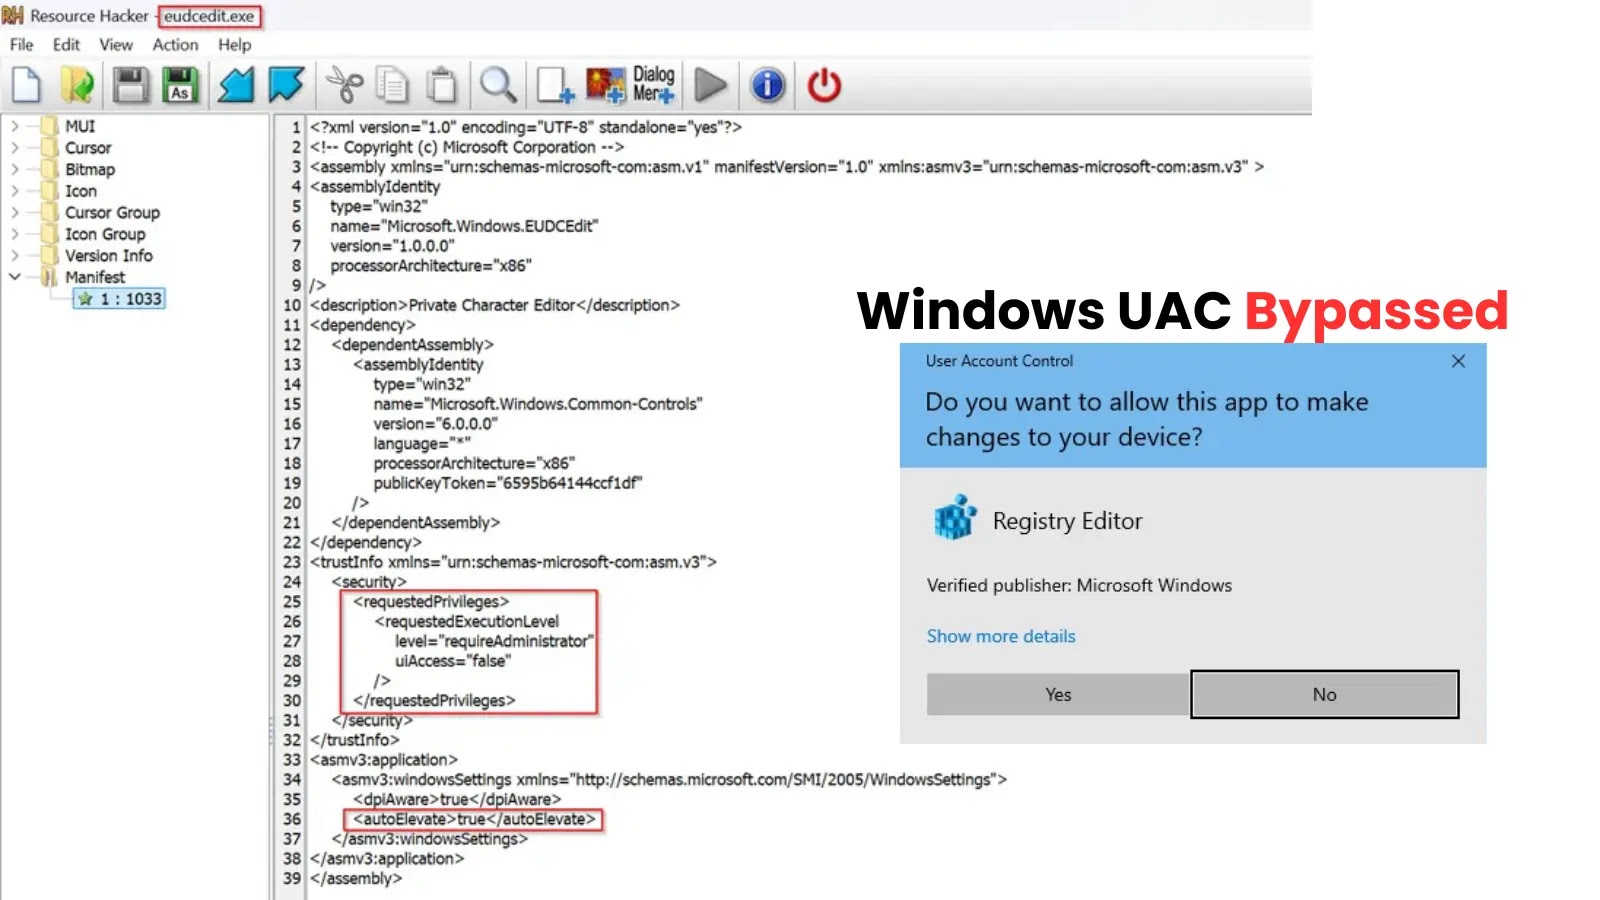
The vulnerability stems from vital configurations embedded inside eudcedit.exe’s utility manifest. Two particular metadata tags create the safety loophole:

– Instructs Home windows to run the binary with full administrative privileges

true – Permits automated elevation with out UAC prompts for trusted binaries when executed by customers within the Directors group.

This mixture proves notably harmful. When UAC is configured with permissive settings similar to “Elevate with out prompting,” Home windows robotically elevates eudcedit.exe from Medium to Excessive integrity with out displaying any safety warnings, Bahar stated.

The assault unfolds by way of a rigorously crafted sequence that exploits the applying’s file dealing with mechanisms. Attackers start by launching the Non-public Character Editor, which robotically elevates to Excessive integrity.

They then navigate to the font linking performance inside the utility interface, sometimes accessed by way of the File menu.

The vital vulnerability manifests when customers choose font linking choices and are prompted to avoid wasting information. At this juncture, the elevated eudcedit.exe course of will be manipulated to execute arbitrary instructions.

By merely getting into “PowerShell” within the file dialog, attackers can spawn a high-privilege PowerShell session that inherits the elevated integrity degree of the mum or dad course of.

powershell display

Microsoft’s method to UAC bypasses stays in line with historic patterns. Since UAC is designed as a comfort characteristic moderately than a safety boundary, the corporate sometimes doesn’t concern patches for bypass methods.

The eudcedit.exe UAC bypass demonstrates how attackers can weaponize authentic system utilities to attain malicious targets. This method’s simplicity and effectiveness make it a big concern for enterprise safety groups.

Equip your SOC with full entry to the newest risk knowledge from ANY.RUN TI Lookup that may Enhance incident response -> Get 14-day Free Trial

Cyber Security News Tags:Account, Bypassed, Character, Control, Editor, Escalate, Privileges, User, Windows

Post navigation

Previous Post: Threat Actors Weaponize Malicious Gopackages to Deliver Obfuscated Remote Payloads
Next Post: Columbia University Data Breach Impacts 860,000

Related Posts

CISA Demands Removal of Outdated Network Devices CISA Demands Removal of Outdated Network Devices Cyber Security News
Surveillance Company Using SS7 Bypass Attack to Track the User’s Location Information Surveillance Company Using SS7 Bypass Attack to Track the User’s Location Information Cyber Security News
Hackers Weaponize Compiled HTML Help to Deliver Malicious Payload Hackers Weaponize Compiled HTML Help to Deliver Malicious Payload Cyber Security News
Critical LiteLLM Vulnerability Risks Cloud Security Critical LiteLLM Vulnerability Risks Cloud Security Cyber Security News
Microsoft Teams “couldn’t connect” Error Following Recent Sidebar Update Microsoft Teams “couldn’t connect” Error Following Recent Sidebar Update Cyber Security News
Chrome Vulnerabilities Let Attackers Execute Malicious Code Remotely Chrome Vulnerabilities Let Attackers Execute Malicious Code Remotely Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Cisco Warns of Severe Email Gateway Security Flaw
  • Critical Cisco Email Gateway Vulnerability Exploited
  • Critical Linux Kernel Flaw Allows Privilege Escalation
  • New Cyclops Blink Malware Targets Corporate Networks
  • WhatsApp Tests New Feature to Lock Chats on Primary Phone

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Cisco Warns of Severe Email Gateway Security Flaw
  • Critical Cisco Email Gateway Vulnerability Exploited
  • Critical Linux Kernel Flaw Allows Privilege Escalation
  • New Cyclops Blink Malware Targets Corporate Networks
  • WhatsApp Tests New Feature to Lock Chats on Primary Phone

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark