Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Recent GeoServer Vulnerability Exploited in Attacks

Recent GeoServer Vulnerability Exploited in Attacks

Posted on December 12, 2025December 12, 2025 By CWS

The US cybersecurity company CISA on Thursday warned that menace actors have been exploiting a current OSGeo GeoServer vulnerability in assaults.

Tracked as CVE-2025-58360 (CVSS rating of 9.8), the critical-severity bug is described as an XML Exterior Entity (XXE) challenge that would enable attackers to entry arbitrary information, conduct SSRF assaults, or trigger denial-of-service (DoS) situations.

“The appliance accepts XML enter via a particular endpoint /geoserver/wms operation GetMap. Nonetheless, this enter just isn’t sufficiently sanitized or restricted, permitting an attacker to outline exterior entities throughout the XML request,” GeoServer’s maintainers stated final month.

Patches for the safety defect had been included in GeoServer model 2.28.1, which was introduced on November 25. The replace additionally addressed a medium-severity XSS vulnerability within the software (tracked as CVE-2025-21621).

Packages impacted by the difficulty embody docker.osgeo.org/geoserver, org.geoserver.internet:gs-web-app (Maven), and org.geoserver:gs-wms (Maven), which ought to be up to date to variations 2.25.6, 2.26.3, or 2.27.0.

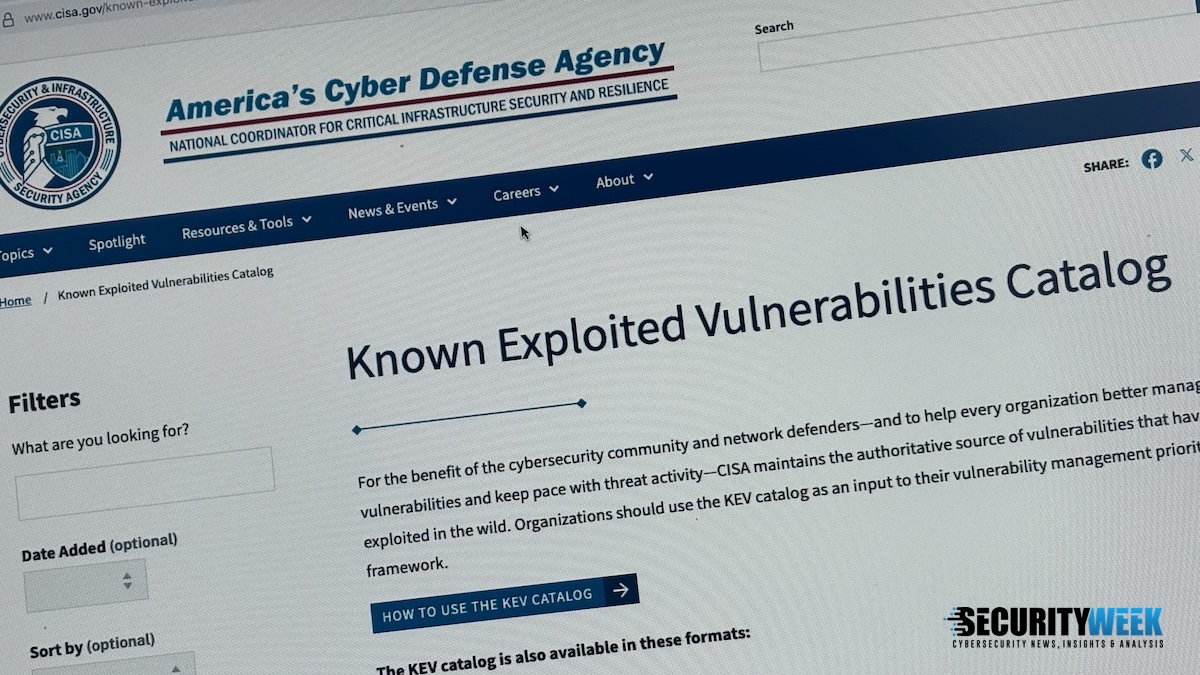
On Thursday, CISA added CVE-2025-58360 to its Recognized Exploited Vulnerabilities (KEV) record, with out offering particulars on the noticed in-the-wild exploitation.

Nonetheless, primarily based on advisories from cybersecurity agency Wiz and the Canadian Cyber Centre, an exploit for the bug has existed since late November.

Per Binding Operational Directive (BOD) 22-01, federal companies have three weeks to establish and patch weak GeoServer situations inside their environments.Commercial. Scroll to proceed studying.

It’s price noting that CVE-2025-58360 is the third exploited GeoServer vulnerability documented by CISA this yr. In June, it warned of CVE-2022-24816’s exploitation and in July it warned that CVE-2024-36401 had been focused in assaults.

In September, CISA revealed that, 4 days earlier than its July alert, a menace actor exploited the year-old GeoServer defect to compromise a federal company.

Associated: Unpatched Gogs Zero-Day Exploited for Months

Associated: Google Patches Mysterious Chrome Zero-Day Exploited within the Wild

Associated: Microsoft Patches 57 Vulnerabilities, Three Zero-Days

Associated: Android Zero-Days Patched in December 2025 Safety Replace
Security Week News Tags:Attacks, Exploited, GeoServer, Vulnerability

Post navigation

Previous Post: MITRE Releases 2025 List of Top 25 Most Dangerous Software Vulnerabilities
Next Post: CyberVolk Hackers Group With New VolkLocker Payloads Attacks both Linux and Windows Systems

Related Posts

Critical VS Code Flaw Enables GitHub Token Theft Critical VS Code Flaw Enables GitHub Token Theft Security Week News
Supply Chain Attack Hits SAP NPM Packages Supply Chain Attack Hits SAP NPM Packages Security Week News
Russian APT Hits Ukrainian Government With New Malware via Signal Russian APT Hits Ukrainian Government With New Malware via Signal Security Week News
Data Breach at Centers Laboratory Affects Over 540,000 Data Breach at Centers Laboratory Affects Over 540,000 Security Week News
Alumni, Student, and Staff Information Stolen From Harvard University Alumni, Student, and Staff Information Stolen From Harvard University Security Week News
OpenAI Enhances AI Security with New Protocols OpenAI Enhances AI Security with New Protocols Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark