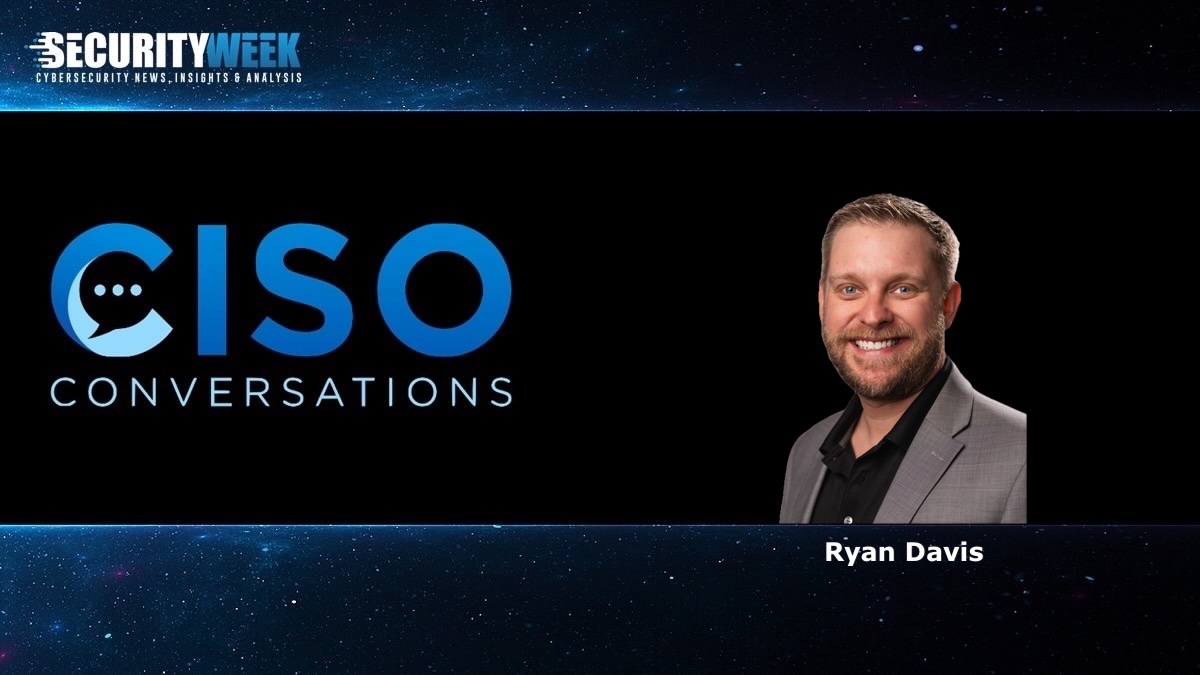
Ryan Davis, the Chief Information Security Officer (CISO) at New Charter Technologies, has crafted a remarkable career path that began in the realm of hacking. His early fascination with computers set the stage for his future endeavors in cybersecurity, where his skills and insights now contribute to the protection of business information systems.
The Early Years: A Path to Cybersecurity
Growing up in a household equipped with multiple personal computers, Davis developed a deep interest in technology. His mother’s secretarial college provided him with ample opportunities to experiment with these machines, fostering a curiosity that led him beyond conventional uses. As the internet emerged, Davis expanded his knowledge through online forums, driven by a desire to push systems to their limits without malicious intent.
During his high school years, Davis discovered vulnerabilities within the school’s network. Choosing to report these issues to the system administrator, he demonstrated a strong ethical foundation. This decision marked a pivotal moment in his journey, reinforcing his belief in the innate morality that guides individuals toward constructive paths.
A Professional Journey in Cybersecurity
Following high school, Davis pursued higher education in computer networking and information security. His academic achievements led to a position at MIT Lincoln Laboratory, where he applied his skills in developing advanced security technologies. After several years at MIT, Davis transitioned to Veracode in 2012, where he managed and expanded the company’s security programs.
During his time at Veracode, Davis engaged with the internal CISO, setting his sights on a similar role. This ambition materialized in 2019 when he became Veracode’s CISO. His career continued to evolve as he took on the CISO role at NS1, later acquired by IBM, before joining New Charter Technologies.
Leadership and Team Building
Davis emphasizes the importance of balancing technical expertise with business acumen in the CISO role. He views the position as a business enabler, requiring a blend of skills to protect not just information, but the entire organization. Davis believes a successful CISO must understand both technical and business needs to effectively communicate with executive teams.
Building a cohesive security team is crucial to Davis, who advocates for diversity and a mix of skills. He believes that varied perspectives enhance problem-solving, particularly in the dynamic field of cybersecurity. Davis’s leadership philosophy centers on empowering team members and fostering an environment of trust and collaboration.
Addressing Challenges and Mentoring
Recognizing the risk of burnout in high-pressure security roles, Davis stresses the necessity of maintaining a work-life balance. He advocates for trust in one’s team and systems to avoid constant stress. Additionally, Davis sees mentorship as a key component of professional growth, both in his journey and for those he guides.
For Davis, cybersecurity is an ever-evolving field where the unknown presents constant challenges. He dedicates time to understanding emerging technologies and potential threats, acknowledging that security must continuously adapt to new developments. This vigilant approach is what he believes defines the intersection of security and reality.