Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Executive Order to Secure US Power Grid from Foreign Threats

Executive Order to Secure US Power Grid from Foreign Threats

Posted on August 27, 2026 By CWS

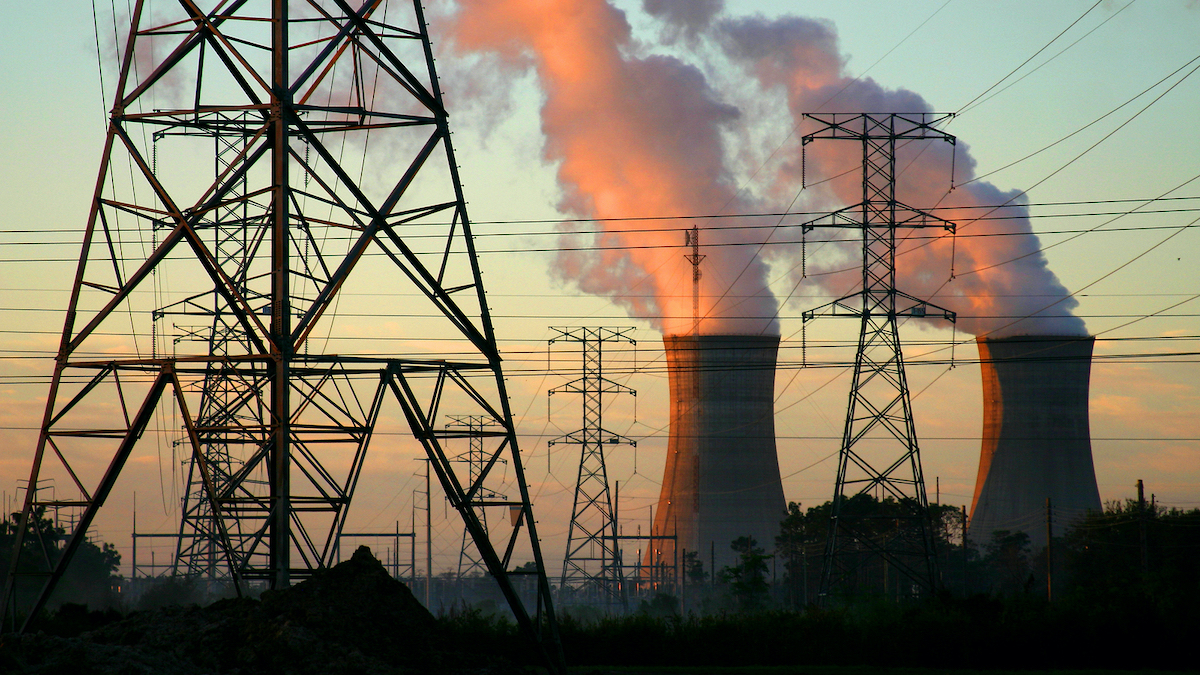
The United States has taken a significant step toward safeguarding its power grid infrastructure. On Wednesday, President Trump signed Executive Order 14420, declaring a national emergency aimed at addressing vulnerabilities within the bulk power system that stem from foreign-made electrical equipment. This executive action seeks to prevent potential threats to the nation’s energy security.

Addressing Growing Technological Demands

The order highlights the rapid advancements in areas such as data centers, artificial intelligence, and defense manufacturing, which have amplified the importance of a reliable power grid. Officials have expressed concerns over the dependency on foreign supply chains, which could be exploited through built-in backdoors, risking unauthorized access or disruptions.

Focusing on critical infrastructure, the order pertains to bulk-power system components that operate at transmission lines rated 69 kilovolts or higher. Local electricity distribution networks, however, are not included in this directive. Technologies under scrutiny include transformers, energy storage systems, and industrial control systems, along with their associated software and remote access functionalities.

Prohibitions and Future Implications

By August 26, 2026, the acquisition or installation of foreign-produced bulk power equipment will be restricted if it involves designated entities posing security risks. These measures aim to counteract potential sabotage, unauthorized access, and supply chain disruptions.

Although no specific countries are named, the order closely resembles a previous directive from 2020 targeting Chinese entities. This points to a strategic shift in addressing upstream supply chain risks and embedded hardware vulnerabilities, emphasizing the need for robust security measures.

Ensuring Grid Security and Operational Continuity

For components installed before this new order, the Department of Energy (DOE) is empowered to enforce security protocols. In collaboration with defense and intelligence officials, the DOE can mandate actions such as identifying, isolating, or replacing vulnerable components to ensure the grid’s operational integrity.

To maintain continuity, energy authorities might establish mitigation agreements or release an approved list of equipment and vendors exempt from these restrictions. This ongoing effort underscores the critical need to secure the nation’s energy infrastructure against potential foreign threats.

As the US navigates these new security measures, the focus remains on balancing technological advancements with the imperative of safeguarding national security. This executive order represents a proactive approach to fortifying the nation’s energy infrastructure against evolving global threats.
Security Week News Tags:bulk power system, critical infrastructure, DOE regulations, energy infrastructure, energy policy, executive order, foreign threats, national security, power grid security, supply chain risks, Trump administration, US power grid

Post navigation

Previous Post: Amazon Kiro Vulnerability Risks Data Exposure
Next Post: Australian Duo Arrested for Massive TeamPCP Cyber Attacks

Related Posts

Microsoft’s Project Ire Autonomously Reverse Engineers Software to Find Malware Microsoft’s Project Ire Autonomously Reverse Engineers Software to Find Malware Security Week News
FBI Security Breach, Iranian Camera Hack, and More Cyber Developments FBI Security Breach, Iranian Camera Hack, and More Cyber Developments Security Week News
LLMs in Attacker Crosshairs, Warns Threat Intel Firm LLMs in Attacker Crosshairs, Warns Threat Intel Firm Security Week News
Analog Devices Reports Cybersecurity Breach Analog Devices Reports Cybersecurity Breach Security Week News
SAP Patches Another Critical NetWeaver Vulnerability SAP Patches Another Critical NetWeaver Vulnerability Security Week News
BTMOB Android Malware Threatens Full Device Control BTMOB Android Malware Threatens Full Device Control Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks
  • SAP Addresses Critical Vulnerabilities in NetWeaver and S/4HANA
  • Microsoft Fixes Record 1,413 Vulnerabilities Including Exploited Bug

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks
  • SAP Addresses Critical Vulnerabilities in NetWeaver and S/4HANA
  • Microsoft Fixes Record 1,413 Vulnerabilities Including Exploited Bug

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark