Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
6,500 Axis Servers Expose Remoting Protocol, 4,000 in U.S. Vulnerable to Exploits

6,500 Axis Servers Expose Remoting Protocol, 4,000 in U.S. Vulnerable to Exploits

Posted on August 7, 2025August 7, 2025 By CWS

Aug 07, 2025Ravie LakshmananVulnerability / Risk Intelligence
Cybersecurity researchers have disclosed a number of safety flaws in video surveillance merchandise from Axis Communications that, if efficiently exploited, might expose them to takeover assaults.
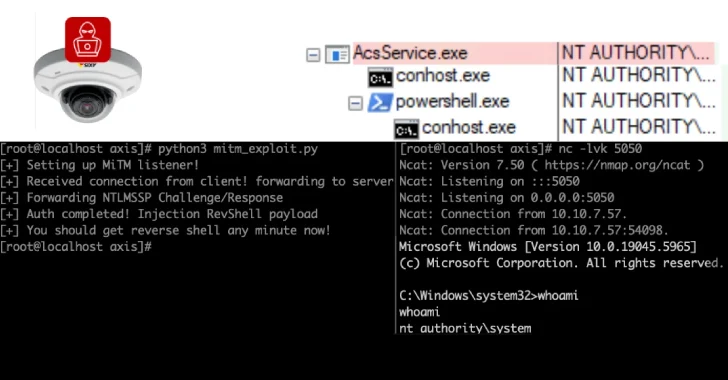
“The assault ends in pre-authentication distant code execution on Axis Gadget Supervisor, a server used to configure and handle fleets of cameras, and the Axis Digital camera Station, shopper software program used to view digital camera feeds,” Claroty researcher Noam Moshe stated.
“Moreover, utilizing web scans of uncovered Axis.Remoting providers, an attacker can enumerate weak servers and shoppers, and perform granular, extremely focused assaults.”

The listing of recognized flaws is beneath –

CVE-2025-30023 (CVSS rating: 9.0) – A flaw within the communication protocol used between shopper and server that would result in an authenticated person performing a distant code execution assault (Mounted in Digital camera Station Professional 6.9, Digital camera Station 5.58, and Gadget Supervisor 5.32)
CVE-2025-30024 (CVSS rating: 6.8) – A flaw within the communication protocol used between shopper and server that may very well be leveraged to execute an adversary-in-the-middle (AitM) assault (Mounted in Gadget Supervisor 5.32)
CVE-2025-30025 (CVSS rating: 4.8) – A flaw within the communication protocol used between the server course of and the service management that would result in an area privilege escalation (Mounted in Digital camera Station Professional 6.8 and Gadget Supervisor 5.32)
CVE-2025-30026 (CVSS rating: 5.3) – A flaw within the Axis Digital camera Station Server that would result in an authentication bypass (Mounted in Digital camera Station Professional 6.9 and Digital camera Station 5.58)

Profitable exploitation of the aforementioned vulnerabilities might permit an attacker to imagine an AitM place between the Digital camera Station and its shoppers, successfully making it attainable to change requests/responses and execute arbitrary actions on both the server or shopper techniques. There isn’t a proof that the problems have been exploited within the wild.

Claroty stated it discovered greater than 6,500 servers that expose the proprietary Axis.Remoting protocol and its providers over the web, out of which practically 4,000 of them are situated within the U.S.
“Profitable exploits give attackers system-level entry on the interior community and the power to manage every of the cameras inside a selected deployment,” Moshe famous. “Feeds may be hijacked, watched, and/or shut down. Attackers can exploit these safety points to bypass authentication to the cameras and acquire pre-authentication distant code execution on the gadgets.”
The Hacker News Tags:Axis, Exploits, Expose, Protocol, Remoting, Servers, U.S, Vulnerable

Post navigation

Previous Post: 10 Best Data Loss Prevention Software in 2025
Next Post: Microsoft Discloses Exchange Server Flaw Enabling Silent Cloud Access in Hybrid Setups

Related Posts

RVTools Official Site Hacked to Deliver Bumblebee Malware via Trojanized Installer RVTools Official Site Hacked to Deliver Bumblebee Malware via Trojanized Installer The Hacker News
GitLab Email Vulnerability Exposes Security Risks GitLab Email Vulnerability Exposes Security Risks The Hacker News
How to Protect Your Backups How to Protect Your Backups The Hacker News
Microsoft Alerts on WhatsApp Malware Using UAC Bypass Microsoft Alerts on WhatsApp Malware Using UAC Bypass The Hacker News
Git Addresses Critical Vulnerability in Recursive Clone Operations Git Addresses Critical Vulnerability in Recursive Clone Operations The Hacker News
From MCPs and Tool Access to Shadow API Key Sprawl From MCPs and Tool Access to Shadow API Key Sprawl The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • GhostFrame Malware Threatens VMware ESXi Servers
  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • GhostFrame Malware Threatens VMware ESXi Servers
  • Hackers Exploit Outlook Flaw to Steal Authentication Data
  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark