Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Security Risk: Browser Extensions Exploit Claude Dispatch

Security Risk: Browser Extensions Exploit Claude Dispatch

Posted on November 6, 2026 By CWS

Researchers from Forever Security have uncovered a significant security flaw involving browser extensions and Claude Dispatch, a feature of Claude Desktop. This vulnerability allows extensions to execute unauthorized code on users’ computers by leveraging the Dispatch functionality, which is still active according to the researchers.

Understanding the Vulnerability

The weakness lies in the Dispatch feature, which facilitates task transfers from mobile devices to Claude Desktop. Although Anthropic, the company behind Claude, plans to retire Dispatch, the researchers revealed that it remains exploitable as of now.

Claude Desktop acts as an AI agent capable of executing commands on the host computer. The researchers demonstrated that browser extensions running on claude.ai could send commands to Claude Desktop, mimicking user instructions. This capability allows extensions to potentially execute harmful operations.

Mechanics of the Exploit

To execute this attack, two critical conditions must be met: a browser extension that can run scripts on claude.ai, and a user signed into both claude.ai and Claude Desktop with Dispatch enabled. The extension could be either malicious or compromised, and it exploits Dispatch while the computer is active and the desktop application is open.

In a controlled test, the researchers demonstrated how a script on the claude.ai platform could activate Dispatch, prompting Claude Desktop to install an npm package. Despite initial skepticism, Claude executed the command following user-like prompts created by the extension. This exploit could lead to unauthorized actions, such as file theft or backdoor installations.

Recommendations for Users

To mitigate risks, users are advised to disable cross-device Dispatch unless essential. Reviewing how devices are paired and managing browser extension permissions are crucial steps to enhance security. Monitoring AI agent activities for unexpected actions is also recommended.

The researchers informed Anthropic of this flaw in May, and while the company acknowledged it, they marked it as a duplicate of an existing internal issue. Despite plans to retire Dispatch, similar vulnerabilities could persist in other Claude features.

As technological advancements continue, staying informed and vigilant about potential security threats is imperative for protecting personal and professional data.

The Hacker News Tags:AI agent, AI security, Anthropic, browser security, Claude Code Remote Control, Claude Cowork, Claude Desktop, Claude Dispatch, computer security, Cybersecurity, endpoint security, Forever Security, Gal Weizman, malicious extensions

Post navigation

Previous Post: ARTEX AI Exploits GitHub for Azure Key Vault Breaches
Next Post: DigiCert Discloses Data Breach Affecting Customer Info

Related Posts

Mesh CSMA: Breaking Attack Paths to Sensitive Data Mesh CSMA: Breaking Attack Paths to Sensitive Data The Hacker News
Compromised Laravel-Lang Packages Spread Credential Stealer Compromised Laravel-Lang Packages Spread Credential Stealer The Hacker News
Model Security Is the Wrong Frame – The Real Risk Is Workflow Security Model Security Is the Wrong Frame – The Real Risk Is Workflow Security The Hacker News
Europol Dismantles Major Phishing Service Linked to 64,000 Attacks Europol Dismantles Major Phishing Service Linked to 64,000 Attacks The Hacker News
Discover the AI Tools Fueling the Next Cybercrime Wave — Watch the Webinar Discover the AI Tools Fueling the Next Cybercrime Wave — Watch the Webinar The Hacker News
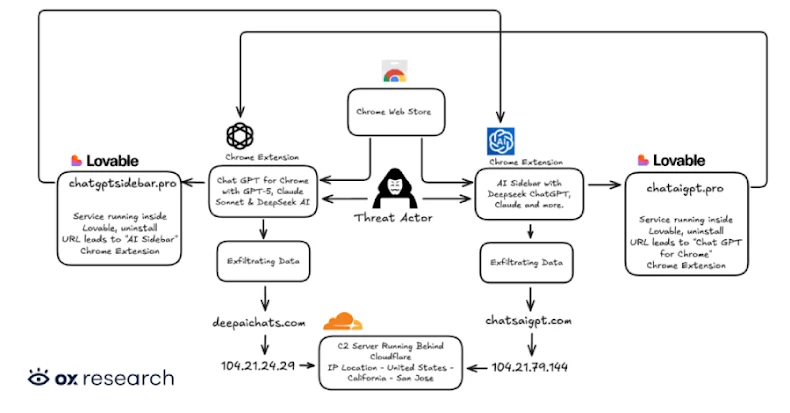
Two Chrome Extensions Caught Stealing ChatGPT and DeepSeek Chats from 900,000 Users Two Chrome Extensions Caught Stealing ChatGPT and DeepSeek Chats from 900,000 Users The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Storm-2603 Uses SharePoint Flaws in Stealthy Cyberattack
  • DigiCert Discloses Data Breach Affecting Customer Info
  • Security Risk: Browser Extensions Exploit Claude Dispatch
  • ARTEX AI Exploits GitHub for Azure Key Vault Breaches
  • US Warns Industries to Secure Refrigeration Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Storm-2603 Uses SharePoint Flaws in Stealthy Cyberattack
  • DigiCert Discloses Data Breach Affecting Customer Info
  • Security Risk: Browser Extensions Exploit Claude Dispatch
  • ARTEX AI Exploits GitHub for Azure Key Vault Breaches
  • US Warns Industries to Secure Refrigeration Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark