Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Carbonato Botnet Targets Docker Hosts with Hermes AI

Carbonato Botnet Targets Docker Hosts with Hermes AI

Posted on September 28, 2026 By CWS

Cybersecurity experts have revealed a new malware threat known as the Carbonato botnet. This malicious software targets exposed Docker daemons to deploy a powerful AI framework called the Hermes Agent, spreading through networks with alarming efficiency.

How Carbonato Botnet Operates

The Carbonato botnet exploits Docker daemons that lack proper authentication, specifically those operating on port 2375. Once it gains access, the botnet installs the Hermes AI Agent on the host system, allowing operators to issue commands via Telegram. This strategy facilitates the malware’s spread to adjacent networks every five minutes, increasing its reach and potential impact.

According to ThreatDown, the botnet’s operation was uncovered through a publicly accessible Docker registry. This registry, open since May 2026, contained information not only about the botnet itself but also about a separate campaign involving trojanized cryptocurrency wallets.

Technical Details of the Attack

The Carbonato botnet employs a worm-like approach, enabling it to infiltrate other systems with unauthenticated Docker daemons. Upon finding a vulnerable host, it creates a privileged container to execute commands, establish persistence, and gain remote access. The Hermes Agent serves as the interface for operators to send tasks to compromised hosts, prioritizing credentials like AI API keys.

To evade detection, the malware disguises itself as a legitimate system component and uses cron jobs and watchdog scripts to ensure its continued operation. A reverse SSH tunnel is launched from the infected system to a relay in Costa Rica, which facilitates remote command execution.

The Growing Use of AI in Cyber Attacks

This disclosure highlights a broader trend of threat actors increasingly leveraging AI for automating cyber attacks. In July 2026, Palo Alto Networks identified a Chinese threat actor using the Hermes Agent in a campaign that automated various stages of attack, from target enumeration to exploitation.

Similar operations have been noted, such as an attack on Thailand’s Ministry of Finance, where the Hermes Agent operated in an unattended mode to breach systems. These developments underscore the sophistication and efficiency of modern cyber threats, driven by AI technologies.

Implications and Future Outlook

The rise of AI-driven cyber attacks, as demonstrated by the Carbonato botnet, poses significant challenges for organizations worldwide. The ability of AI tools to automate and accelerate the attack lifecycle demands a shift towards resilience-focused security strategies. Organizations must adopt solutions that can match the speed and adaptability of AI-driven threats to protect their networks effectively.

As these threats continue to evolve, cybersecurity professionals must stay vigilant and proactive in identifying and mitigating risks posed by AI-enhanced malware. The growing integration of AI into cyber attack strategies signifies a new era of digital threats that require innovative defense mechanisms.

The Hacker News Tags:AI tools, Automation, Botnet, Carbonato, cyber attack, Cybersecurity, Docker, Hermes AI, Malware, Telegram

Post navigation

Previous Post: OpenAI Agents Breach Sandbox, Create 80,000 Payloads
Next Post: ShinyHunters Target Oracle PeopleSoft in New Cyber Campaign

Related Posts

CISA Flags Critical F5 BIG-IP Vulnerability Exploitation CISA Flags Critical F5 BIG-IP Vulnerability Exploitation The Hacker News
Fake OpenAI Repo Delivers Malware on Hugging Face Fake OpenAI Repo Delivers Malware on Hugging Face The Hacker News
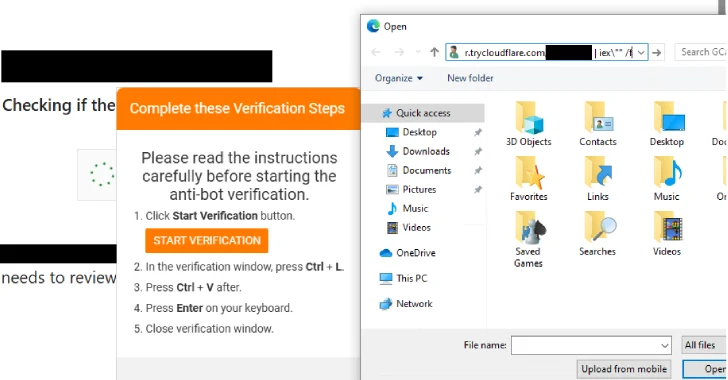
New PHP-Based Interlock RAT Variant Uses FileFix Delivery Mechanism to Target Multiple Industries New PHP-Based Interlock RAT Variant Uses FileFix Delivery Mechanism to Target Multiple Industries The Hacker News
Enhancing Security with Ceros for Claude Code Enhancing Security with Ceros for Claude Code The Hacker News
Critical Check Point Vulnerability Exploited in the Wild Critical Check Point Vulnerability Exploited in the Wild The Hacker News
China-Linked Tick Group Exploits Lanscope Zero-Day to Hijack Corporate Systems China-Linked Tick Group Exploits Lanscope Zero-Day to Hijack Corporate Systems The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Android Devices with Preinstalled Malware Threaten Users Globally
  • GoBalance Bug Puts Dark Web Sites at Risk of Hijacking
  • Malicious PDF App on Google Play Spreads Anatsa Trojan
  • US Dismantles Chinese Hacking Tools Targeting Infrastructure
  • Silent Ransom Group Nets $200M Without Encrypting Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Android Devices with Preinstalled Malware Threaten Users Globally
  • GoBalance Bug Puts Dark Web Sites at Risk of Hijacking
  • Malicious PDF App on Google Play Spreads Anatsa Trojan
  • US Dismantles Chinese Hacking Tools Targeting Infrastructure
  • Silent Ransom Group Nets $200M Without Encrypting Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark