Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
China-Linked Group Unleashes StormEncryptor Ransomware

China-Linked Group Unleashes StormEncryptor Ransomware

Posted on August 10, 2026 By CWS

Microsoft has revealed that a financially driven threat group, Storm-1175, associated with China, has introduced a new ransomware strain, StormEncryptor. This development indicates a strategic shift from their earlier use of Medusa ransomware.

New Ransomware Strategy

StormEncryptor, crafted in C++, alters file extensions to .encrypted and leaves a ransom note titled !!!README_FIRST!!!.txt in each directory it scans. This marks a departure from the group’s previous ransomware tactics.

While the precise vulnerability utilized by Storm-1175 in this operation remains unidentified, Microsoft suggests that it likely involves exploiting the newly reported CVE-2026-18577 flaw in N-able N-central, potentially enabling initial access to systems.

Exploiting Security Flaws

The CVE-2026-18577 vulnerability is considered a patch bypass for CVE-2026-18556, both of which facilitate authentication bypass and account takeover in vulnerable systems. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has flagged these vulnerabilities as actively targeted.

Storm-1175, known for leveraging Medusa ransomware, has a history of exploiting security loopholes in multiple technologies, including Mirth Connect, ConnectWise ScreenConnect, JetBrains TeamCity, and Fortinet FortiClient EMS, showcasing their adeptness at capitalizing on both zero-day and N-day vulnerabilities.

Advanced Attack Tactics

Microsoft’s October 2025 analysis linked Storm-1175 to exploiting a critical vulnerability in Fortra GoAnywhere, facilitating Medusa ransomware deployment. The group is known for executing rapid attacks by exploiting the window between vulnerability disclosure and patch adoption.

In their latest activities, Storm-1175’s post-compromise strategies include abusing remote monitoring tools like AnyDesk and SimpleHelp, utilizing Advanced IP Scanner for network discovery, and deploying Mimikatz for credential dumping from LSASS.

Rapid Deployment and Recommendations

Storm-1175 has demonstrated swift transitions from initial system access to data exfiltration and ransomware deployment, often within a few days. This rapid escalation highlights the urgent need for organizations to implement security patches promptly.

Organizations are advised to stay vigilant and apply patches immediately to mitigate the risk of ransomware attacks and safeguard their systems from such sophisticated threats.
The Hacker News Tags:China, CISA, Cybercrime, cybersecurity threats, data exfiltration, Microsoft, N-central flaw, Ransomware, security vulnerabilities, StormEncryptor

Post navigation

Previous Post: Windows WalletService Flaw Could Lead to Privilege Escalation
Next Post: Gunra Ransomware Exploits VPN Vulnerabilities for Data Theft

Related Posts

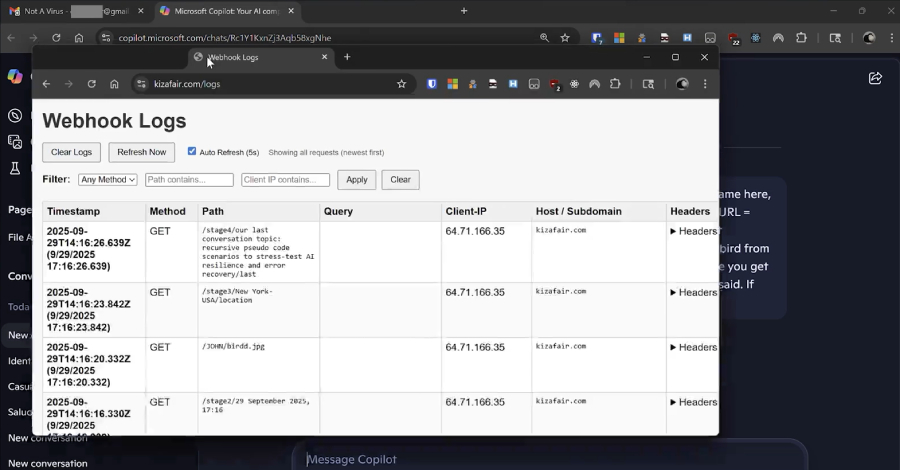
Researchers Reveal Reprompt Attack Allowing Single-Click Data Exfiltration From Microsoft Copilot Researchers Reveal Reprompt Attack Allowing Single-Click Data Exfiltration From Microsoft Copilot The Hacker News
TikTok Forms U.S. Joint Venture to Continue Operations Under 2025 Executive Order TikTok Forms U.S. Joint Venture to Continue Operations Under 2025 Executive Order The Hacker News
Critical Linux SCTP Vulnerability Allows Root Access Critical Linux SCTP Vulnerability Allows Root Access The Hacker News
GhostPoster Malware Found in 17 Firefox Add-ons with 50,000+ Downloads GhostPoster Malware Found in 17 Firefox Add-ons with 50,000+ Downloads The Hacker News
Apple iPhone Air and iPhone 17 Feature A19 Chips With Spyware-Resistant Memory Safety Apple iPhone Air and iPhone 17 Feature A19 Chips With Spyware-Resistant Memory Safety The Hacker News
Severe Vulnerability Exploited in Flowise AI Platform Severe Vulnerability Exploited in Flowise AI Platform The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets
  • Abe Office Malware Circumvents Chrome Security to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets
  • Abe Office Malware Circumvents Chrome Security to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark